What Is Joomla SQL Injection?
Joomla SQL injection happens when data controlled by a request is allowed to change the intended structure of a database query instead of being treated only as data. MITRE classifies this weakness as CWE-89, Improper Neutralization of Special Elements used in an SQL Command.
The issue is not that Joomla applications use SQL. Database queries are fundamental to the CMS. The vulnerability appears when code builds those queries incorrectly.
A vulnerable path might begin with a URL parameter, form field, API parameter, sort option, selected record ID, or extension-specific AJAX request. Joomla then routes that input into a component or extension. If the value eventually reaches a query clause without appropriate binding, casting, or validation for its SQL context, it may influence the query itself.
That distinction matters. Filtering general web input is not the same thing as making a database query safe.
For a broader assessment of the platform itself, see ScanTitan’s Joomla security assessment. SQL injection is a specific implementation weakness, not evidence that every Joomla installation is inherently vulnerable.
Where Does SQL Injection Happen in Joomla?
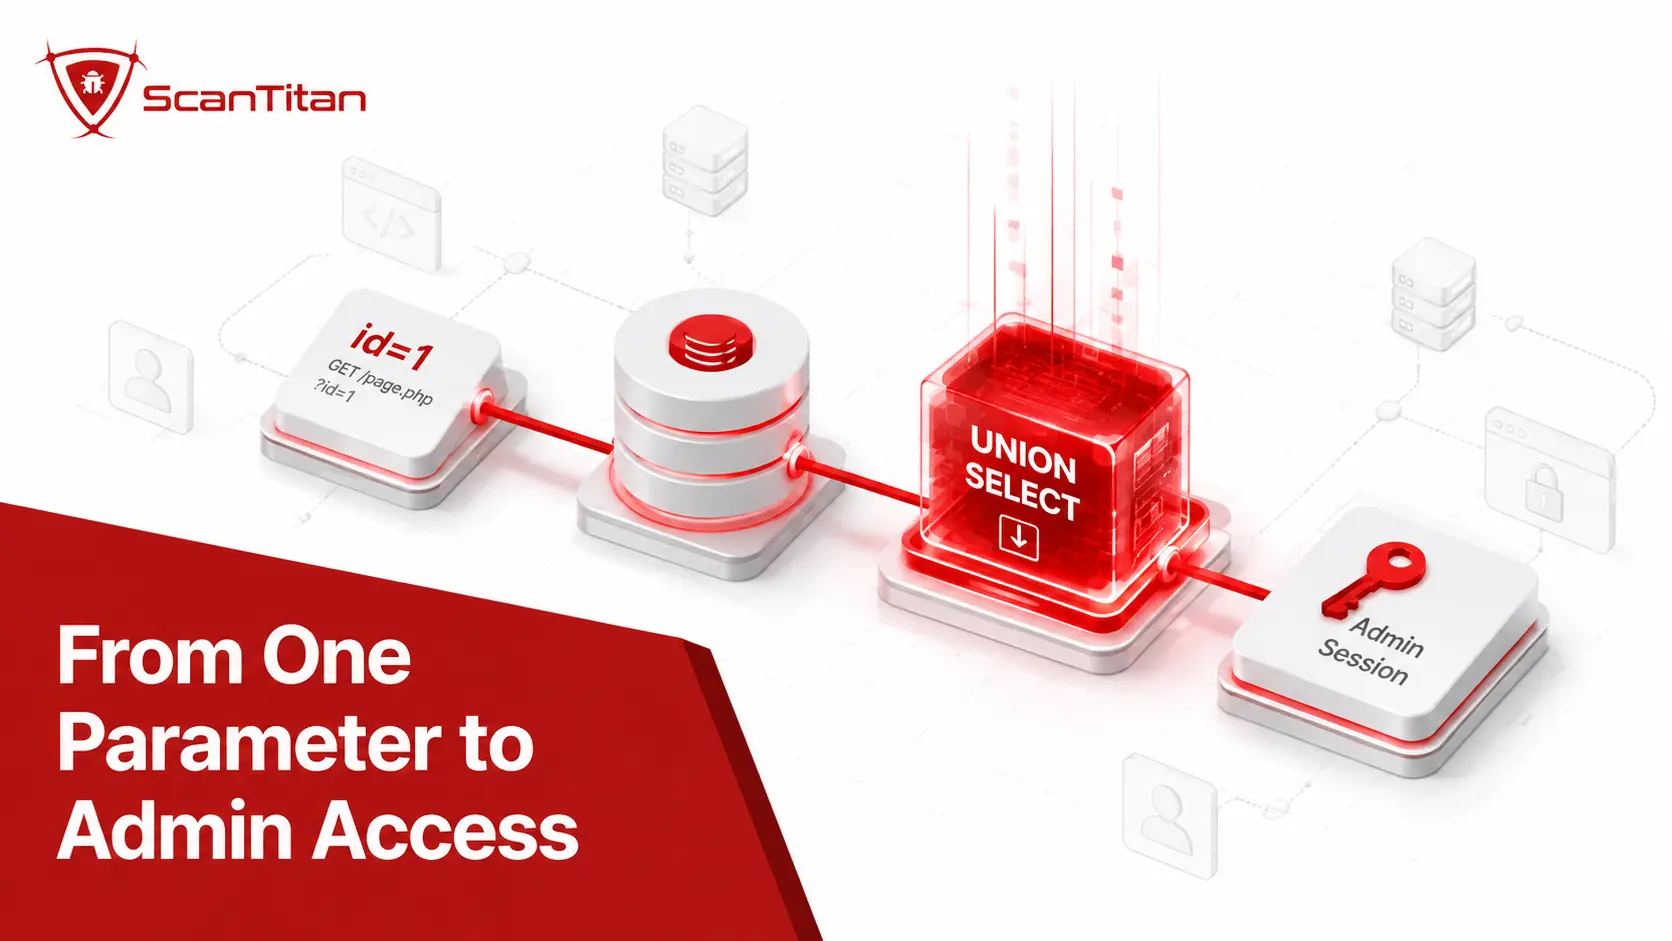
Joomla SQL injection can occur anywhere request-controlled data crosses into unsafe query construction, including core components, third-party extensions, administrator views, filtering and ordering logic, and Web Services endpoints.
Understanding those paths is more useful than memorizing a generic SQLi definition because Joomla’s historical vulnerabilities repeatedly show the same architectural pattern: a request value looks harmless at the controller or model layer, then becomes dangerous when it is concatenated into a structural part of the SQL query.
How option=com_x Parameters Reach Joomla Components and Database Queries
Joomla commonly uses request routing that identifies a component through an option value such as option=com_content, option=com_users, or another com_x component name. Additional values determine views, tasks, filters, record IDs, sorting, pagination, and component-specific behavior.
Those parameters do not become vulnerabilities merely because they appear in a URL. The risk begins when the component later uses them while constructing SQL.
A simplified flow looks like this:
HTTP request → Joomla routing → component/controller → model state → DatabaseQuery → database
Historical Joomla vulnerabilities make this path concrete.
Trustwave’s 2015 research traced a vulnerable path into com_contenthistory. The affected model inherited behavior from JModelList, and request-controlled list state influenced a query built by the model. That flaw eventually allowed researchers to retrieve information from the database.
The lesson for developers is not to block option=com_x. It is to identify every place where a parameter, model state value, selected ID, filter, or ordering choice crosses into SQL.
Why ORDER BY and list[fullordering] Keep Appearing in Joomla SQLi
Ordering parameters are a recurring Joomla SQL injection risk because database placeholders are designed primarily for data values, while SQL identifiers and structural clauses such as column names and sort directions require different handling.
CVE-2017-8917 is one of the clearest examples. Sucuri traced the flaw to Joomla 3.7.0’s com_fields component. A value associated with list.fullordering could influence input passed to the query’s ORDER BY construction. The Joomla project fixed the issue in 3.7.1.
The pattern did not disappear after 2017.
CVE-2025-22207 involved improperly built order clauses in the com_scheduler backend task list. CVE-2026-21630 involved improperly built order clauses in the com_content articles Web Services endpoint. CVE-2026-352212 involved improperly validated order clauses in com_tags.
This is why developers should not take a user-supplied sort field and concatenate it directly into ORDER BY. Bind ordinary values. For structural SQL choices, use a strict allow-list that maps permitted request values to known column names or directions, then pass identifiers through Joomla’s identifier-handling methods where appropriate.
Can Joomla Web Services Endpoints Be Vulnerable to SQL Injection?
Yes. Joomla Web Services endpoints can contain SQL injection vulnerabilities when API-controlled parameters eventually influence unsafe query construction.
Joomla’s Web Services documentation uses a base such as /api/index.php/v1, with paths for resources including content articles. These requests eventually reach application code and database queries just as browser-facing routes do.
CVE-2026-21630 demonstrates the risk directly. Joomla reported that improperly built order clauses caused SQL injection in the com_content articles Web Services endpoint. The affected ranges were Joomla 4.0.0 through 5.4.3 and 6.0.0 through 6.0.3. Joomla fixed the issue in 5.4.4 and 6.0.4.
An API therefore should not be treated as a separate security universe. Filters, sorting parameters, identifiers, and search options still need the same SQL-safe handling as values received through normal site pages.
Which Joomla SQL Injection CVEs Matter Most?
The most useful Joomla SQL injection CVEs are the ones that show recurring root causes: request filtering failures, missing type casting, unsafe ordering clauses, identifier handling mistakes, and unsafe extension query construction.
| CVE | Joomla area | Affected versions | Fixed in | Main lesson |
|---|---|---|---|---|
| CVE-2015-7857 and related 2015 SQLi CVEs | com_contenthistory |
3.2.0 to 3.4.4 | 3.4.5 | Model state and query construction can expose sensitive database data |
| CVE-2017-8917 | com_fields |
3.7.0 | 3.7.1 | list[fullordering] and ORDER BY require strict structural handling |
| CVE-2020-10243 | Featured Articles menu parameters | 1.7.0 to 3.9.15 | 3.9.16 | Numeric values need type enforcement |
| CVE-2020-35613 | Backend com_users list |
3.0.0 to 3.9.22 | 3.9.23 | Incorrect filtering policy can leave SQLi reachable |
| CVE-2022-23797 | Selected IDs | 3.0.0 to 3.10.6, 4.0.0 to 4.1.0 | 3.10.7, 4.1.1 | Arrays and selected record IDs still require safe handling |
| CVE-2025-22207 | com_scheduler |
4.1.0 to 4.4.10, 5.0.0 to 5.2.3 | 4.4.11, 5.2.4 | Unsafe order-clause construction remains dangerous |
| CVE-2025-25226 | Joomla Framework Database package | 1.0.0 to 2.1.1, 3.0.0 to 3.3.1 | 2.2.0, 3.4.0 | Database identifiers need correct handling |
| CVE-2026-21630 | com_content Web Services |
4.0.0 to 5.4.3, 6.0.0 to 6.0.3 | 5.4.4, 6.0.4 | API ordering parameters can become SQLi inputs |
| CVE-2026-35221 | com_finder |
5.4.0 to 5.4.5, 6.0.0 to 6.1.0 | 5.4.6, 6.1.1 | Filter-clause construction needs the same protection as ordinary values |
| CVE-2026-352212 | com_tags |
4.0.0 to 5.4.5, 6.0.0 to 6.1.0 | 5.4.6, 6.1.1 | Order clauses need validation rather than raw request input |
Version ranges and fixes above come from Joomla Security Centre advisories.
CVE-2015-7857: com_contenthistory and Administrator Session Hijacking
CVE-2015-7857 matters because the 2015 Joomla SQL injection was demonstrated as more than a theoretical database leak.
Joomla’s advisory says its core SQL injection issue affected versions 3.2.0 through 3.4.4 and was fixed in 3.4.5. The advisory associates CVE-2015-7297, CVE-2015-7857, and CVE-2015-7858 with that SQLi release.
Trustwave located vulnerable code in the administrator-side com_contenthistory model and showed how the SQLi could read database information. The vulnerable query was a SELECT path, so the original demonstration did not depend on arbitrary database writes. Instead, researchers targeted Joomla’s session data.
If an administrator had an active session, Trustwave showed that a session identifier could be extracted and replayed to access the administrator area. The active administrator session was a prerequisite for that specific takeover chain.
The often repeated “2.8 million sites” number also needs context. Trustwave said BuiltWith estimated that as many as 2.8 million websites used Joomla at the time. It did not claim that 2.8 million Joomla sites were successfully exploited or compromised by this vulnerability.
Why CVE-2015-8562 Is Not a Joomla SQL Injection CVE
CVE-2015-8562 should not be listed as another Joomla SQL injection vulnerability because Joomla classifies it as a remote code execution flaw.
Joomla said the issue affected CMS versions 1.5.0 through 3.4.5 and fixed it in 3.4.6. The vulnerable behavior involved browser information being stored in session data in a way that could lead to code execution.
Technical analysis of the vulnerability describes the mechanism as object injection related to a crafted User-Agent value. Trustwave documented attackers placing data in the User-Agent header and later causing Joomla to retrieve and process that stored value through PHP deserialization behavior.
That makes the distinction important for a Joomla SQLi article: CVE-2015-8562 is historically relevant to Joomla security and database-backed session handling, but it is not itself a SQL injection CVE.
CVE-2017-8917: com_fields and list[fullordering]
CVE-2017-8917 is a key Joomla SQL injection example because it shows why sort and ordering parameters deserve the same security attention as obvious form inputs.
The flaw affected Joomla 3.7.0 and was fixed in Joomla 3.7.1. Joomla credits Marc-Alexandre Montpas of Sucuri with reporting it.
Sucuri traced the vulnerable behavior to FieldsModelFields in com_fields. The model inherited from JModelList, and the researcher showed how the list.fullordering state could become attacker-controlled and eventually influence the query’s ordering logic.
That matters because developers sometimes think only search boxes, login fields, and raw text values are interesting SQLi inputs. A sort field can be just as dangerous when it changes an ORDER BY expression.
The safe pattern is not to bind an arbitrary column name as though it were an ordinary string value. Instead, map a limited set of accepted sort choices to known identifiers and reject anything else.
CVE-2020-10243 and CVE-2020-35613: Type Casting and Filtering Failures
CVE-2020-10243 and CVE-2020-35613 show two different ways apparently routine Joomla input handling can result in SQL injection.
For CVE-2020-10243, Joomla identified missing type casting in a variable used by the Featured Articles frontend menu type. The vulnerability affected Joomla 1.7.0 through 3.9.15 and was fixed in 3.9.16.
This is a useful reminder that a value expected to be numeric should actually be enforced as numeric before it reaches a query. A developer should not assume that an ID parameter contains an integer because the normal UI only sends integers.
CVE-2020-35613 affected Joomla 3.0.0 through 3.9.22 and was fixed in 3.9.23. Joomla attributed the SQL injection in the backend com_users list to an improper filter blacklist configuration.
The two CVEs make a broader point: generic input filtering is not a replacement for correct SQL construction. Data types, parameter binding, structural allow-lists, and database API usage each solve different parts of the problem.
CVE-2022-23797: SQL Injection Through Selected IDs
CVE-2022-23797 is important because it fills a gap between the better-known 2020 issues and later Joomla 4 and 5 vulnerabilities.
Joomla reported that inadequate filtering of selected IDs could result in SQL injection. The affected ranges were Joomla 3.0.0 through 3.10.6 and Joomla 4.0.0 through 4.1.0. Joomla fixed the issue in 3.10.7 and 4.1.1.
Selected IDs often arrive as arrays rather than single values. That does not make them inherently safe. If an application expects a collection of numeric identifiers, each value must still be treated according to its required type, or passed into database helpers designed to bind collections safely.
Current Joomla database documentation includes methods such as bindArray() and prepared-statement helpers for constructing value lists without manually concatenating raw request values into the SQL.
CVE-2025-22207 and CVE-2025-25226: Order Clauses and Database Identifiers
CVE-2025-22207 and CVE-2025-25226 are useful together because one affected Joomla CMS query construction while the other affected identifier handling in the Joomla Framework database package.
CVE-2025-22207 affected com_scheduler in Joomla 4.1.0 through 4.4.10 and 5.0.0 through 5.2.3. Joomla said improperly built order clauses in the backend task list caused SQL injection, and fixed the issue in 4.4.11 and 5.2.4.
CVE-2025-25226 affected the Framework Database package’s quoteNameStr method. Affected package ranges were 1.0.0 through 2.1.1 and 3.0.0 through 3.3.1, fixed in 2.2.0 and 3.4.0. Joomla also added an important qualification: the vulnerable protected method was not used by the original database classes, so the issue concerned derived classes that actually called it.
That distinction prevents the article from overstating exposure. A vulnerable library version does not always mean every application using the library has an exploitable path.
2026 Joomla SQL Injection CVEs: CVE-2026-21630, CVE-2026-35221 and CVE-2026-352212
The 2026 Joomla SQL injection advisories show that unsafe filter and order-clause construction remains relevant even in current Joomla branches.
CVE-2026-21630 affected the com_content articles Web Services endpoint. Joomla said improperly built order clauses caused the flaw. Versions 4.0.0 through 5.4.3 and 6.0.0 through 6.0.3 were affected, with fixes in 5.4.4 and 6.0.4.
CVE-2026-35221 involved authenticated blind SQL injection in com_finder. Joomla attributed it to improperly built filter clauses. Affected versions were 5.4.0 through 5.4.5 and 6.0.0 through 6.1.0, fixed in 5.4.6 and 6.1.1.
CVE-2026-352212 affected com_tags, where improperly validated order clauses could produce authenticated blind SQL injection. Joomla lists affected versions as 4.0.0 through 5.4.5 and 6.0.0 through 6.1.0, again fixed in 5.4.6 and 6.1.1.
The unusually long numeric suffix in CVE-2026-352212 is not a typo. Joomla’s Security Centre uses that exact identifier.
Taken together, these 2026 cases reinforce a pattern visible since CVE-2017-8917: values that determine SQL structure, particularly filtering and ordering, need dedicated controls rather than generic sanitization.
Can Joomla Extensions Introduce SQL Injection?
Yes. Joomla extensions can introduce SQL injection independently of Joomla core, so a fully patched CMS does not guarantee that every component, plugin, module, template integration, or page builder is free from SQLi.
Third-party extensions execute application logic and can build their own database queries. A single extension can therefore reintroduce a weakness that has already been handled correctly elsewhere in Joomla.
A recent example is CVE-2026-58078 in Quix Page Builder. The research disclosure describes an unauthenticated SQL injection involving a request-controlled article ID that reached a database query without the required integer handling. The SQLi itself was fixed in Quix 6.2.1, with the researcher recommending 6.2.2 because additional issues were addressed in that release.
This is why an extension inventory matters just as much as checking the Joomla core version.
It is also why removing extensions you no longer use is more valuable than merely disabling them. Fewer installed code paths mean fewer dependencies that need monitoring, patching, and review.
For a broader view of the difference between platform and ecosystem exposure, ScanTitan compares those security models in its Joomla vs WordPress security guide.
How the Vulnerable Extensions List and JSST Fit Into Joomla Security
The Joomla Security Strike Team and the Vulnerable Extensions List serve different but complementary roles.
The Joomla Security Strike Team, or JSST, oversees security issues affecting the Joomla project. Joomla’s security site describes the JSST as a group of developers and security specialists responsible for managing and improving security for Joomla. The Security Centre publishes resolved issues affecting Joomla CMS and Framework releases.
The Vulnerable Extensions List, or VEL, focuses on extension risk. Joomla’s Extensions Directory says its live list contains extensions for which a known vulnerability has no patch listed, while its resolved list covers extensions for which a patch is available. The VEL also warns that it is compiled from available reports and does not guarantee completeness or independent validation.
Site owners therefore need more than one check:
Core and Framework advisories tell you what Joomla itself has fixed. The VEL and extension vendors help you track third-party code. Your own inventory tells you which of those packages are actually installed.
Lifecycle matters too. Joomla 3 standard support ended in August 2023, and its extended LTS period ended in February 2025. Joomla documentation lists Joomla 4.4 security support ending in October 2025. As of September 2026, Joomla’s roadmap identifies 5.x and 6.x as supported release families.
Running an end-of-life branch changes the problem from “Which patch fixes this CVE?” to “How do we migrate onto software that still receives fixes?”
How Does the Joomla Database API Prevent SQL Injection?
The Joomla database API helps prevent SQL injection by separating SQL structure from values and by providing prepared statements, parameter binding, typed parameters, identifier quoting, and query-builder methods.
These APIs are most effective when developers use them according to the role each piece of input plays in the query.
Use DatabaseQuery, bind(), and ParameterType for Data Values
Joomla’s current database documentation uses prepared statements and parameter binding for values rather than concatenating request values directly into SQL.
For example, a developer can build a condition using a placeholder such as :id, then bind an integer value using ParameterType::INTEGER. Joomla’s documentation explains that when a variable is bound to a query, the application does not need to manually quote or escape that bound value.
The important distinction is that placeholders represent data values.
A user ID, username, article ID, search term, status value, or similar piece of data usually belongs in a bound parameter.
Type information matters as well. Joomla supports ParameterType values so the query can distinguish an integer from a string. For numeric IDs, explicitly enforcing an integer type reduces ambiguity and prevents a string containing unexpected SQL syntax from being treated as the intended ID.
For collections, Joomla also documents bindArray() and helpers such as whereIn(), which avoid manually constructing a comma-separated list from uncontrolled values.
Use quoteName() for Identifiers, quote() Carefully for Values, and Cast Numeric IDs
quoteName(), quote(), parameter binding, and integer casting solve different problems, so they should not be treated as interchangeable “sanitization” functions.
quoteName() is designed for database identifiers such as table and column names. Joomla’s own examples use it when specifying fields, tables, joins, and ordering expressions.
quote() applies database-appropriate quoting to values, but modern code should prefer parameter binding for ordinary untrusted values whenever the query supports it. Prepared statements make the boundary between SQL instructions and application data much clearer.
Integer casting is valuable when the application truly expects an integer. CVE-2020-10243 is a Joomla example where lack of type casting contributed to SQL injection.
Structural choices require another strategy. You cannot safely assume that binding a value will turn arbitrary user text into a valid column name or ASC/DESC instruction. Sort fields and directions should come from an explicit allow-list.
For example, if the UI accepts title, date, or id as sort choices, translate those values to known application-controlled identifiers. Reject anything outside that set.
Joomla input filters still have a role, but they should not be treated as an SQL security boundary. A filter designed to clean HTML or normalize request values does not replace correct query-level data handling.
Vulnerable vs Fixed Joomla PHP Query Example
The safer Joomla pattern keeps request-controlled values out of the SQL string itself and binds them separately with the expected type.
Consider an extension that receives an article ID.
A risky pattern is:
use Joomla\CMS\Factory;

$db = Factory::getContainer()->get(
    \Joomla\Database\DatabaseInterface::class
);

$input = Factory::getApplication()->input;
$id = $input->get('id');

$query = $db->createQuery()
    ->select('*')
    ->from($db->quoteName('#__content'))
    ->where('id = ' . $id);

$db->setQuery($query);
$article = $db->loadObject();
The problem is not the query builder itself. The problem is that $id becomes part of the SQL text through string concatenation.
A safer approach separates the value:
use Joomla\CMS\Factory;
use Joomla\Database\ParameterType;

$db = Factory::getContainer()->get(
    \Joomla\Database\DatabaseInterface::class
);

$input = Factory::getApplication()->input;
$id = (int) $input->getInt('id');

$query = $db->createQuery()
    ->select('*')
    ->from($db->quoteName('#__content'))
    ->where($db->quoteName('id') . ' = :id')
    ->bind(':id', $id, ParameterType::INTEGER);

$db->setQuery($query);
$article = $db->loadObject();
The improved example applies two controls with different purposes. The application enforces the value as an integer, then passes it to the query as a bound integer parameter. The column name is application-controlled and handled as an identifier with quoteName().
Joomla’s database documentation follows this same prepared-statement model and demonstrates bind() with ParameterType::INTEGER.
The same principle applies beyond IDs. Bind text values, dates, booleans, and other data with appropriate types. For structural SQL such as permitted sort columns, choose from application-controlled identifiers rather than accepting raw SQL fragments from the request.
How Can You Check a Joomla Site for SQL Injection Exposure?
You can check a Joomla site for known SQL injection exposure by inventorying the core, Framework, and extensions, comparing their exact versions with security advisories, reviewing custom query code, and using non-destructive external testing to identify externally visible exposure.
No single check answers every SQLi question.
Check Core, Extension, and Framework Versions Against Security Advisories
Start with exact versions because known Joomla SQL injection CVEs usually have precise affected and fixed ranges.
A Joomla 5 site, for example, should not be treated as “safe” merely because the major version is supported. CVE-2026-21630 affected part of the 5.x line through 5.4.3, while CVE-2026-35221 and CVE-2026-352212 affected later 5.4 releases through 5.4.5.
The same principle applies to extensions.
Record each installed component, plugin, module, page builder, template framework, and supporting package. Compare versions against Joomla’s Vulnerable Extensions List, vendor advisories, and CVE records. Remove software that is abandoned or no longer needed.
Custom extensions require another layer because no public CVE database can describe a private query flaw that has never been disclosed.
Review custom code for values flowing from request input into calls such as where(), order(), having(), raw SQL fragments, selected-ID arrays, search expressions, or manually assembled IN clauses.
Understand What an External Joomla Scan Can and Cannot Confirm
An external Joomla scan can identify externally observable risks and match detectable software versions to known vulnerabilities, but it cannot prove that every custom query path is free from SQL injection.
ScanTitan’s Joomla vulnerability scanner uses non-destructive external checks and known-version detection. It does not send working SQL injection exploit payloads to a site simply to prove exploitation.
That distinction matters.
Version-based detection can tell you that a detected Joomla or extension version falls inside the affected range of a known CVE. External configuration checks can identify additional exposed conditions. Neither result should be described as source-code review of a custom extension.
If you need to validate a suspected custom SQLi path, use a controlled testing environment and an authorized application-security process. ScanTitan’s guide to testing for SQL injection vulnerabilities explains the broader testing process.
For an SMB team, the practical workflow is to combine version awareness, external detection, extension inventory, and code review where custom development exists.
How to Prevent SQL Injection in Joomla
Prevent Joomla SQL injection by keeping supported code patched and by ensuring every extension treats data values, identifiers, numeric IDs, filters, and ordering parameters according to their database context.
Owners and developers control different parts of that process.
For Joomla Site Owners and Administrators
Site owners prevent known Joomla SQL injection primarily by keeping the CMS and extensions on supported, patched releases and by removing code that no longer receives security maintenance.
- Patch supported versions: Apply Joomla core and extension security updates promptly after testing them in staging. A fixed CVE remains relevant to your site until the affected version is actually replaced.
- Remove abandoned extensions: Uninstall extensions that are no longer required or supported. Do not assume that disabling a component eliminates every reachable file or integration path.
- Review the VEL: Compare installed extensions with Joomla’s live and resolved Vulnerable Extensions List, while remembering Joomla explicitly warns that the list is not guaranteed to contain every vulnerability.
- Migrate end-of-life branches: Treat Joomla 3 and Joomla 4 migration as a security requirement rather than a cosmetic upgrade. Unsupported branches no longer receive normal security fixes from the Joomla project.
- Limit database privileges: Give the application’s database account only the permissions the site actually requires. SQL injection impact depends partly on what the compromised query and database account are able to access or modify.
- Use a WAF as a secondary control: A web application firewall can block some recognizable SQLi traffic, but it does not repair unsafe query construction. MITRE notes that application firewalls can reduce exposure while still missing vectors or being bypassed.
- Harden the rest of Joomla: SQLi prevention belongs inside a larger maintenance process that includes account security, access control, HTTPS, logging, backups, and extension review. ScanTitan’s Joomla hardening guide covers that broader workflow, while the Joomla security features guide explains the controls available in the CMS.
If a suspected SQL injection has already led to unauthorized modification, new administrator accounts, malicious files, or other evidence of compromise, patching the vulnerable component is only the first step. The site should also be investigated for persistence and contamination. ScanTitan’s website malware removal service covers that recovery scenario.
For Joomla Extension Developers
Extension developers prevent Joomla SQL injection by designing query construction so request-controlled data never becomes trusted SQL syntax by accident.
- Bind ordinary values: Use placeholders and
bind()for user-controlled values rather than concatenating those values intowhere(),set(), or other SQL fragments. - Declare expected types: Use
ParameterTypeand appropriate input methods for integers, strings, booleans, and other known value types. Type enforcement is especially important for IDs. - Quote identifiers correctly: Use
quoteName()for application-controlled table and column names rather than manually adding database quoting characters. - Allow-list structural choices: Map user-facing sort and filter options to known column names, operators, and sort directions. Never treat arbitrary request text as a trusted
ORDER BYexpression. - Bind arrays safely: Use helpers such as
bindArray()orwhereIn()for collections instead of joining unchecked request values into an SQL list. - Review inherited model state: Values set by parent classes such as list-model behavior can still originate from request parameters. CVE-2017-8917 is a useful reminder to trace state all the way to the query.
- Test API routes too: Apply the same query-review rules to
/api/index.php/v1endpoints and other Web Services code. An API parameter is not safer merely because it arrives as JSON or through an authenticated token. - Separate HTML filtering from SQL safety: Use Joomla input and output filtering for the problems those tools are designed to solve, but keep SQL safety at the database-query boundary.
A security review should follow data flow from request to query, not simply search the codebase for a few dangerous function names.
Joomla SQL Injection FAQ
These questions focus specifically on Joomla SQL injection rather than general scanner behavior.
Can a Joomla Extension Cause SQL Injection Even If Joomla Core Is Fully Patched?
Yes. A Joomla extension can contain its own SQL injection vulnerability even when the CMS core is completely current.
Extensions can register components, AJAX endpoints, administrator interfaces, Web Services, models, plugins, and database queries. That code is maintained separately from Joomla core, so installing the latest CMS release does not automatically replace vulnerable third-party PHP.
CVE-2026-58078 in Quix Page Builder is a useful recent example. The reported flaw involved extension code handling a request-controlled article ID incorrectly before it reached a query.
For that reason, maintain an extension inventory alongside the Joomla version. Check vendor advisories and the Joomla VEL, remove abandoned software, and include custom extensions in code review.
“Joomla is updated” and “the Joomla application has no known vulnerable extension” are two separate claims.
Is $db->quote() Enough to Prevent SQL Injection in Joomla?
No. $db->quote() is useful for database-aware value quoting, but it should not be treated as a universal replacement for prepared statements and context-specific query construction.
For ordinary values, Joomla’s modern database documentation uses placeholders and bind(). That approach separates the SQL statement from the data and can include explicit ParameterType information.
Identifiers need different treatment. Column and table names belong in quoteName(), generally after your application has selected them from a known set. Sort directions and other structural SQL elements often require allow-listing rather than parameter binding.
The right question is therefore not “Was this input escaped?” It is “What role does this value play in the SQL query, and which Joomla API or validation rule matches that role?”
Does Joomla InputFilter Prevent SQL Injection?
No. Joomla input filtering should not be treated as a substitute for parameterized database queries, type enforcement, and structural allow-listing.
Input filtering is useful for controlling the format or content of incoming data. SQL injection occurs later, when a value is interpreted inside an SQL statement. Those are related but different trust boundaries.
Historical Joomla CVEs make the distinction clear. CVE-2020-10243 involved missing type casting in a value that reached SQL, while CVE-2020-35613 involved improper blacklist filtering in the com_users backend list.
A developer should therefore filter input according to application requirements and independently construct database queries safely. Bind values, enforce their types, quote application-controlled identifiers, and allow-list structural query options.
Why Are ORDER BY Parameters Difficult to Protect With Normal Parameter Binding?
ORDER BY parameters are difficult because a placeholder normally represents data, while a column name or SQL direction is part of the query’s syntax.
Consider a request that lets a user sort a list by title, creation date, or ID. You can bind a search value in a WHERE clause because it is data. You should not simply accept arbitrary text from a sort parameter and drop it into an ORDER BY clause.
Instead, translate each permitted choice to a known identifier:
title → a.title
date → a.created
id → a.id
Then reject any value not present in the mapping and use quoteName() for the selected identifier where appropriate.
This pattern is particularly important in Joomla because multiple historical SQLi vulnerabilities have involved ordering or filter clauses, including CVE-2017-8917, CVE-2025-22207, CVE-2026-21630, and CVE-2026-352212.
Can Joomla Web Services API Endpoints Have SQL Injection Vulnerabilities?
Yes. Joomla Web Services API endpoints can have SQL injection vulnerabilities if request parameters flow into incorrectly constructed database queries.
Joomla documents API access under /api/index.php/v1 and exposes resource routes such as content articles. The API layer still depends on backend application code and database access.
CVE-2026-21630 is a direct example. Joomla reported SQL injection in the com_content articles Web Services endpoint because of improperly built order clauses. The flaw affected portions of both the Joomla 5 and Joomla 6 release lines before patched versions were published.
For developers, the security rule is the same whether an input arrives through HTML, query parameters, JSON, or an API client: trace it to the query and protect it according to its SQL role.
How Do I Know Whether My Joomla Version Is Affected by a Known SQLi CVE?
Check the exact installed Joomla version against the affected and fixed ranges in the Joomla Security Centre instead of relying only on the major version number.
For example, saying “we run Joomla 5” would not have been enough to rule out CVE-2026-21630, because Joomla listed affected 5.x releases through 5.4.3. Likewise, CVE-2026-35221 affected Joomla 5.4.0 through 5.4.5 before the fix in 5.4.6.
Repeat the same check for third-party extensions and relevant Joomla Framework packages.
A vulnerability scanner can automate part of this known-version matching, but do not confuse version detection with exploit confirmation. Custom code without a published advisory requires code review or authorized application testing.
Can a WAF Stop Joomla SQL Injection Without Patching the Vulnerable Component?
A WAF may block some attempts to exploit Joomla SQL injection, but it should not replace the security update or code fix that removes the vulnerable query path.
Trustwave documented WAF and ModSecurity protections for the 2015 Joomla SQLi while still recommending that affected Joomla installations upgrade to 3.4.5.
That is the right way to think about a WAF: as an additional filtering layer, not as proof that vulnerable PHP is safe to leave online.
A WAF may be valuable when an emergency patch cannot be deployed immediately, when it provides virtual-patching coverage, or when it blocks broad automated probing. But signatures can miss unexpected encodings, alternate routes, new attack forms, or custom extension behavior.
Patch the root cause first. Keep the WAF as defense around the application, not as a substitute for secure database code.