Website Security Blog: Vulnerability Scanning and Malware Guides
Practical website security guides on vulnerability scanning, malware removal, WordPress, APIs and attack surface management, written by practitioners for teams without a SOC.
Website Security Blog Topics: Scanning, Malware, WordPress and APIs
Each guide explains how an attack or exposure works, how to detect it and how to fix it.
WordPress core files modified is a scanner alert that means a file in your install no longer matches the official release for your version. It is not always a hack.
The best Sucuri alternatives cover some or all of what Sucuri sells: a firewall, WordPress protection, hack cleanup and website scanning. This guide ranks six of them by how many
Is your website blacklisted by Google? Google has no single blacklist. A site can sit on Google’s Safe Browsing list, which triggers security warnings, carry a manual action, which is
A website flagged as phishing is a site that a browser, security vendor or email filter has classified as a fake login or credential trap. The cause is either a
.htaccess malware is malicious configuration code that an attacker writes into the Apache .htaccess file, which the server reads before WordPress loads. It can redirect search visitors, run image files
A cloaking hack in WordPress is malicious code that shows spam to Google and a normal site to you, so the dashboard and your own browser look clean while search
Nulled plugins malware is malicious code hidden in a pirated copy of a premium WordPress plugin, installed by an owner who wanted it for free. The code runs with the
A site still blocklisted after cleanup is rarely a mystery. The flag stays because you are still waiting for a review, part of the infection is still there, or a
Malicious JavaScript on website pages is script code that an attacker planted so it runs in your visitors’ browsers. It loads from a theme file, a database row, a third-party
WordPress mu-plugin malware is malicious PHP placed in the wp-content/mu-plugins folder, where WordPress loads it on every request without activation, so it never shows as an active plugin. Attackers use
Hidden admin user WordPress infections are administrator accounts that exist in the database but are filtered out of the Users screen by code, so the dashboard shows nothing unusual. Attackers
The 12 signs of website malware fall into five groups: what visitors see, what Google shows, what you see in the dashboard, what the server’s files and logs show, and
PHP2Shell is the name researchers gave to two critical PHP core flaws, CVE-2026-109618 and CVE-2026-109619, that let an unauthenticated attacker run code on a server through ordinary web requests. The
To find a backdoor in a website, run three passes: compare every file against a clean copy, search for code that behaves like a backdoor, and trace unusual requests in
How did my website get hacked? Almost always through one of nine entry points: a vulnerable plugin or theme, stolen credentials, a nulled theme, a compromised hosting account, vulnerable custom
A seo spam hack is an attack that injects spam pages, links or redirects into your site so the attacker can rank pharmacy, casino or counterfeit-goods pages on your domain.
Database malware WordPress owners miss is malicious code, links or settings stored in database rows instead of files, which is why file scanners and file restores never catch it. It
WordPress malware keeps coming back when cleanup removed what you could see and left the way back in. The usual causes are a surviving backdoor, a hidden admin user, a
Obfuscated PHP malware is malicious PHP code that an attacker has scrambled so scanners and site owners cannot read it at a glance. The scrambling uses encoding, string tricks and
The 15 different types of malware below are the families every security guide names, and each one is explained from a site owner’s point of view: what it does to
A clean malware scan is a report that says the scanner found nothing it recognizes, and it is not proof that a site is clean. When a malware scanner says
A malicious redirect is code that sends visitors from your page to a spam, scam or malware site without their consent. It often fires only for some visitors, which is
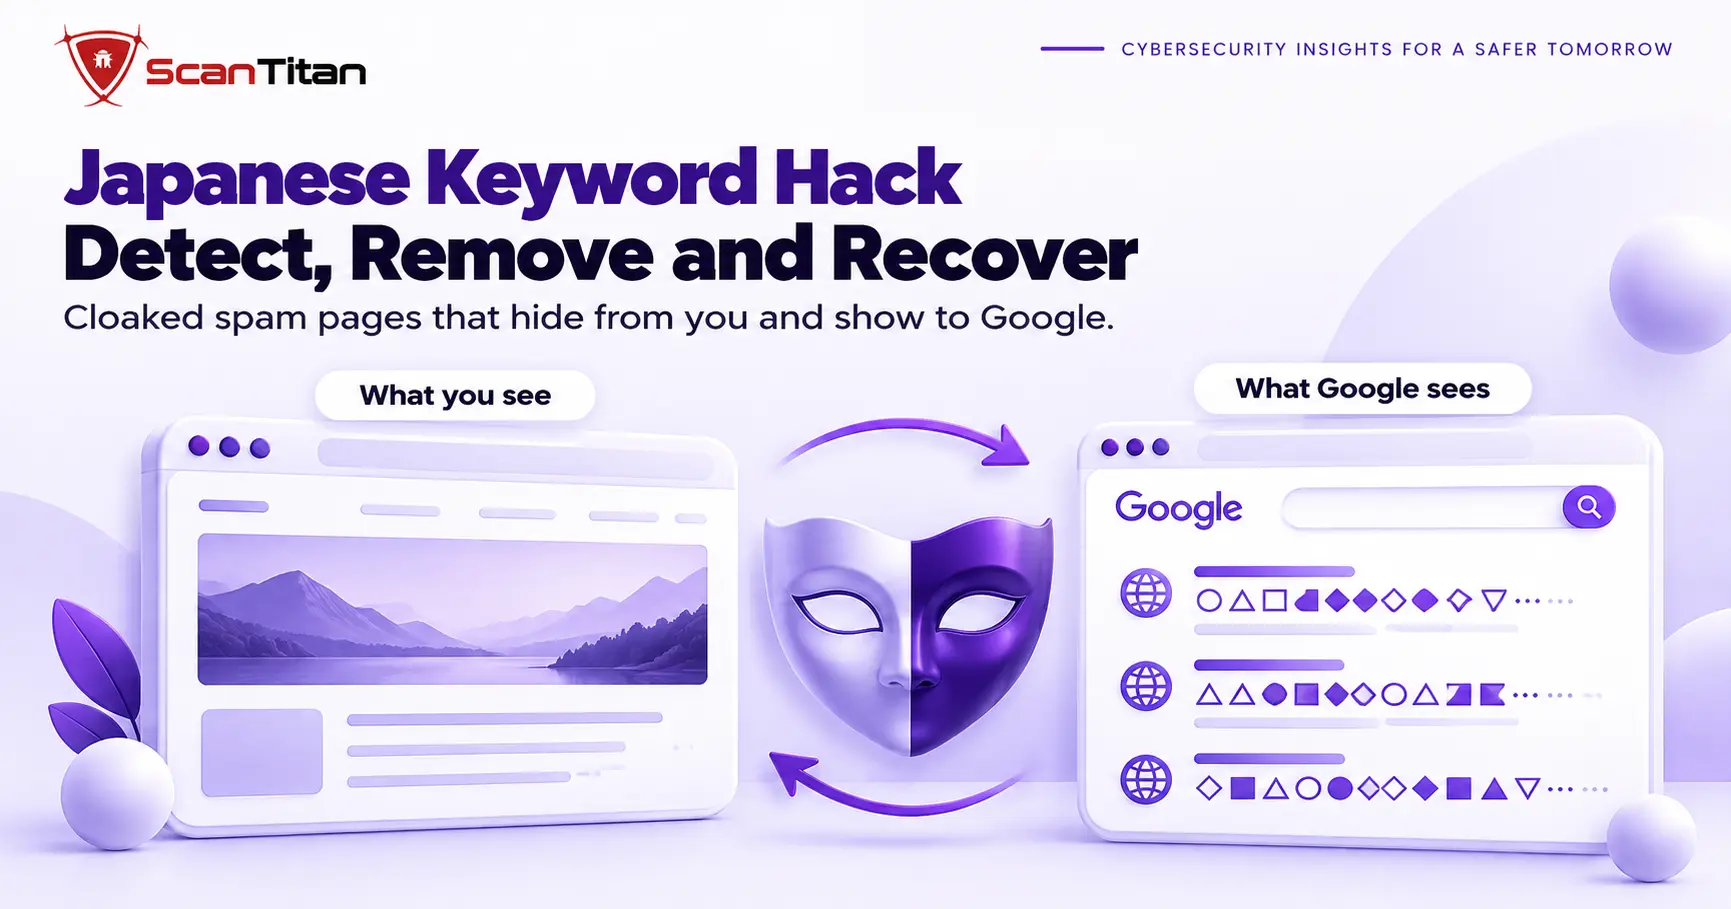
The Japanese keyword hack is a form of SEO spam hack in which attackers inject thousands of auto-generated Japanese pages into a compromised website. It works by cloaking: Google and
A web shell is a server-side script that an attacker can use to maintain remote access to a compromised web server. Depending on its capabilities and the privileges of the
The Deceptive Site Ahead warning is a red Chrome screen that appears when Google Safe Browsing detects behavior associated with phishing or social engineering on a page. For visitors, it
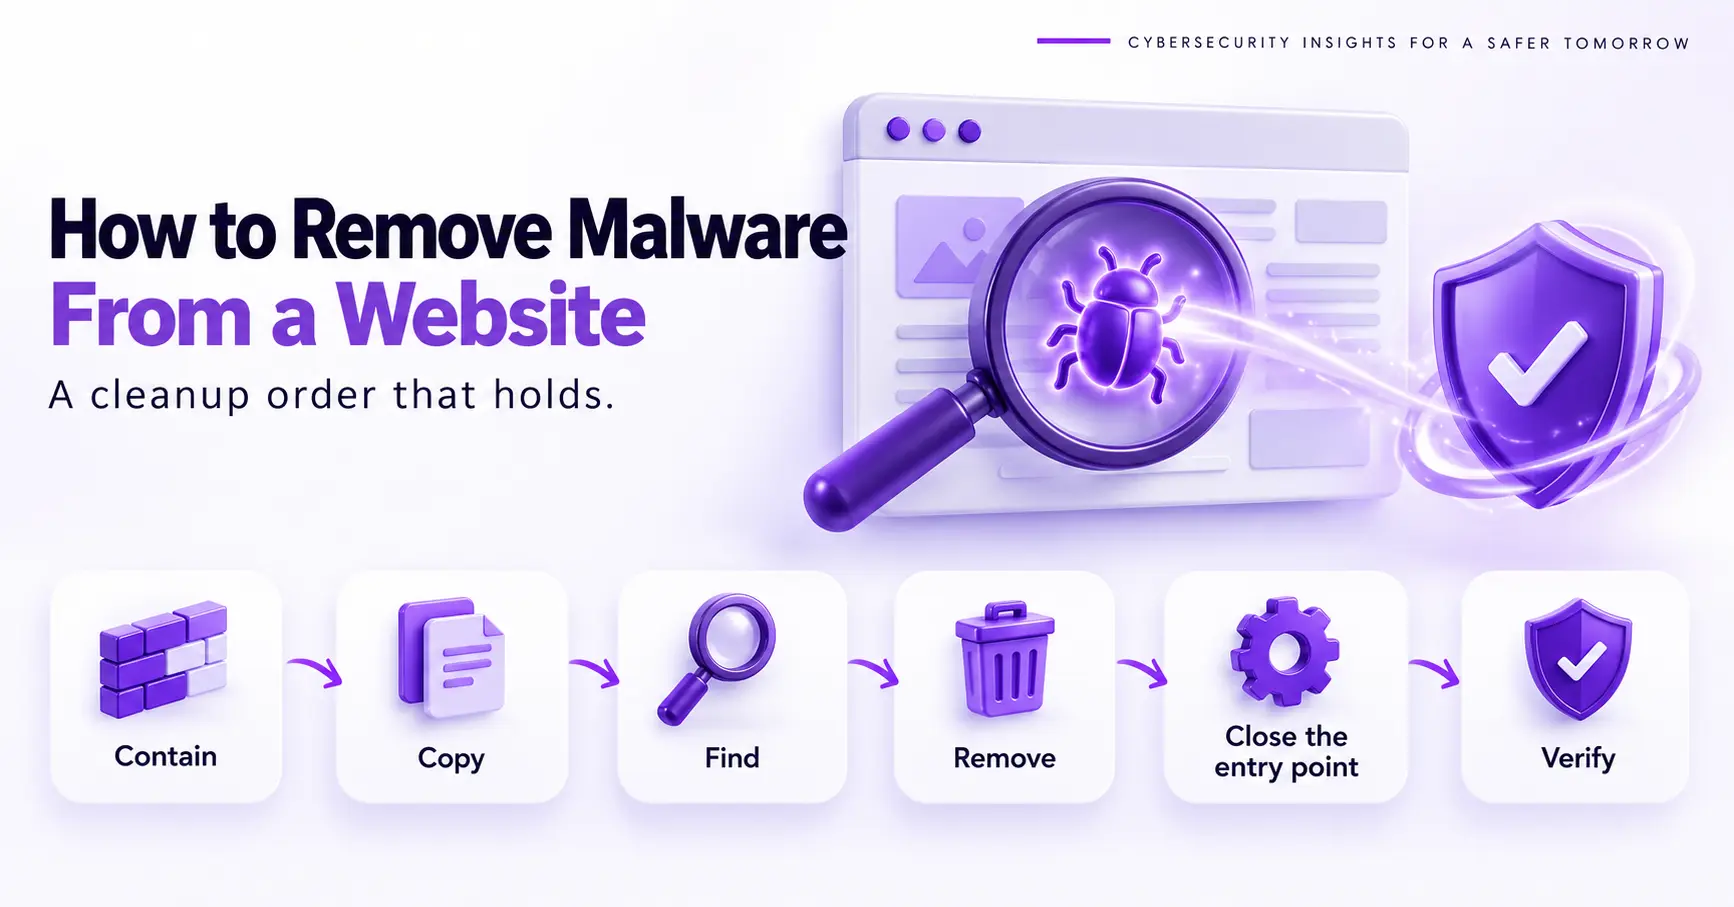
A website malware cleanup is the ordered process you follow to remove malware from website files and databases without leaving a way back in. It runs in six steps: contain
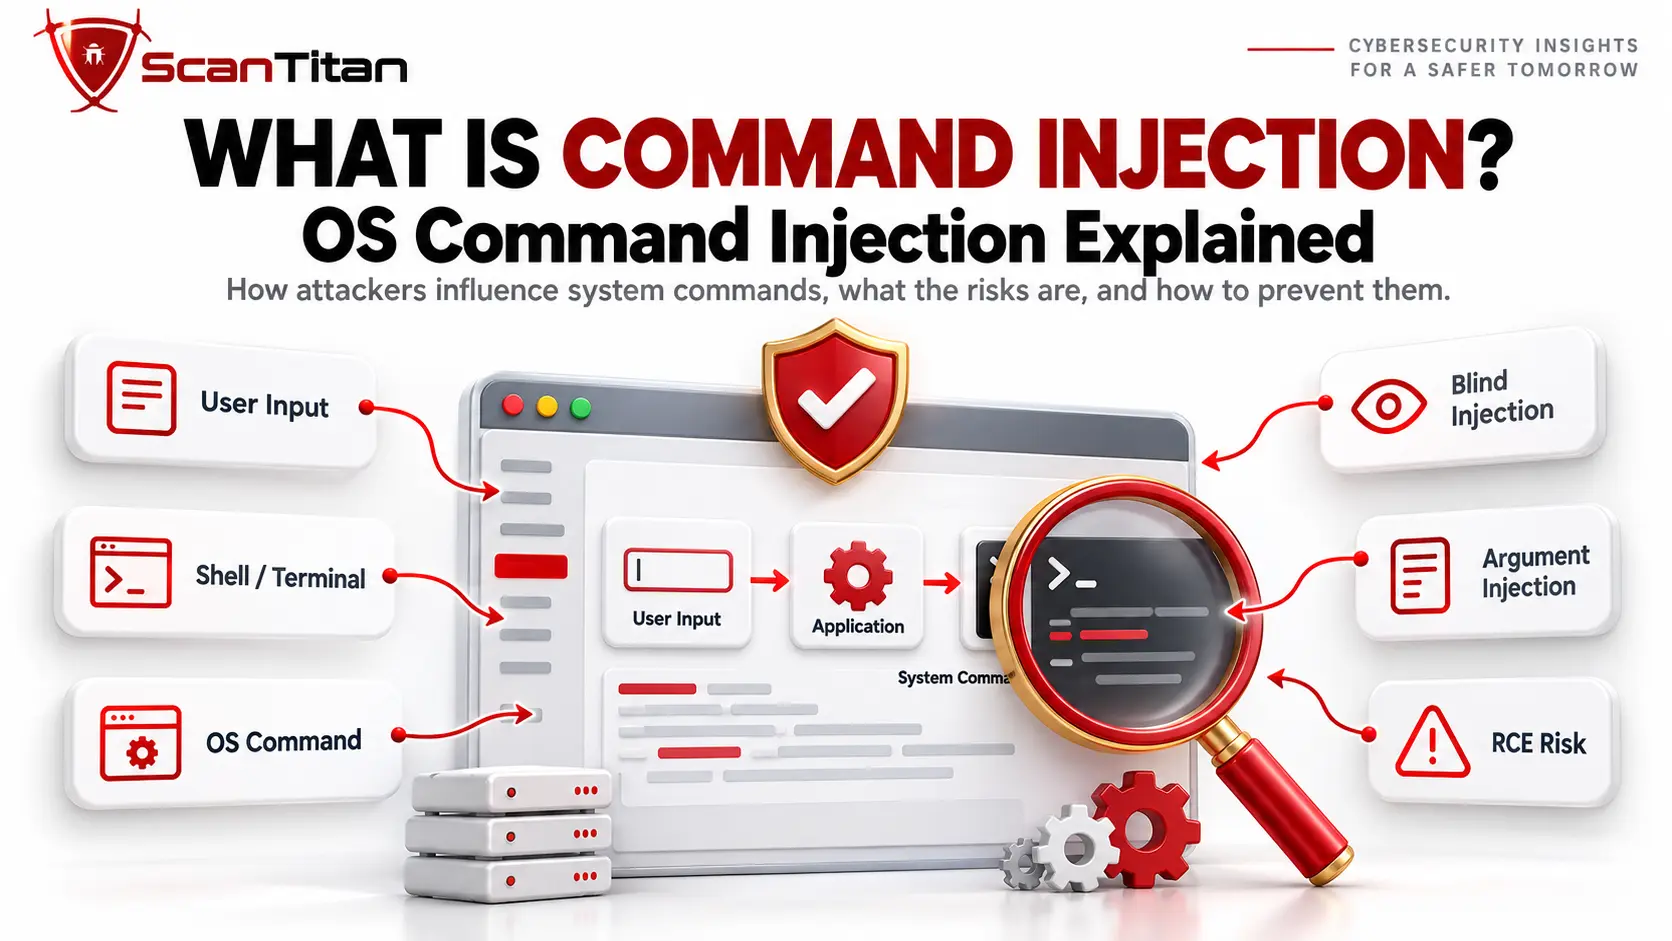
Command injection, usually referring to OS command injection, is a security vulnerability in which attacker-controlled input changes an operating-system command executed by an application, allowing unintended command behavior or additional
An exposed .env file vulnerability occurs when a web server allows unauthorized users to retrieve an environment configuration file. A publicly accessible .env file can reveal database credentials, API keys,
The OWASP API Top 10 is a ranked list of the ten most critical API security risks, and the 2023 edition is still the current version. It covers broken authorization,
The best vulnerability scanning tools in 2026 depend on what you need to scan. ScanTitan, Intruder, and HostedScan serve small teams that want cloud scanning without a security department, Tenable
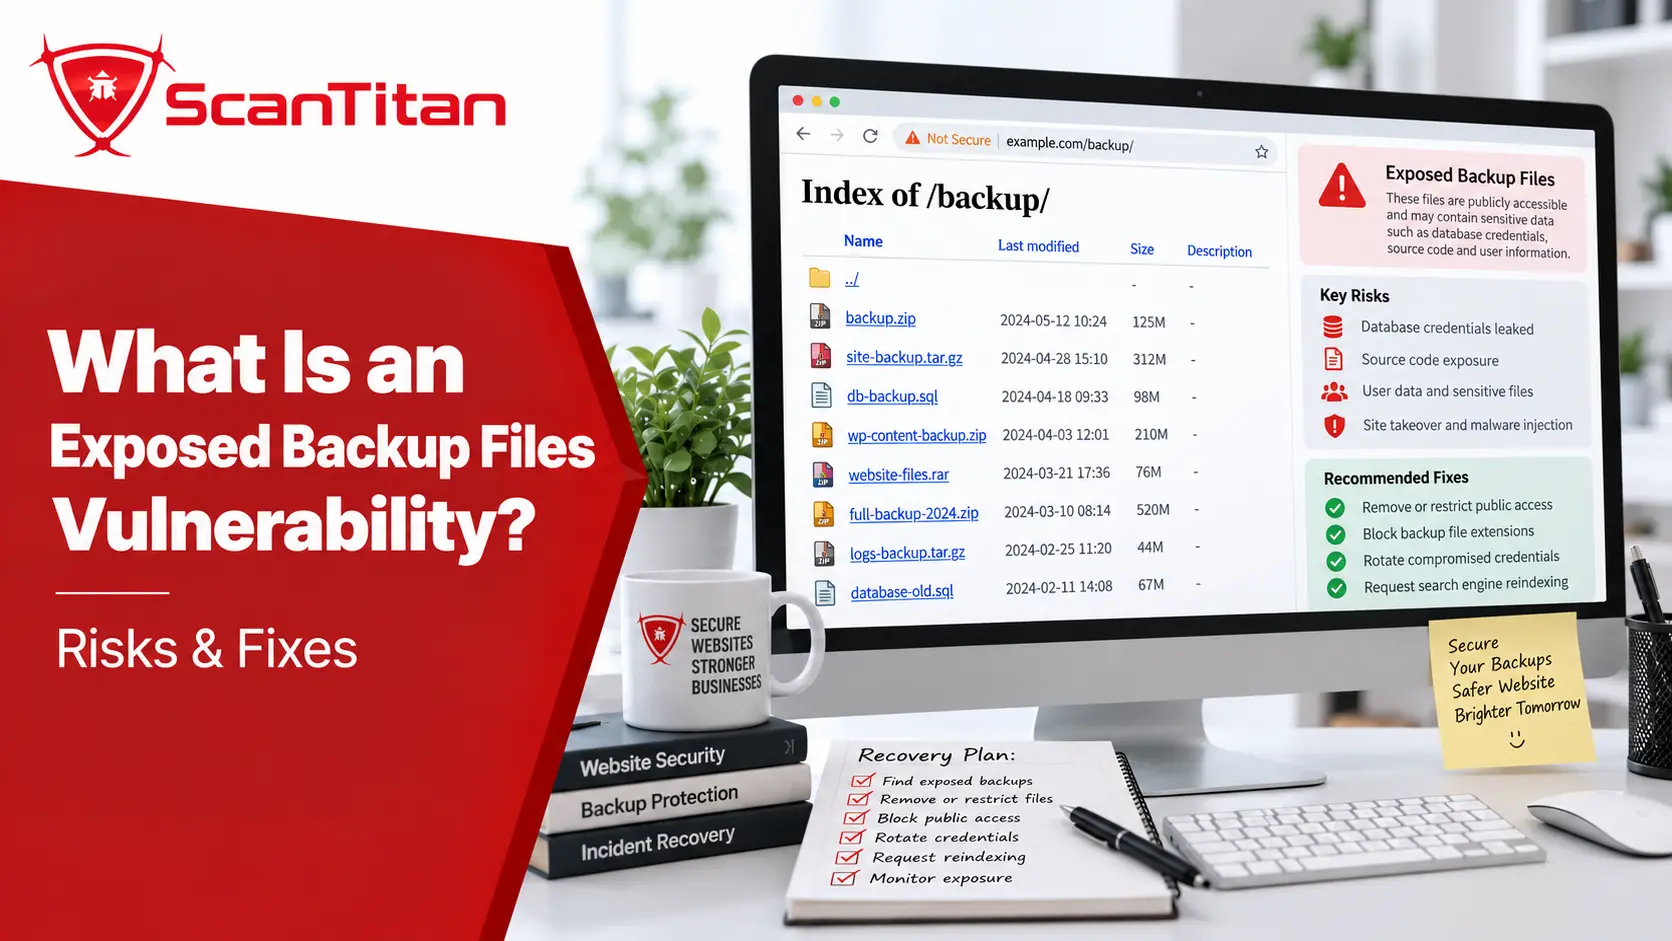
An exposed backup files vulnerability occurs when a backup, database dump, old source-code copy, deployment archive, or editor-generated file is publicly accessible from a web server. Files such as config.php.bak,
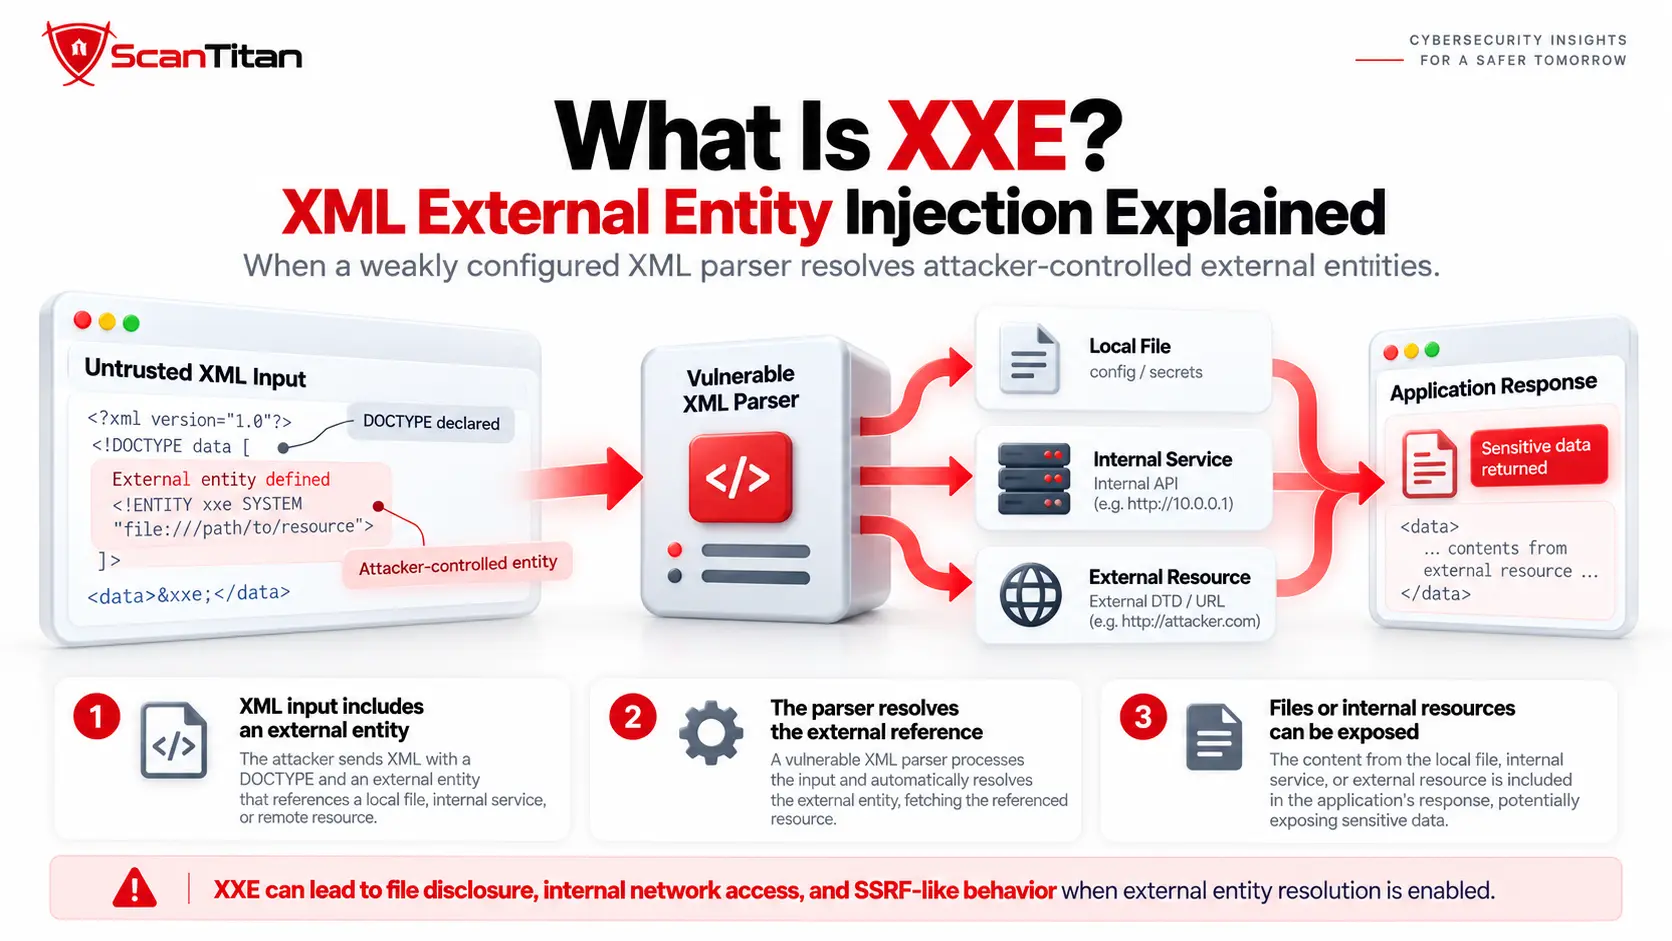
XML External Entity (XXE) Injection is a web security vulnerability in which an application processes attacker-controlled XML with a parser that is allowed to resolve external entities or other external
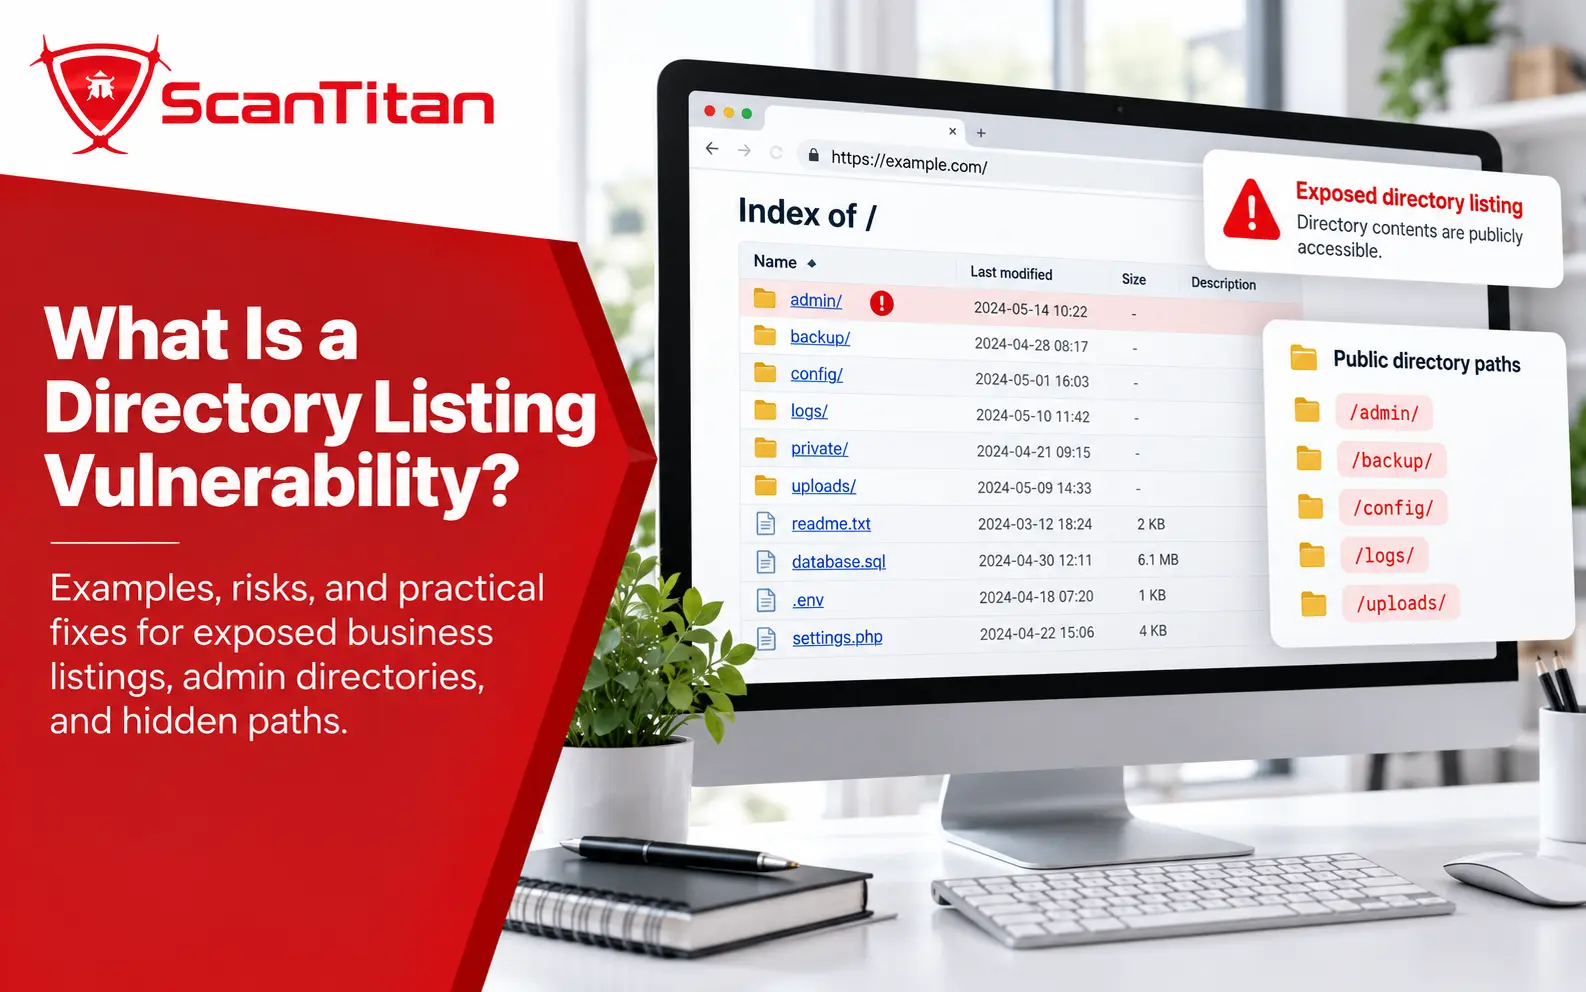
A directory listing vulnerability occurs when a web server exposes a browsable index of files and subdirectories that were not intended to be discovered this way. Instead of returning an
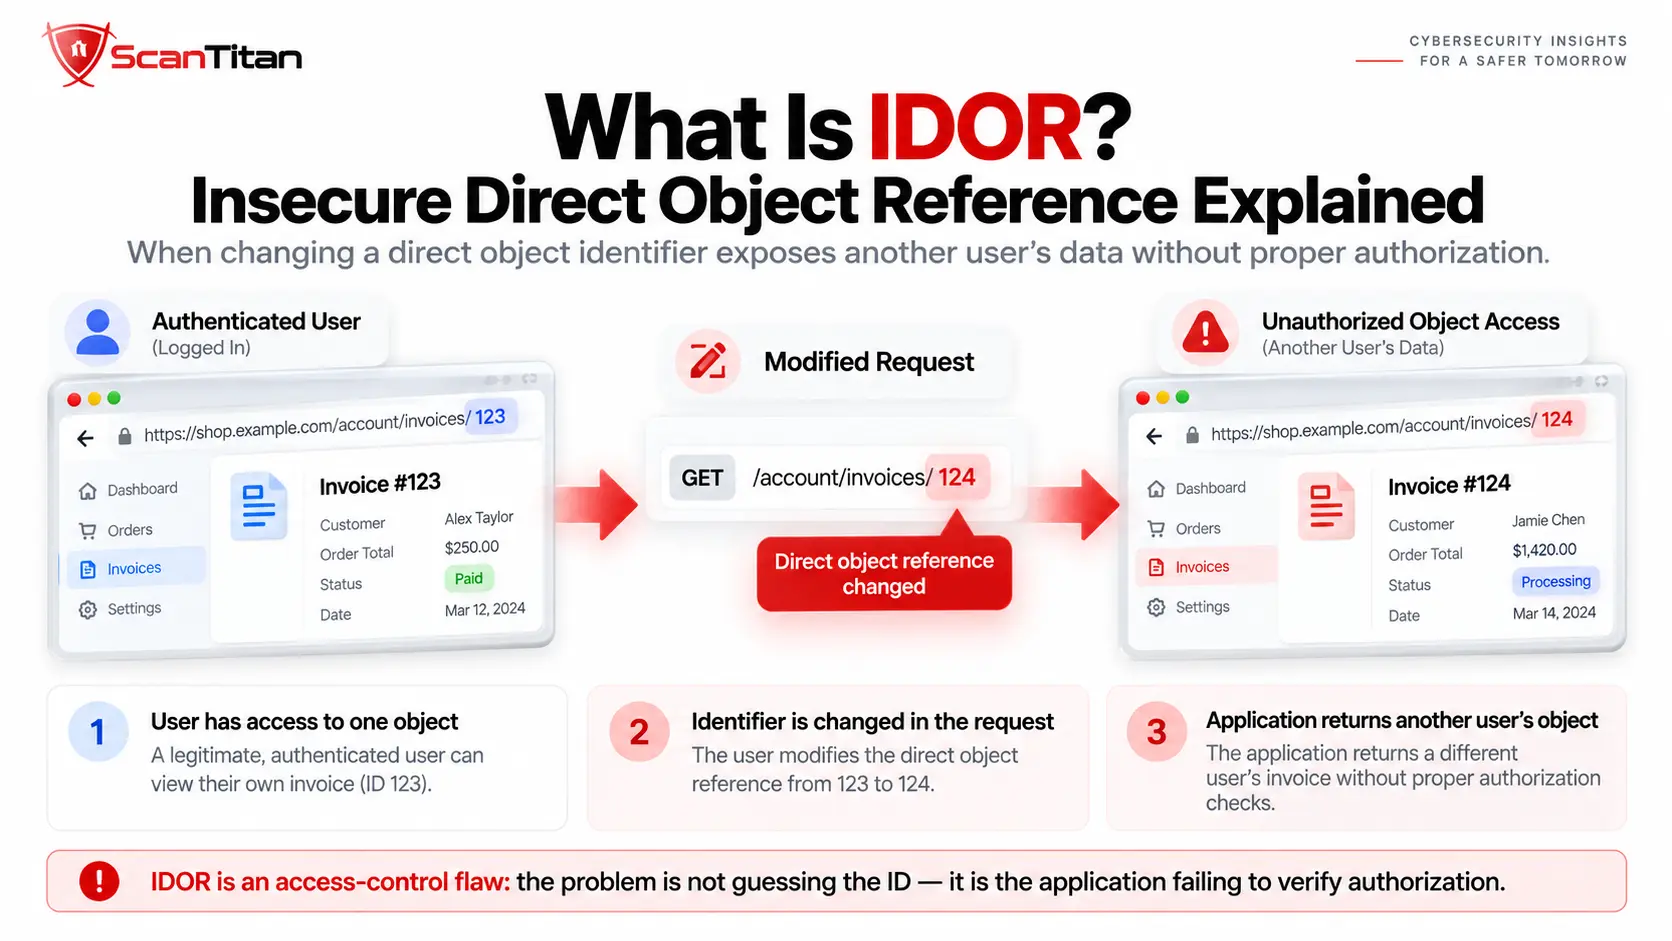
Insecure Direct Object Reference (IDOR) is an access control vulnerability in which an application uses a user-controllable reference to retrieve, change, delete, or otherwise act on an object without verifying
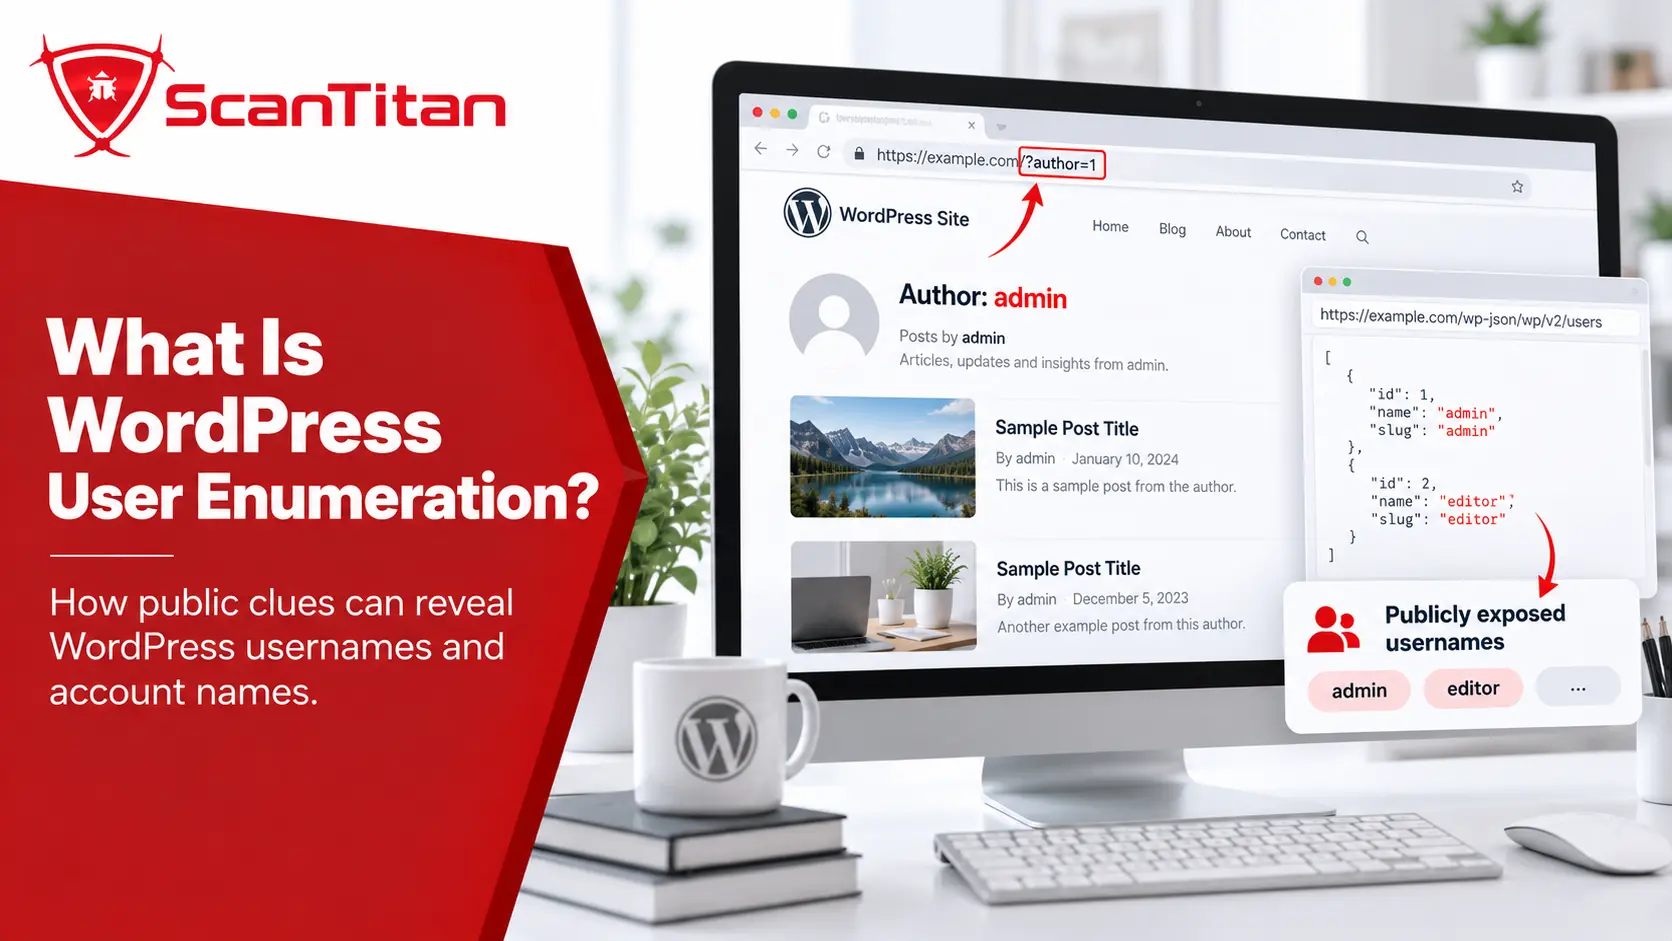
WordPress user enumeration is the process of discovering information that identifies valid WordPress accounts, such as user IDs, display names, author slugs, author URLs, or whether an account exists. WordPress
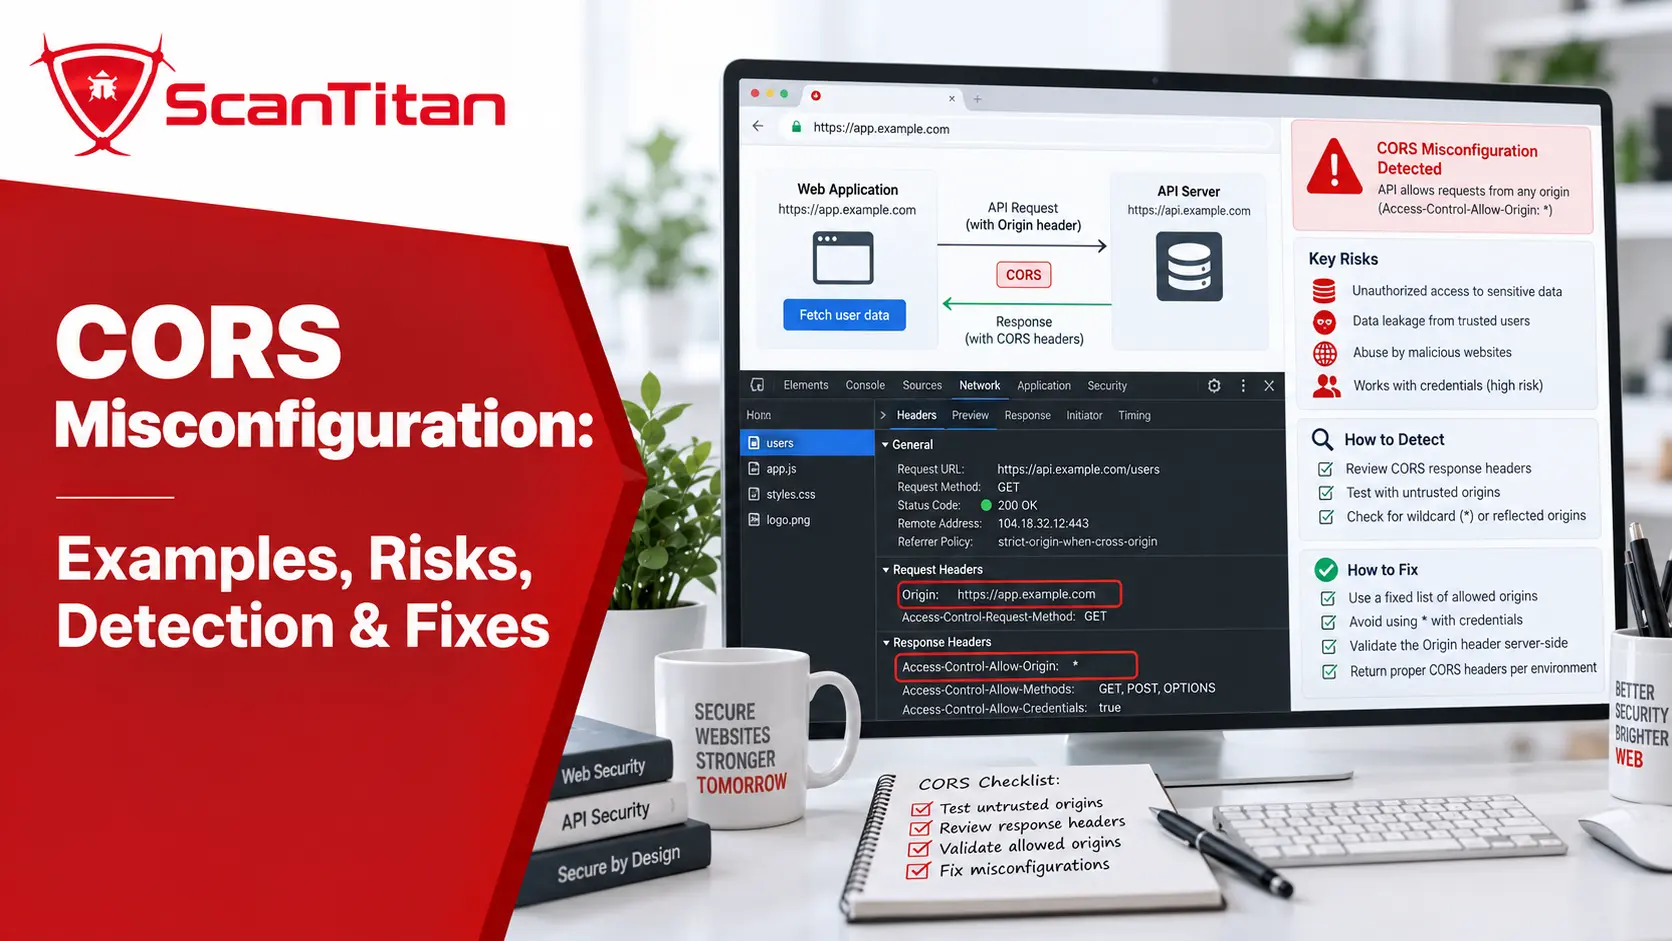
A CORS misconfiguration occurs when a web application allows an untrusted origin to read cross-origin responses that should only be available to trusted websites. Common causes include reflecting arbitrary Origin
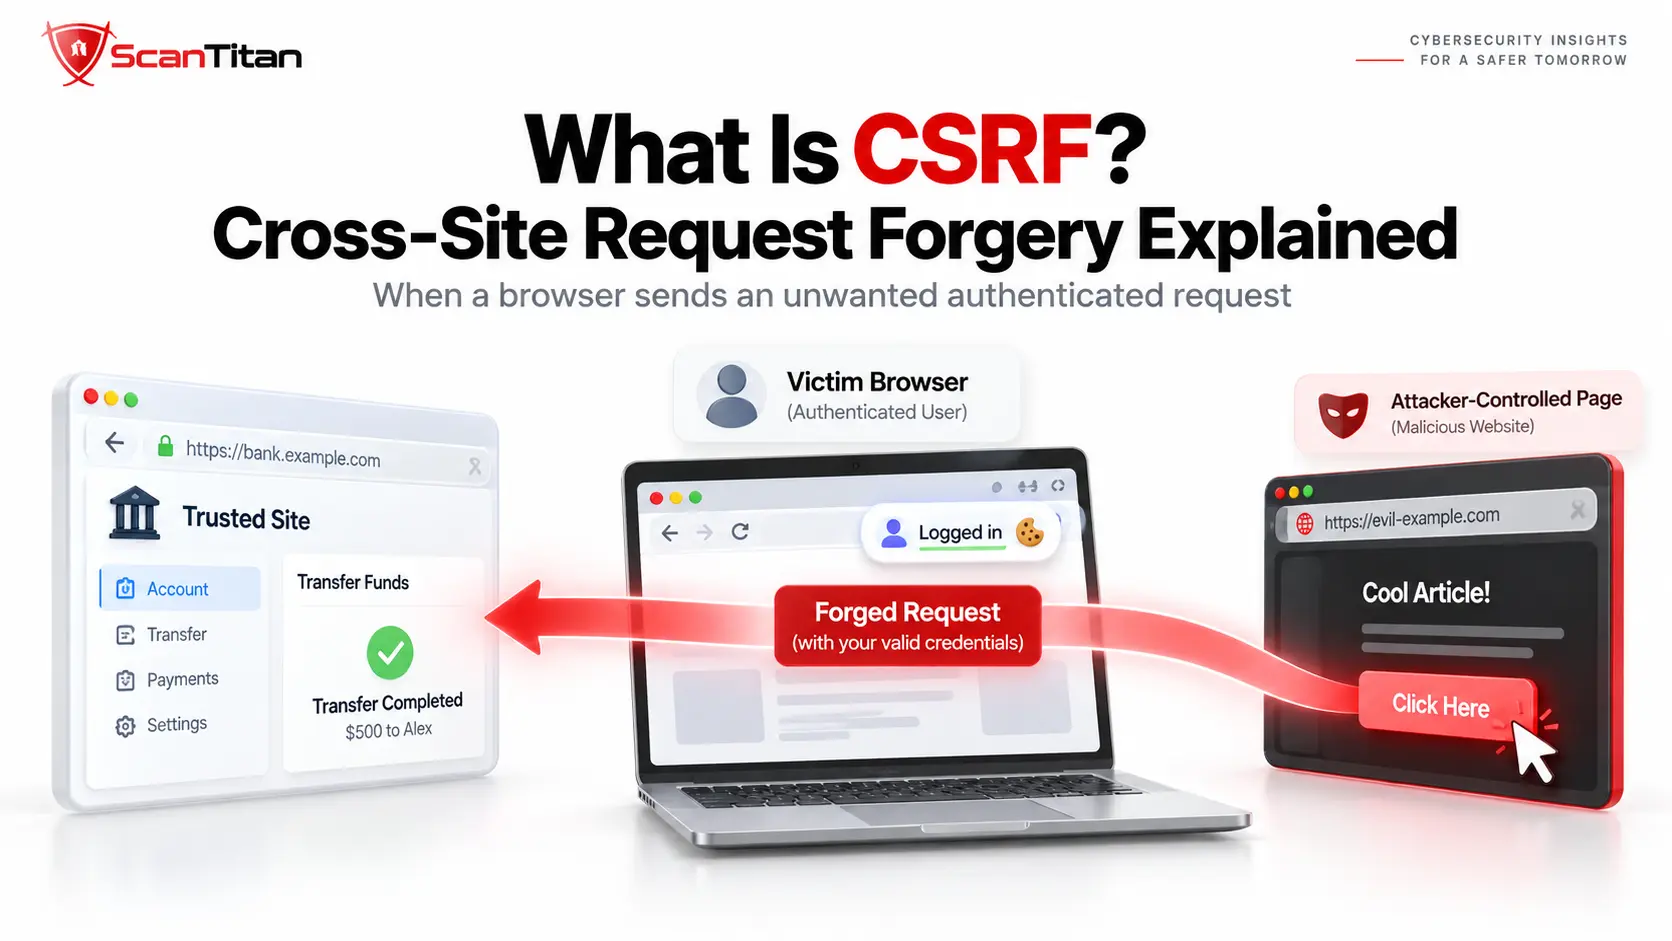
Cross-Site Request Forgery (CSRF) is a web security vulnerability in which an attacker causes a user’s browser to send an unintended request to an application that accepts the user’s automatically
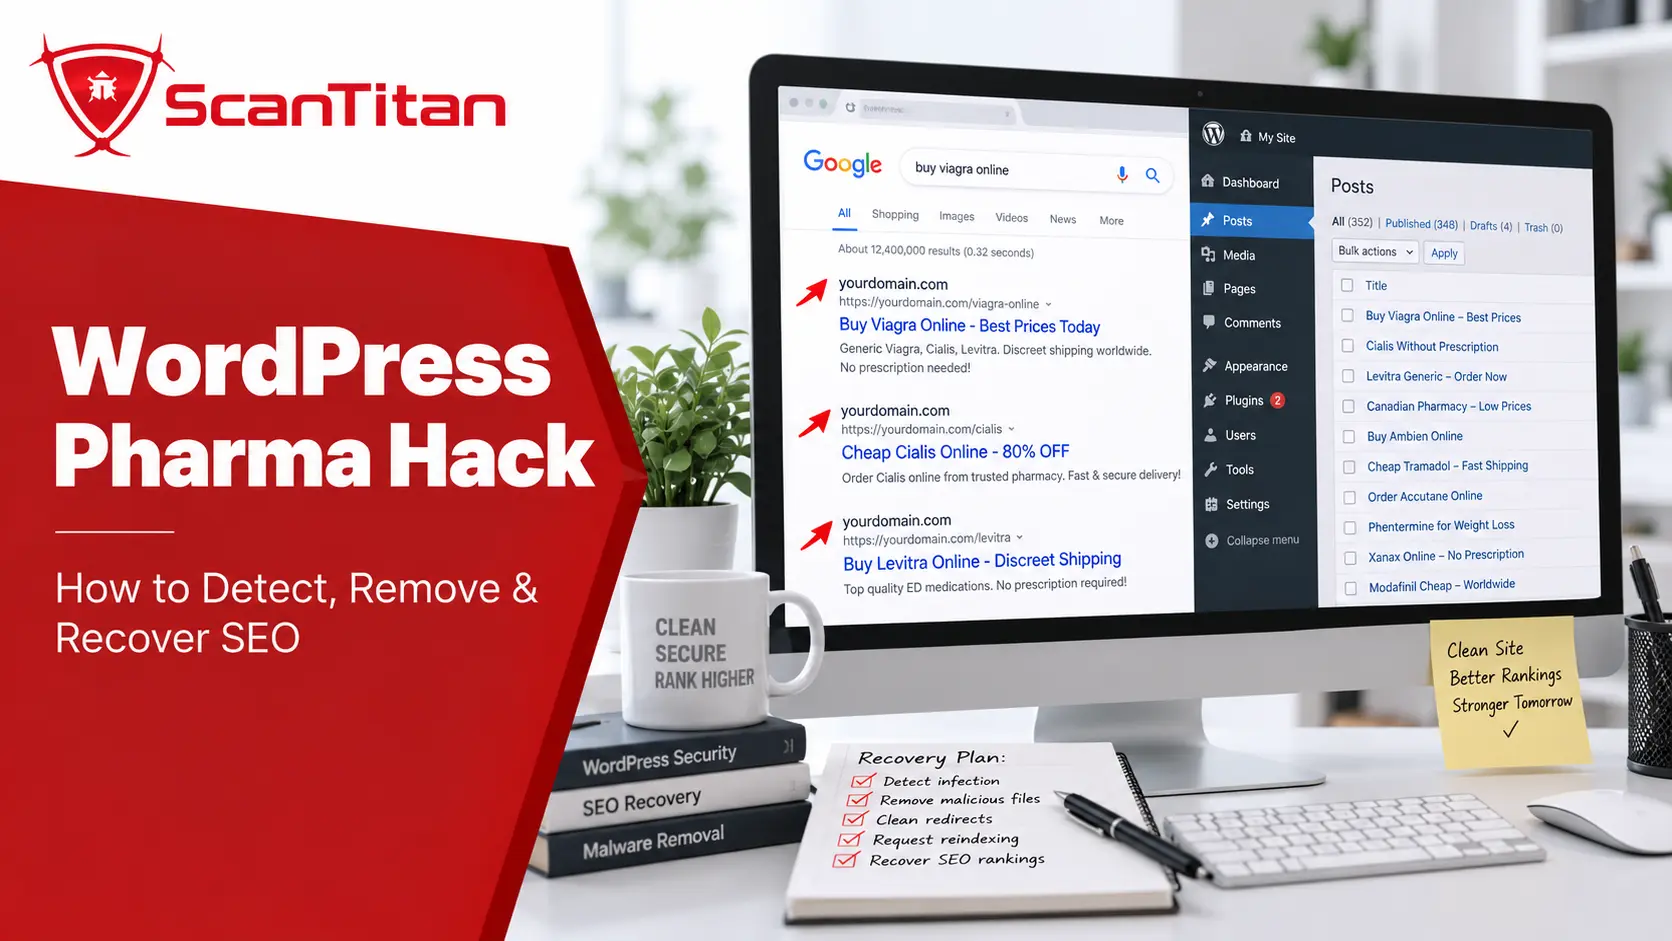
A WordPress pharma hack is a post-compromise SEO spam infection that adds pharmaceutical keywords, links, pages, redirects, or hidden content to a WordPress website without the owner’s permission. It is
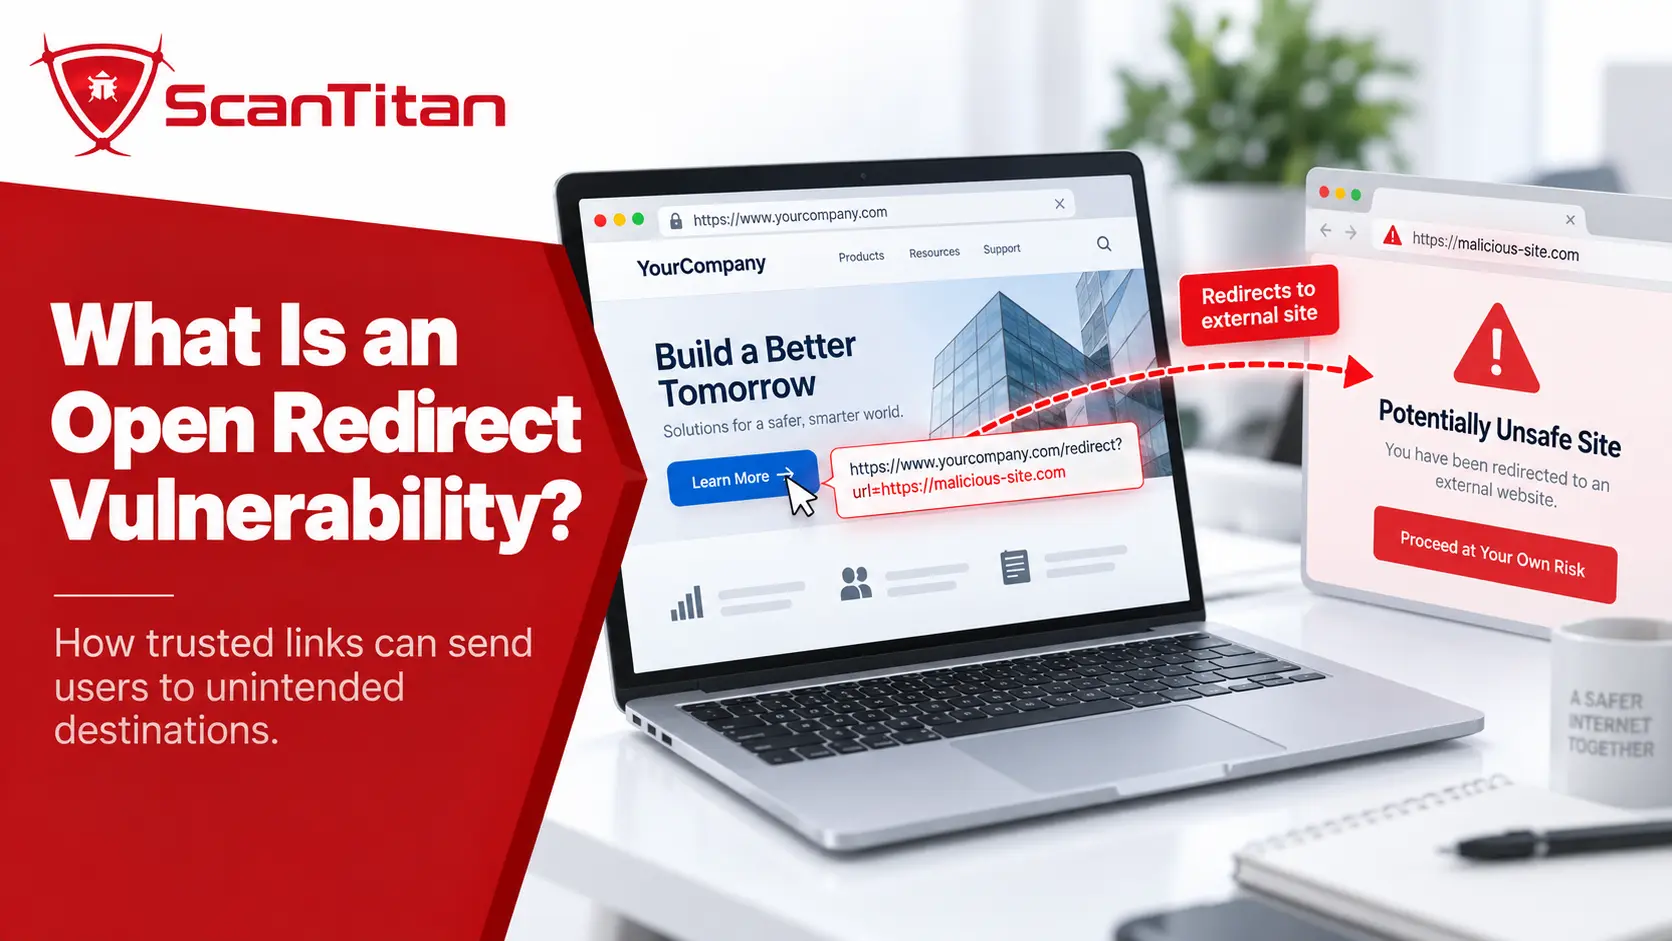
An open redirect vulnerability occurs when a web application lets attacker-controlled input determine where a user is redirected without sufficiently restricting the final destination. An attacker can then create a
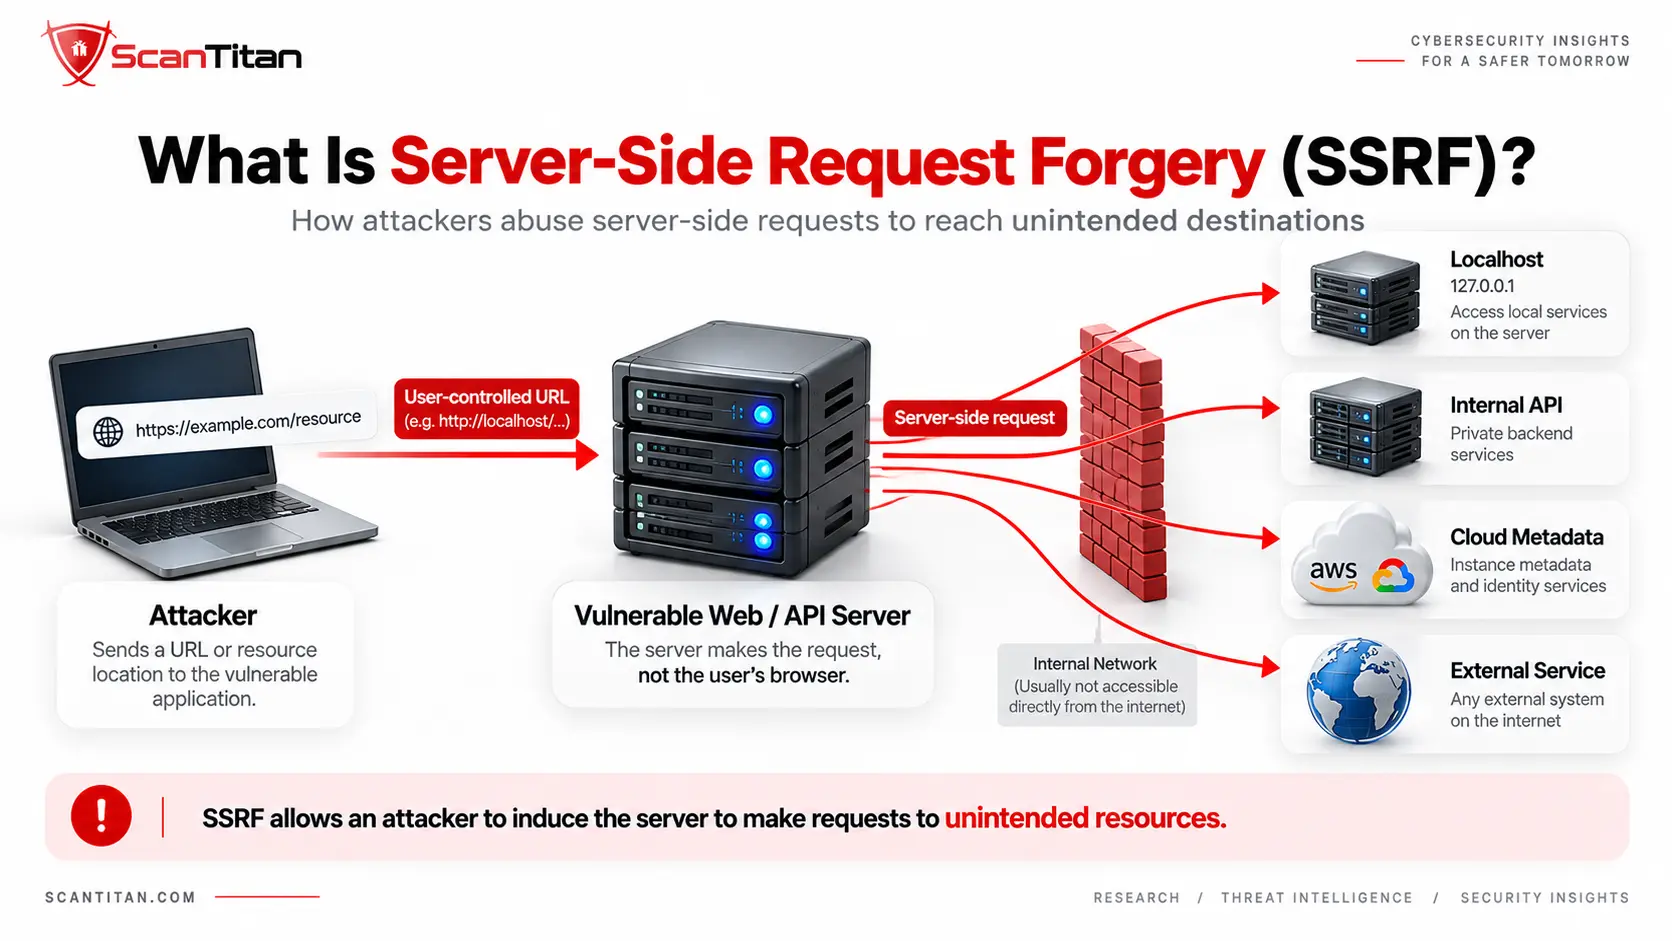
Server-Side Request Forgery (SSRF) is a web application security vulnerability in which attacker-controlled input causes a server-side component to send a network request to an unintended destination. The defining characteristic
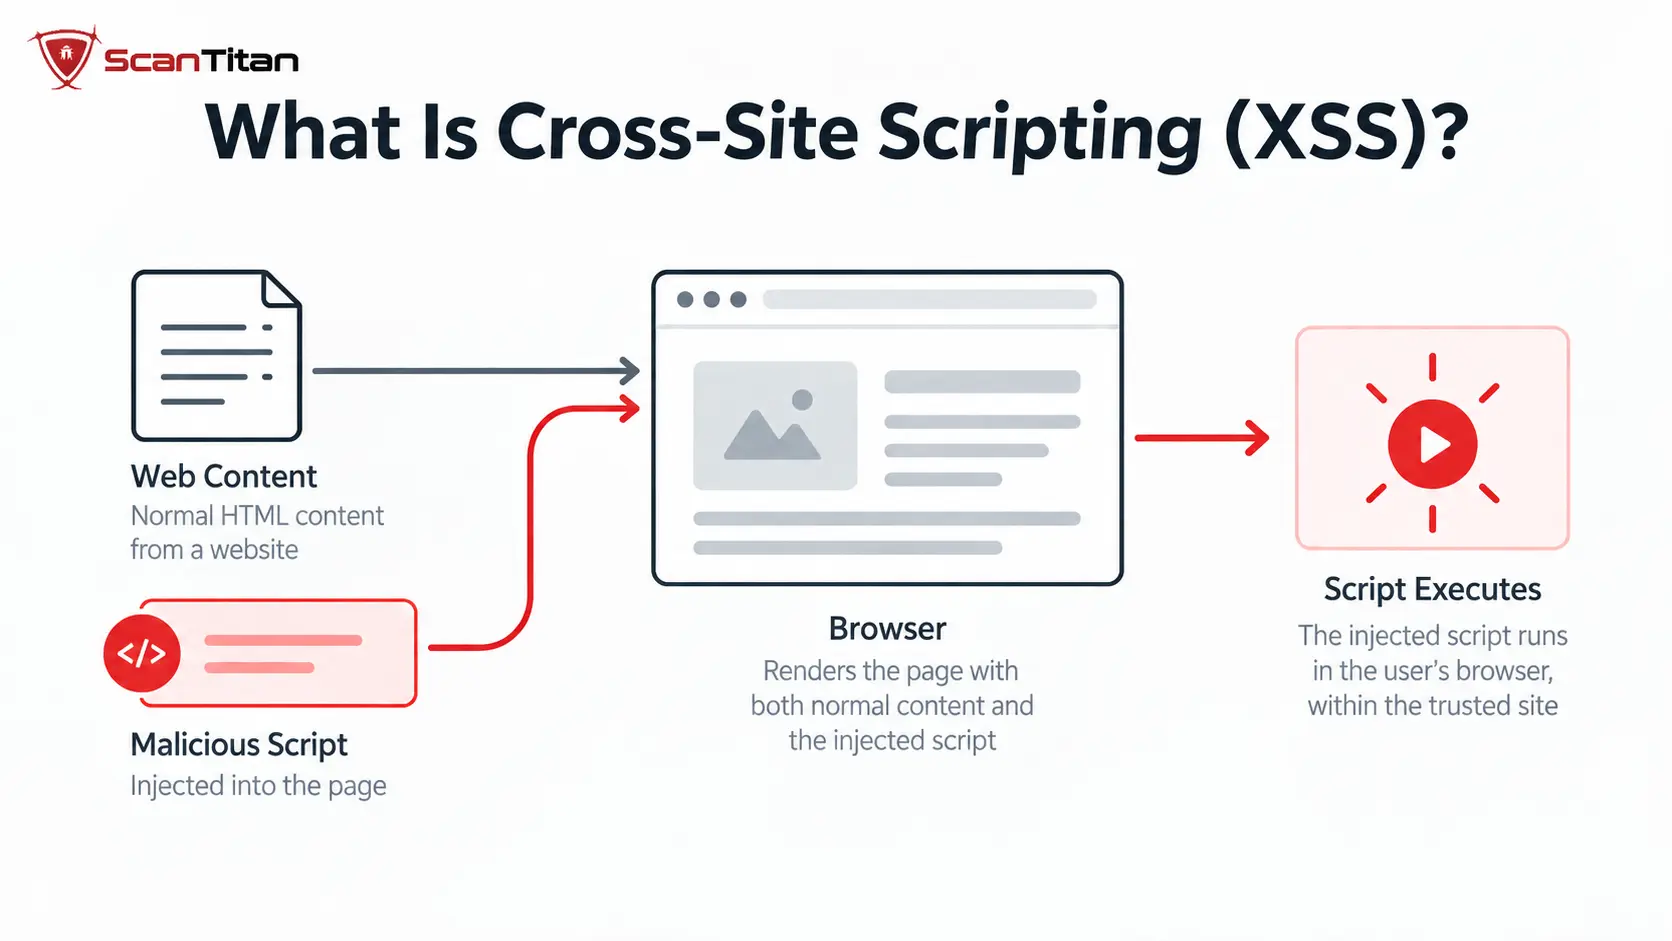
Cross-site scripting (XSS) is a web application vulnerability that allows untrusted data to reach a browser in a context where the browser interprets it as executable code instead of ordinary
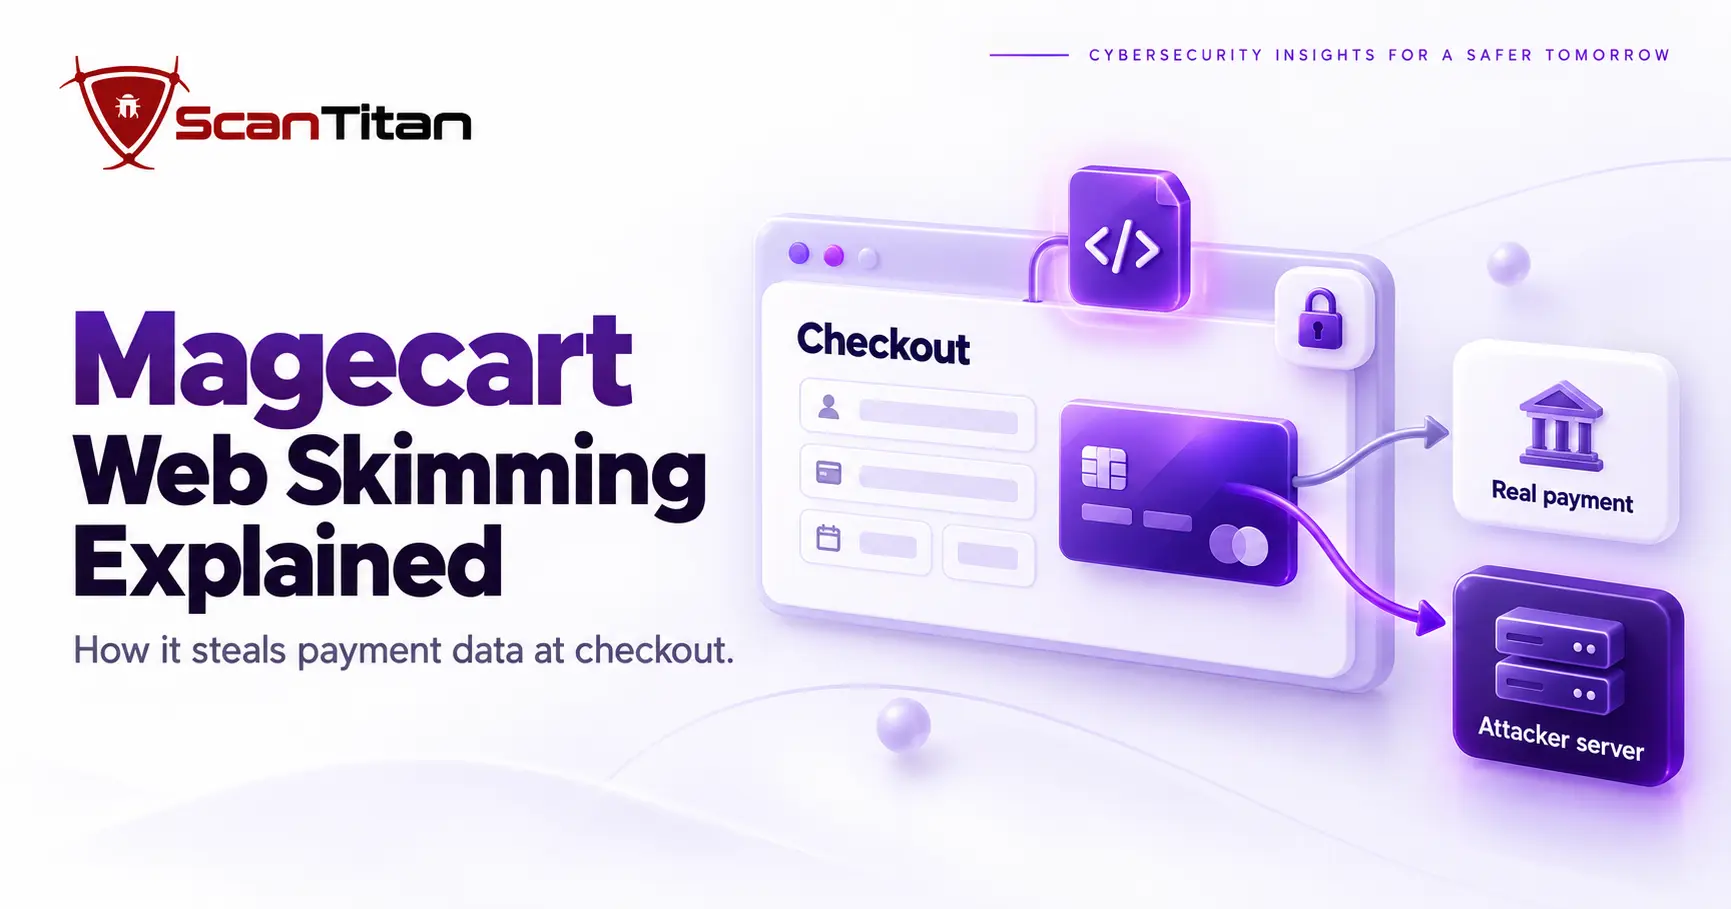
Magecart is the name for criminal groups that steal payment card data from online checkout pages, usually by planting JavaScript that copies card details while the real purchase goes through.
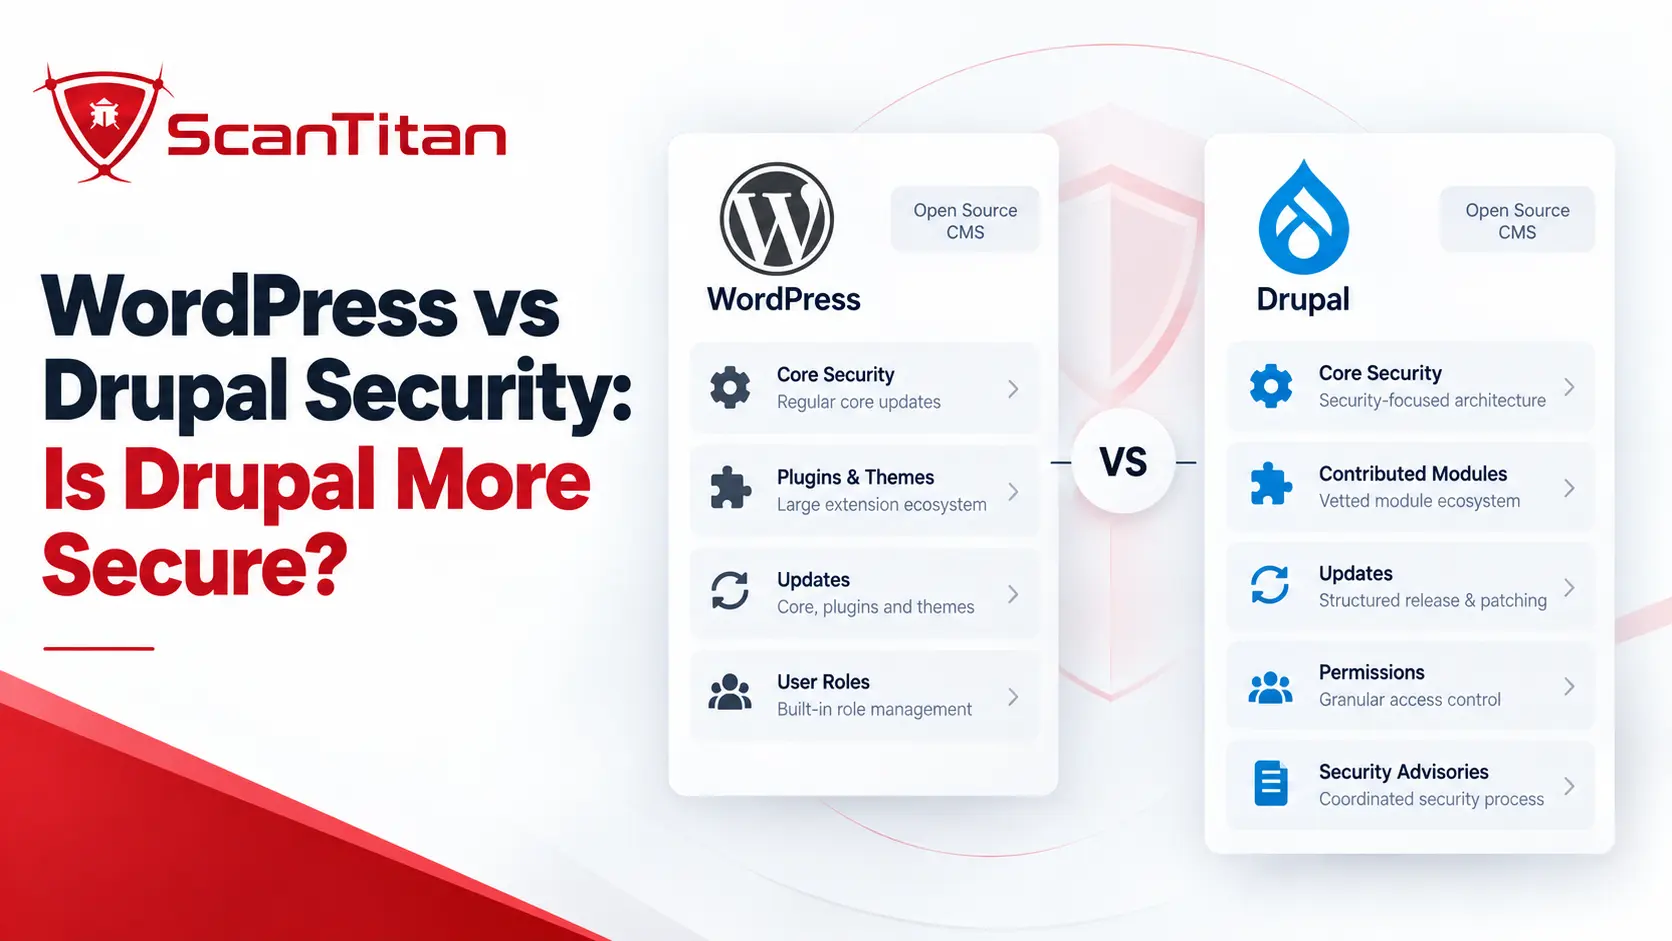
WordPress vs Drupal security is not as simple as comparing vulnerability counts. Drupal generally provides stronger security and governance defaults for complex, multi-user websites, especially around permissions, configuration management, and
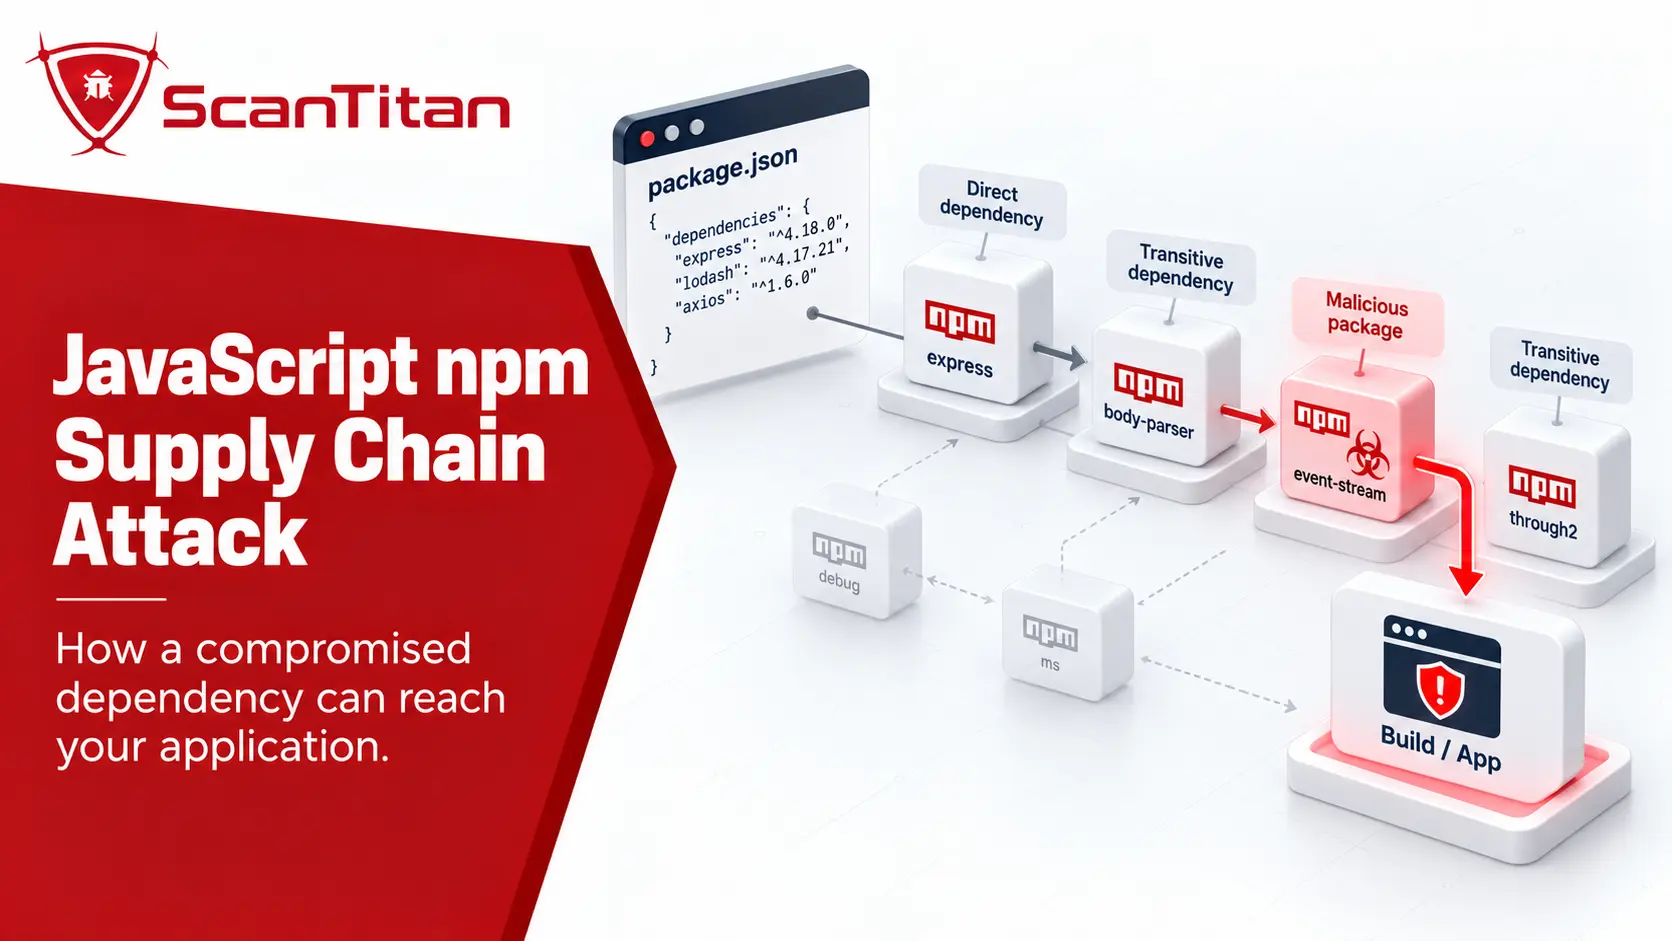
A JavaScript npm supply chain attack targets the software and infrastructure between an npm package maintainer and the application that eventually installs that package. Instead of exploiting a flaw in
This guide will tell you how to monitor your website availability and uptime by using ScanTitan free online website monitor. As the world evolves today, websites become an increasingly vital
This guide will tell you how to scan your website against malware which includes viruses, webshells, malicious javascript and others by using ScanTitan free website malware scanner. What is website
This guide will tell you how to find your website security vulnerabilities and weakness by using ScanTitan free online vulnerability scanner. What is website vulnerability? According to research, it has
This guide will tell you how to reduce your website and online services attack surface by finding your security exposures using ScanTitan free online vulnerability scanner. What is website security
This guide will tell you how to know your network exposure and running services on your edge device like a firewall or router and how to monitor network exposure using
This article will guide you on how to monitor your cyber brand security using ScanTitan cyber brand monitoring to prevent digital image issues, traffic drops, and your customer trust loss.
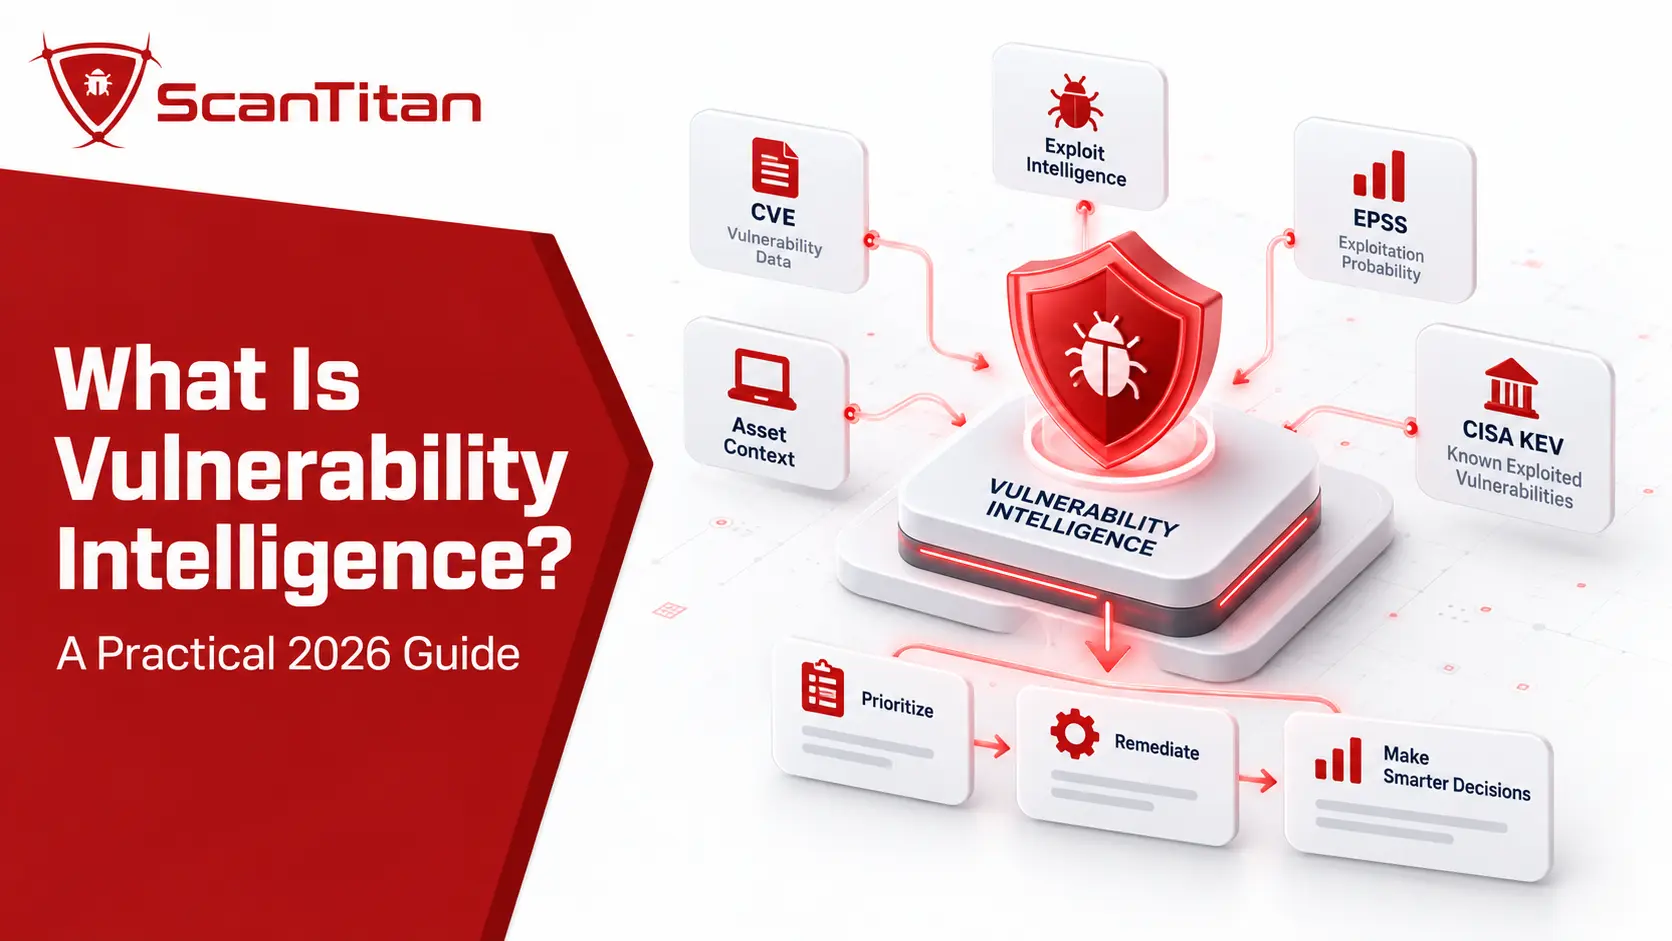
Vulnerability intelligence is the process of turning raw vulnerability data into decisions about what to fix first. It combines CVE records with exploit activity, technical severity, affected products, patch status,
This guide will tell you what is cyber threat intelligence and how it is important to identify relevant threats of your business using ScanTitan Threat Intelligence platform. What is Threat
PHP2Shell is the name researchers gave to two critical PHP core flaws, CVE-2026-109618 and CVE-2026-109619, that let an unauthenticated attacker run code on a server through ordinary web requests. The
Command injection, usually referring to OS command injection, is a security vulnerability in which attacker-controlled input changes an operating-system command executed by an application, allowing unintended command behavior or additional
An exposed .env file vulnerability occurs when a web server allows unauthorized users to retrieve an environment configuration file. A publicly accessible .env file can reveal database credentials, API keys,
The OWASP API Top 10 is a ranked list of the ten most critical API security risks, and the 2023 edition is still the current version. It covers broken authorization,
The best vulnerability scanning tools in 2026 depend on what you need to scan. ScanTitan, Intruder, and HostedScan serve small teams that want cloud scanning without a security department, Tenable
An exposed backup files vulnerability occurs when a backup, database dump, old source-code copy, deployment archive, or editor-generated file is publicly accessible from a web server. Files such as config.php.bak,
XML External Entity (XXE) Injection is a web security vulnerability in which an application processes attacker-controlled XML with a parser that is allowed to resolve external entities or other external
A directory listing vulnerability occurs when a web server exposes a browsable index of files and subdirectories that were not intended to be discovered this way. Instead of returning an
Insecure Direct Object Reference (IDOR) is an access control vulnerability in which an application uses a user-controllable reference to retrieve, change, delete, or otherwise act on an object without verifying
WordPress user enumeration is the process of discovering information that identifies valid WordPress accounts, such as user IDs, display names, author slugs, author URLs, or whether an account exists. WordPress
A CORS misconfiguration occurs when a web application allows an untrusted origin to read cross-origin responses that should only be available to trusted websites. Common causes include reflecting arbitrary Origin
Cross-Site Request Forgery (CSRF) is a web security vulnerability in which an attacker causes a user’s browser to send an unintended request to an application that accepts the user’s automatically
WordPress core files modified is a scanner alert that means a file in your install no longer matches the official release for your version. It is not always a hack.
The best Sucuri alternatives cover some or all of what Sucuri sells: a firewall, WordPress protection, hack cleanup and website scanning. This guide ranks six of them by how many
Is your website blacklisted by Google? Google has no single blacklist. A site can sit on Google’s Safe Browsing list, which triggers security warnings, carry a manual action, which is
A website flagged as phishing is a site that a browser, security vendor or email filter has classified as a fake login or credential trap. The cause is either a
.htaccess malware is malicious configuration code that an attacker writes into the Apache .htaccess file, which the server reads before WordPress loads. It can redirect search visitors, run image files
A cloaking hack in WordPress is malicious code that shows spam to Google and a normal site to you, so the dashboard and your own browser look clean while search
Nulled plugins malware is malicious code hidden in a pirated copy of a premium WordPress plugin, installed by an owner who wanted it for free. The code runs with the
A site still blocklisted after cleanup is rarely a mystery. The flag stays because you are still waiting for a review, part of the infection is still there, or a
Malicious JavaScript on website pages is script code that an attacker planted so it runs in your visitors’ browsers. It loads from a theme file, a database row, a third-party
WordPress mu-plugin malware is malicious PHP placed in the wp-content/mu-plugins folder, where WordPress loads it on every request without activation, so it never shows as an active plugin. Attackers use
Hidden admin user WordPress infections are administrator accounts that exist in the database but are filtered out of the Users screen by code, so the dashboard shows nothing unusual. Attackers
The 12 signs of website malware fall into five groups: what visitors see, what Google shows, what you see in the dashboard, what the server’s files and logs show, and
12+ years in information security. Specialises in web application security, vulnerability management, and external attack surface reduction for SMB and mid-market organisations.
New CVEs, practical guides, and scan methodology updates. One email per week. No sales pitch.
No spam. Unsubscribe any time. GDPR compliant.
Editorial standards: All ScanTitan blog content is reviewed by certified InfoSec professionals before publication. Technical claims are tested against live scan results or cited from primary sources (CVE database, OWASP, NIST NVD). We do not accept sponsored posts or paid placements.
Try a free scan
Run a free vulnerability scan on your domain. No account required.