Guides and analysis on website and network vulnerability scanning — from understanding CVEs to automated vs manual scanning methods.
No vendor fluff. No recycled threat reports. Real guidance on vulnerability scanning, malware, and attack surface management — written by practitioners.
Command injection, usually referring to OS command injection, is a security vulnerability in which attacker-controlled input changes an operating-system command executed by an application, allowing unintended command behavior or additional commands to run with the application’s privileges, The core trust boundary is straightforward: the attacker influences data, the application turns that data into part of […]
An exposed .env file vulnerability occurs when a web server allows unauthorized users to retrieve an environment configuration file. A publicly accessible .env file can reveal database credentials, API keys, application secrets, cloud credentials, mail passwords, signing keys, and other configuration values that were intended to remain server-side.The severity depends on what the file contains […]
The OWASP API Top 10 is a ranked list of the ten most critical API security risks, and the 2023 edition is still the current version. It covers broken authorization, broken authentication, resource abuse, server-side request forgery, misconfiguration, and unsafe use of third-party APIs. This guide explains all ten risks with an attack example, a […]
The best vulnerability scanning tools in 2026 depend on what you need to scan. ScanTitan, Intruder, and HostedScan serve small teams that want cloud scanning without a security department, Tenable Nessus, Qualys VMDR, and Rapid7 InsightVM cover servers and networks, and Invicti, Burp Suite DAST, and Detectify test running web applications. This guide compares ten […]
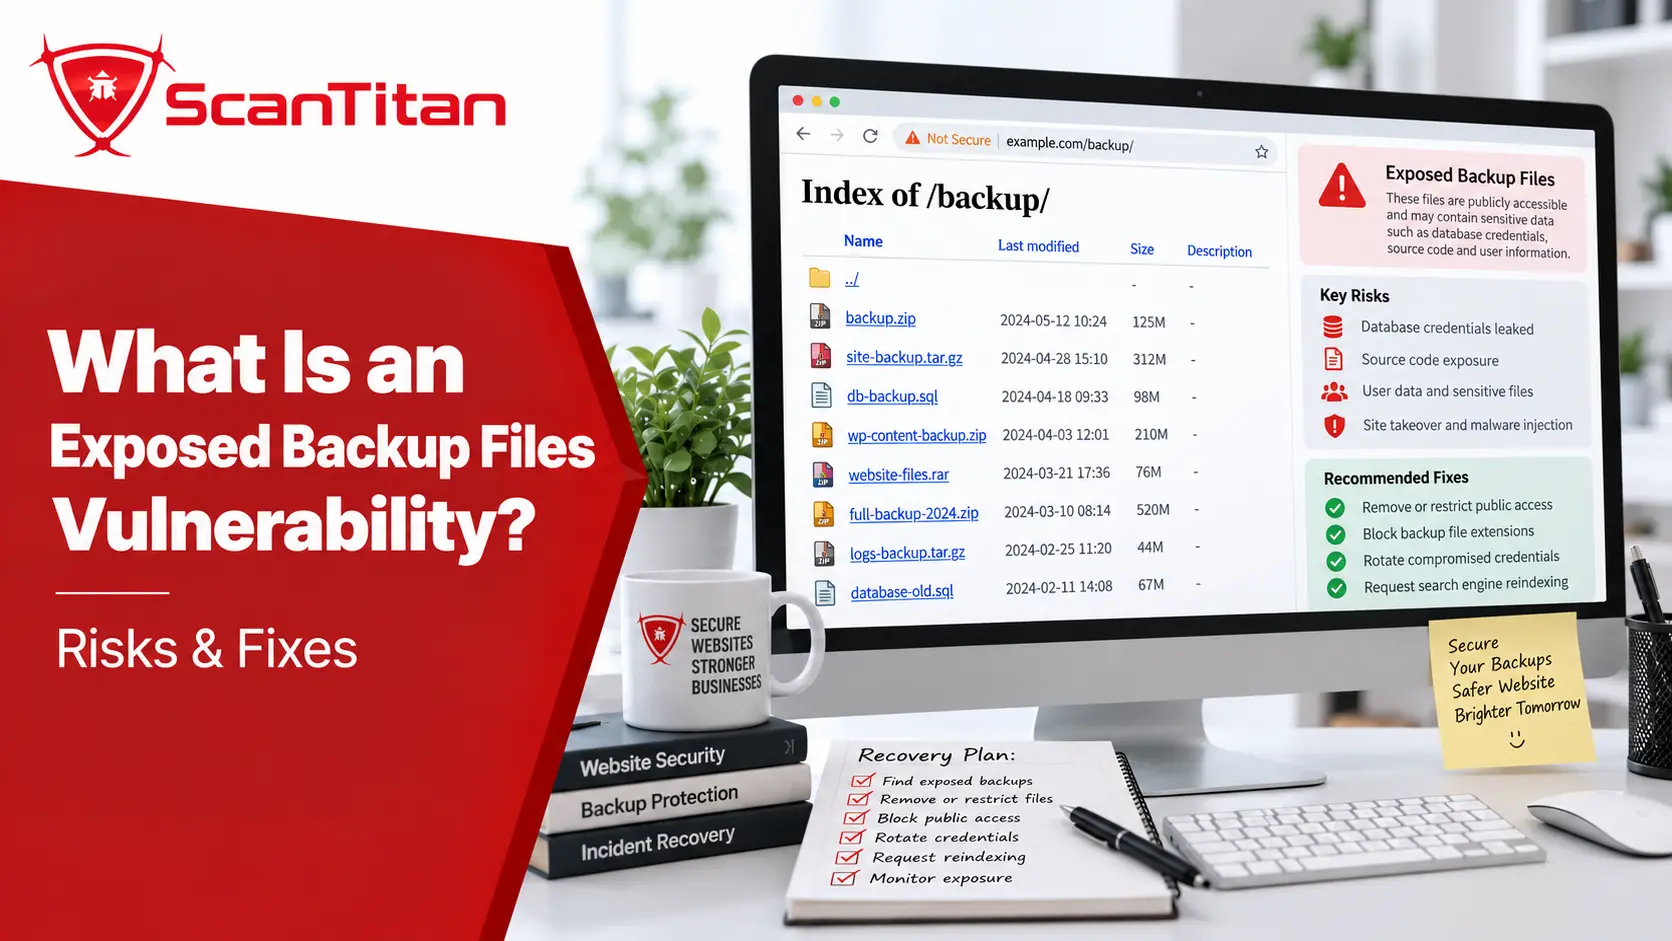
An exposed backup files vulnerability occurs when a backup, database dump, old source-code copy, deployment archive, or editor-generated file is publicly accessible from a web server. Files such as config.php.bak, database.sql, site-backup.zip, or index.php~ can reveal source code, credentials, private data, and internal application details.The impact depends on what the backup contains. An obsolete static […]
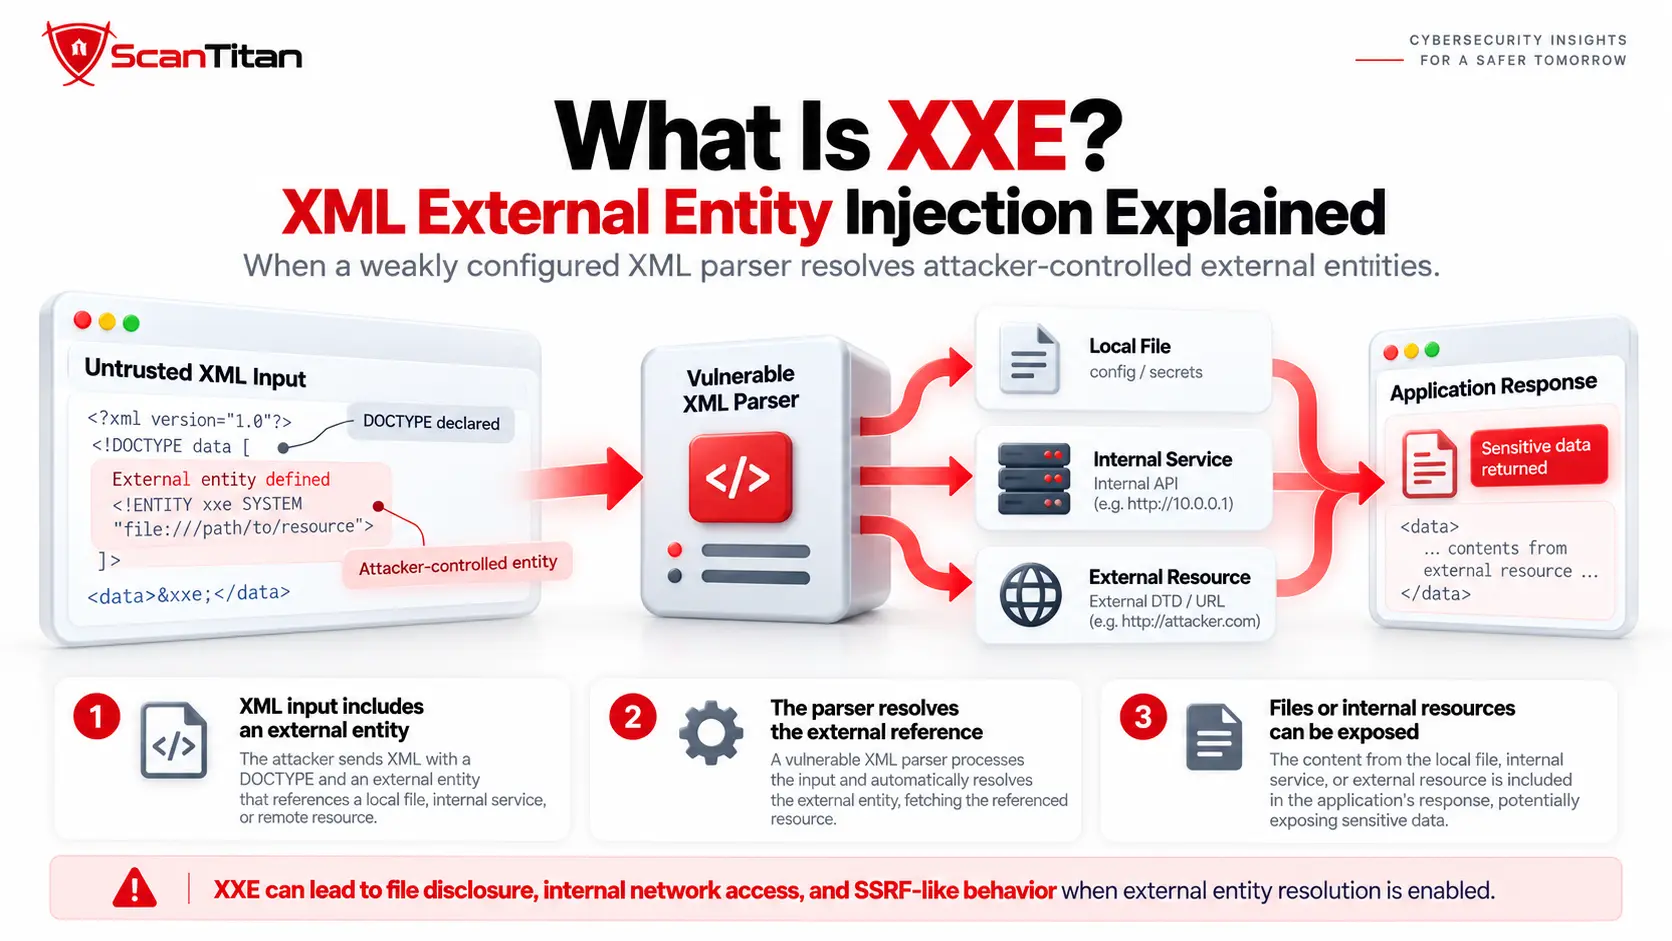
XML External Entity (XXE) Injection is a web security vulnerability in which an application processes attacker-controlled XML with a parser that is allowed to resolve external entities or other external XML resources. That unsafe parser behavior can expose local files, trigger server-side requests to internal or external systems, or create other unintended resource access. The […]
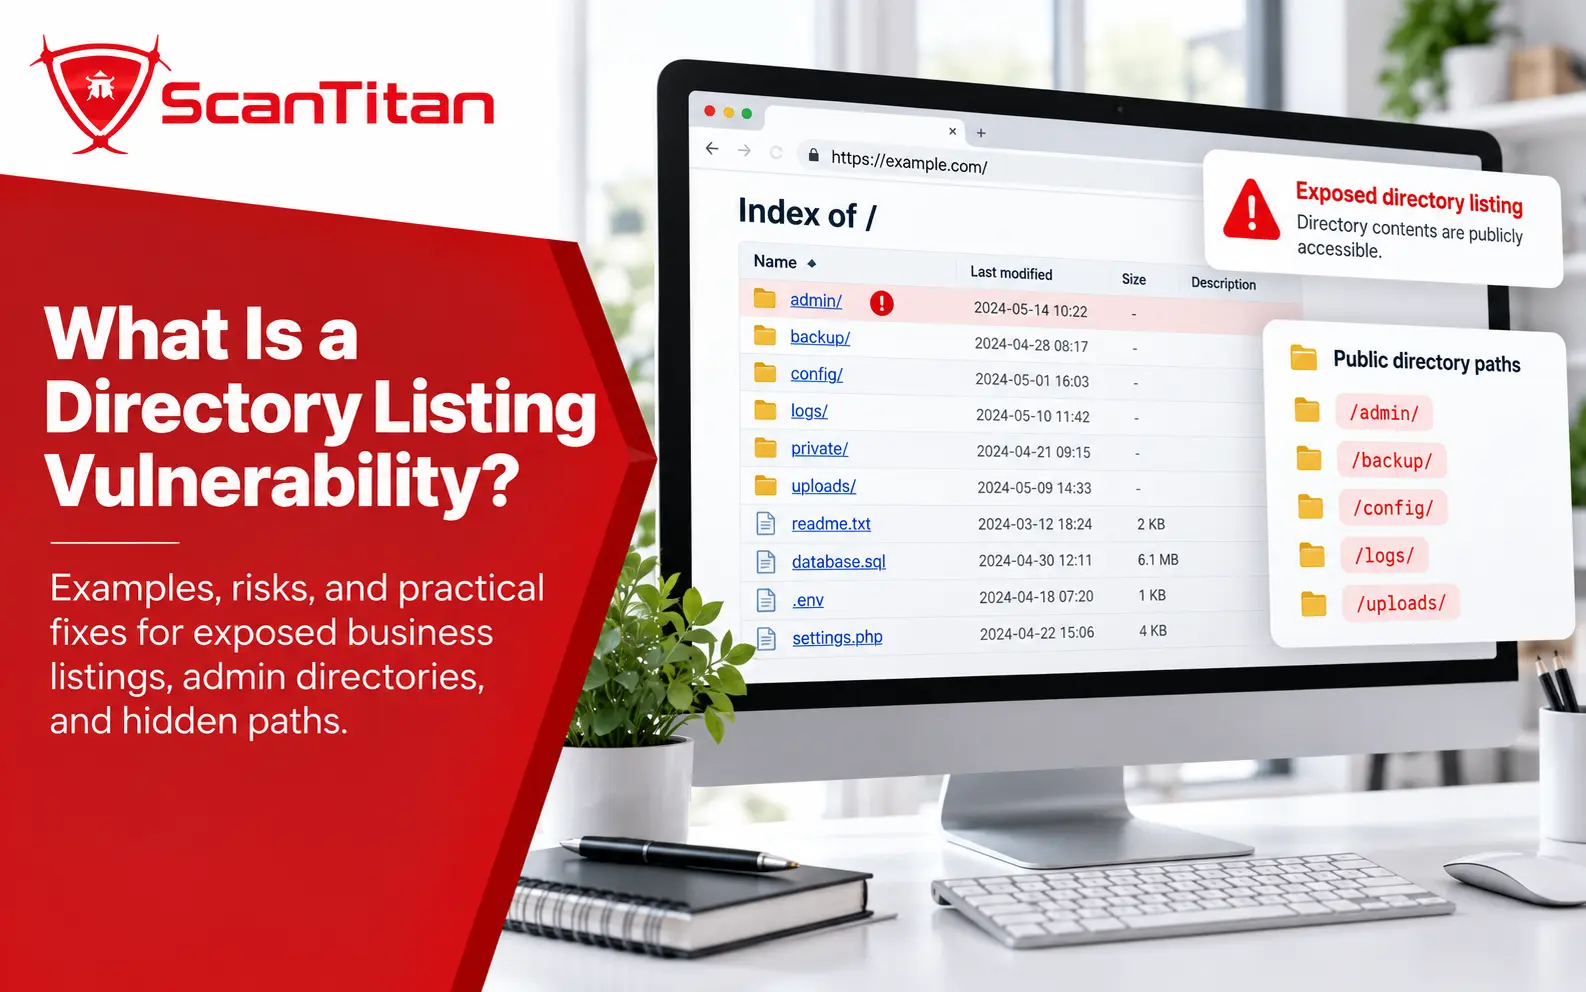
A directory listing vulnerability occurs when a web server exposes a browsable index of files and subdirectories that were not intended to be discovered this way. Instead of returning an index page or denying access, the server generates a list that can reveal filenames, backup archives, configuration files, logs, source code, database exports, or internal […]
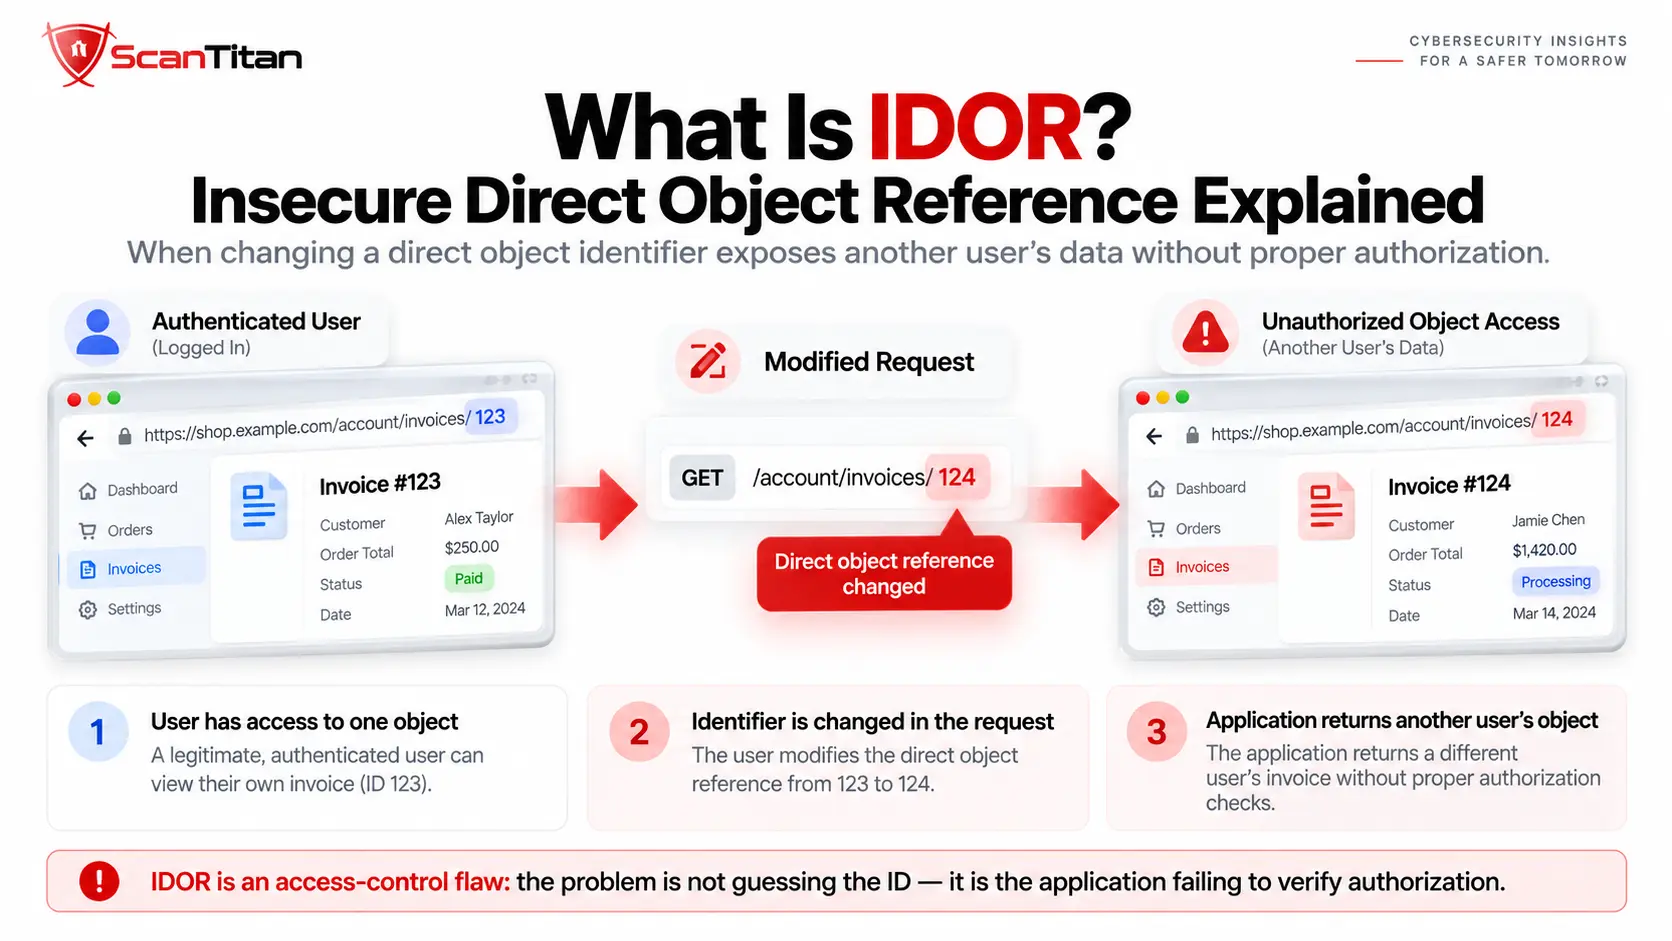
Insecure Direct Object Reference (IDOR) is an access control vulnerability in which an application uses a user-controllable reference to retrieve, change, delete, or otherwise act on an object without verifying that the requester is authorized to perform that action on that specific object.The central mistake is confusing authentication with authorization. Authentication answers “Who are you?” […]
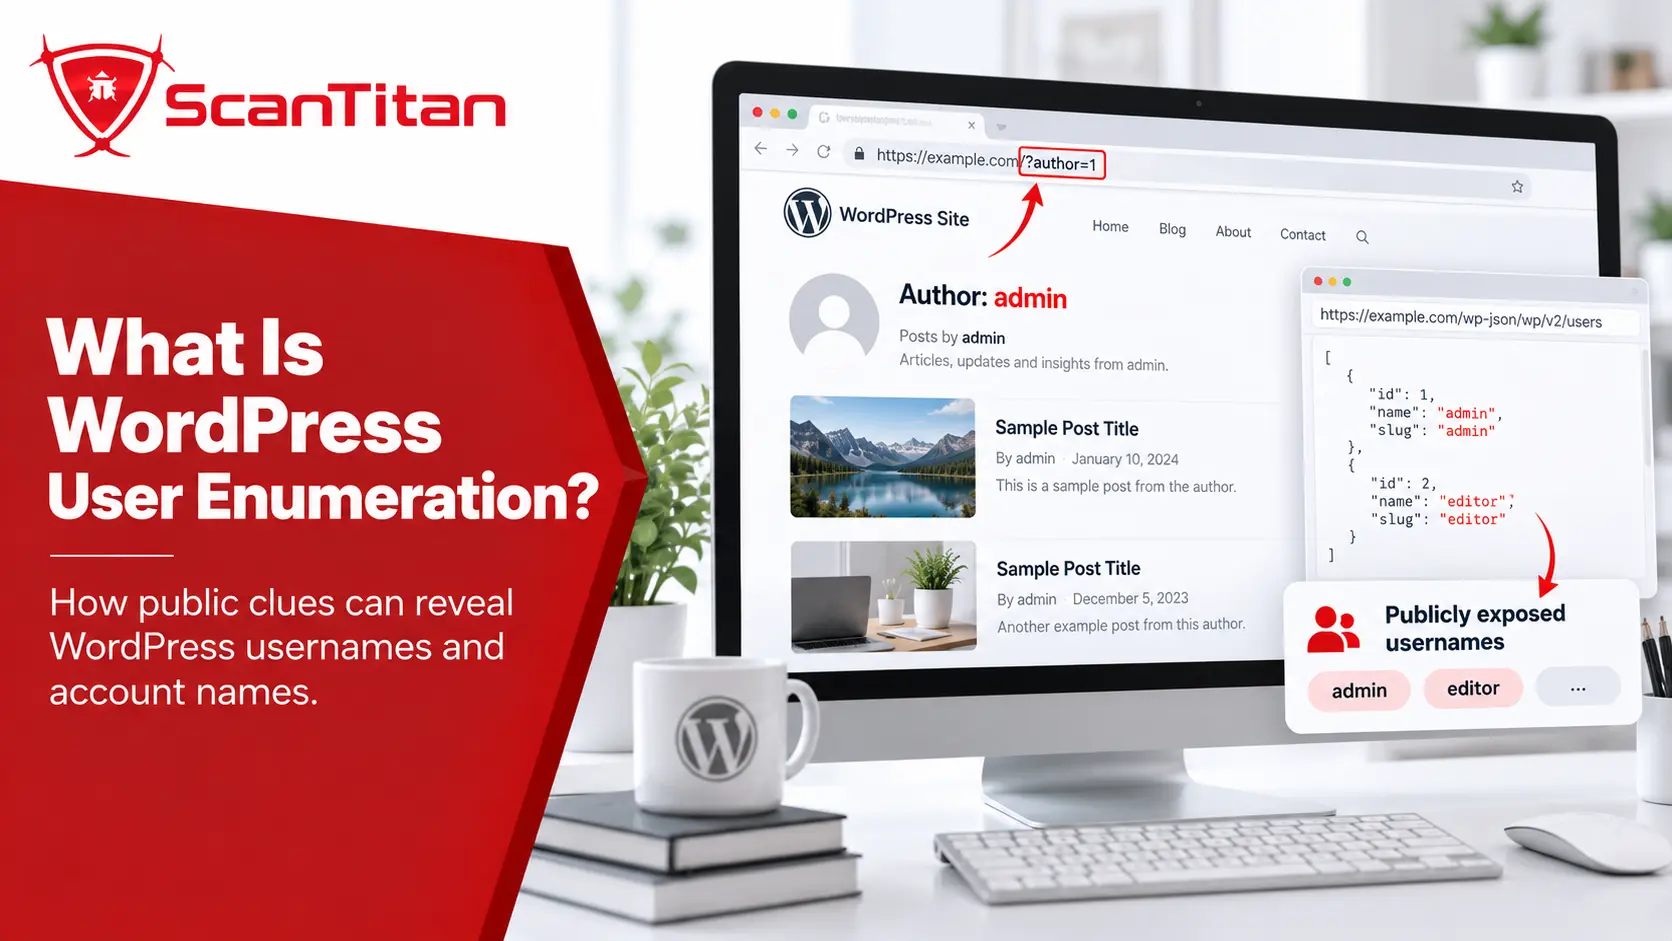
WordPress user enumeration is the process of discovering information that identifies valid WordPress accounts, such as user IDs, display names, author slugs, author URLs, or whether an account exists. WordPress can expose some of this information intentionally through author pages, REST API responses, sitemaps, and login behavior. Enumeration does not bypass authentication and does not […]
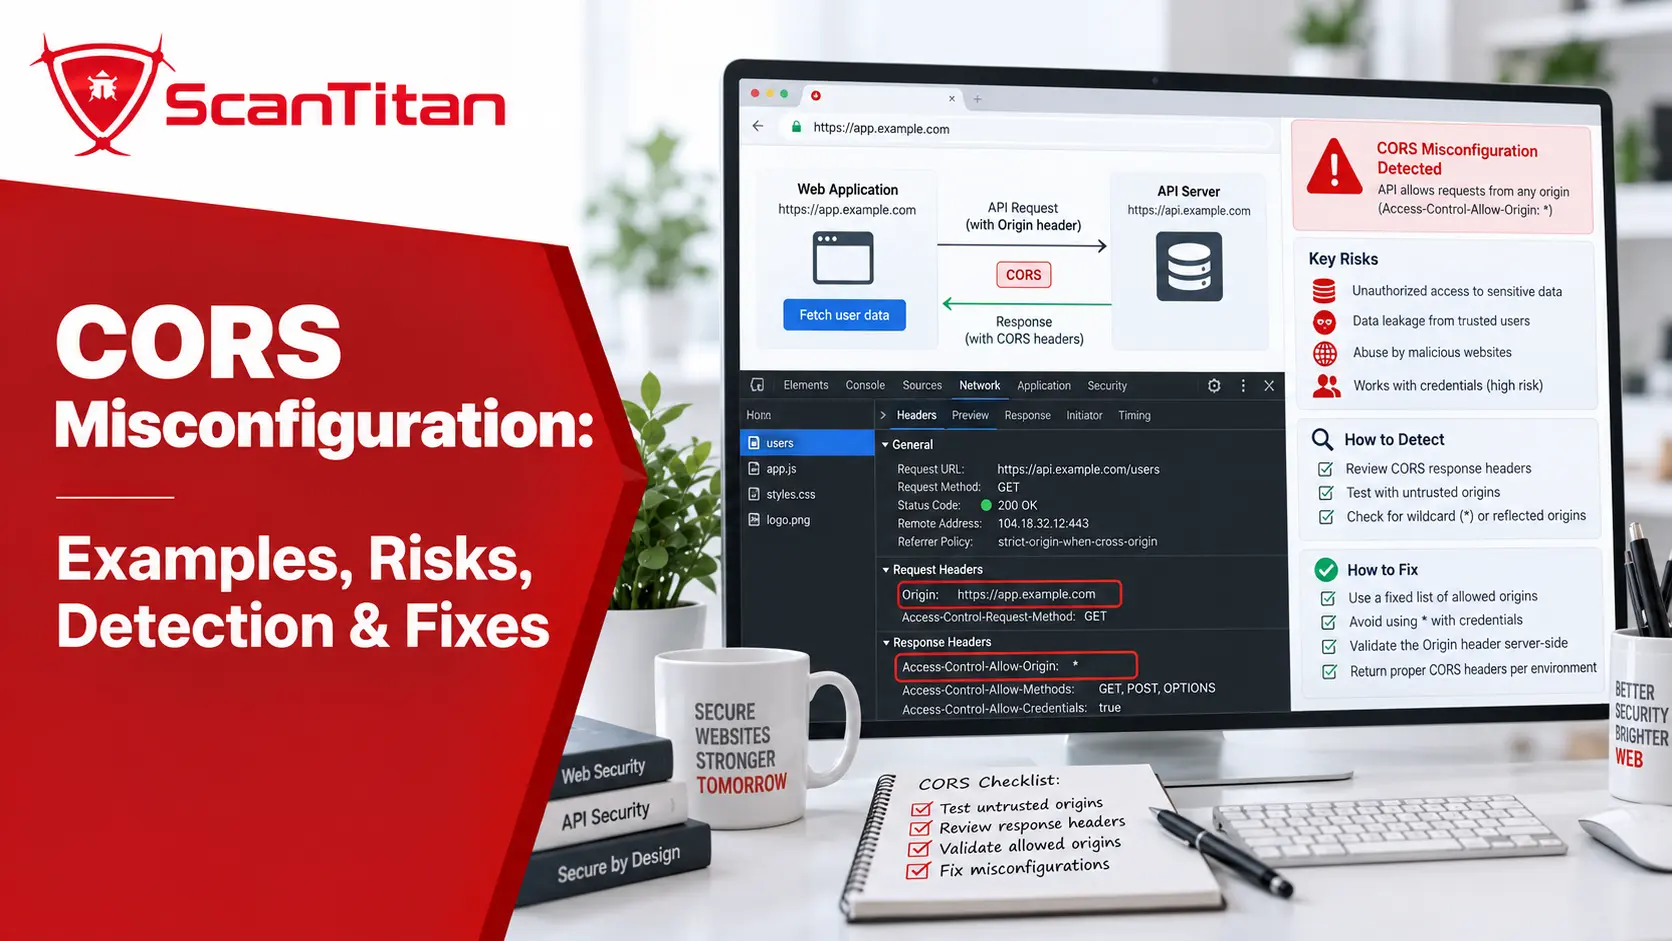
A CORS misconfiguration occurs when a web application allows an untrusted origin to read cross-origin responses that should only be available to trusted websites. Common causes include reflecting arbitrary Origin values, weak origin validation, trusting null, or allowing origins that attackers can control.Not every permissive CORS response is an exploitable vulnerability. The real risk depends […]
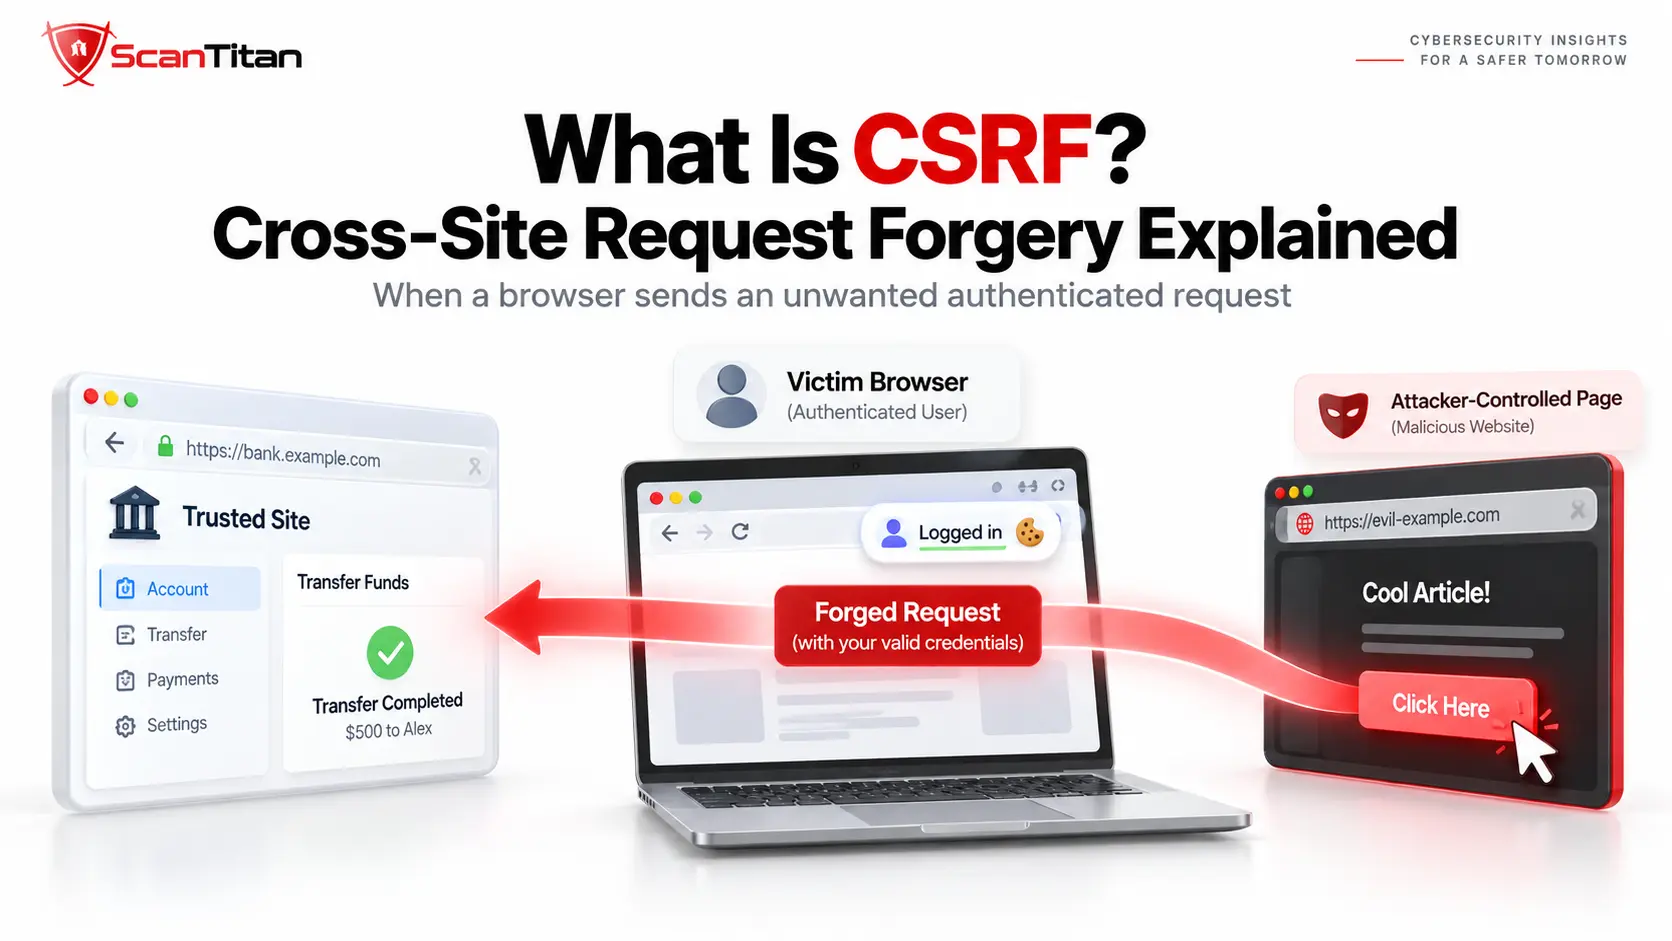
Cross-Site Request Forgery (CSRF) is a web security vulnerability in which an attacker causes a user’s browser to send an unintended request to an application that accepts the user’s automatically supplied credentials or authority. The browser may be authenticated, but the application fails to verify that the user actually intended the action.That distinction is the […]
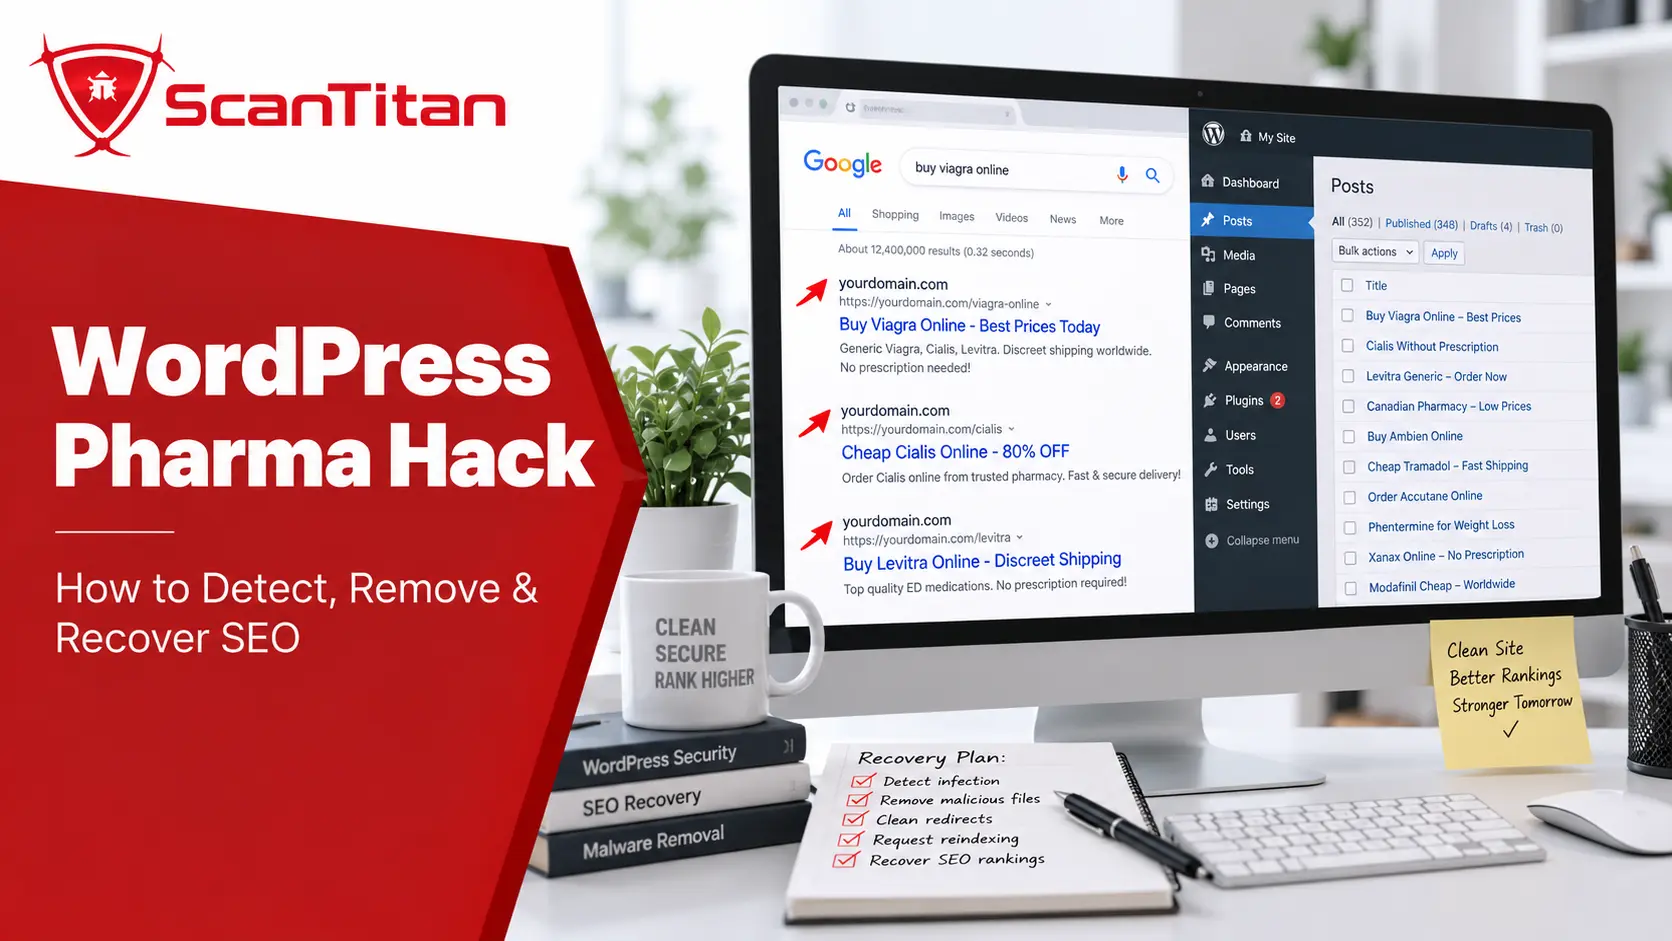
A WordPress pharma hack is a post-compromise SEO spam infection that adds pharmaceutical keywords, links, pages, redirects, or hidden content to a WordPress website without the owner’s permission. It is also commonly called a Viagra hack, pharmaceutical spam hack, or pharma SEO spam.The infection can be confusing because the website may look normal when you […]
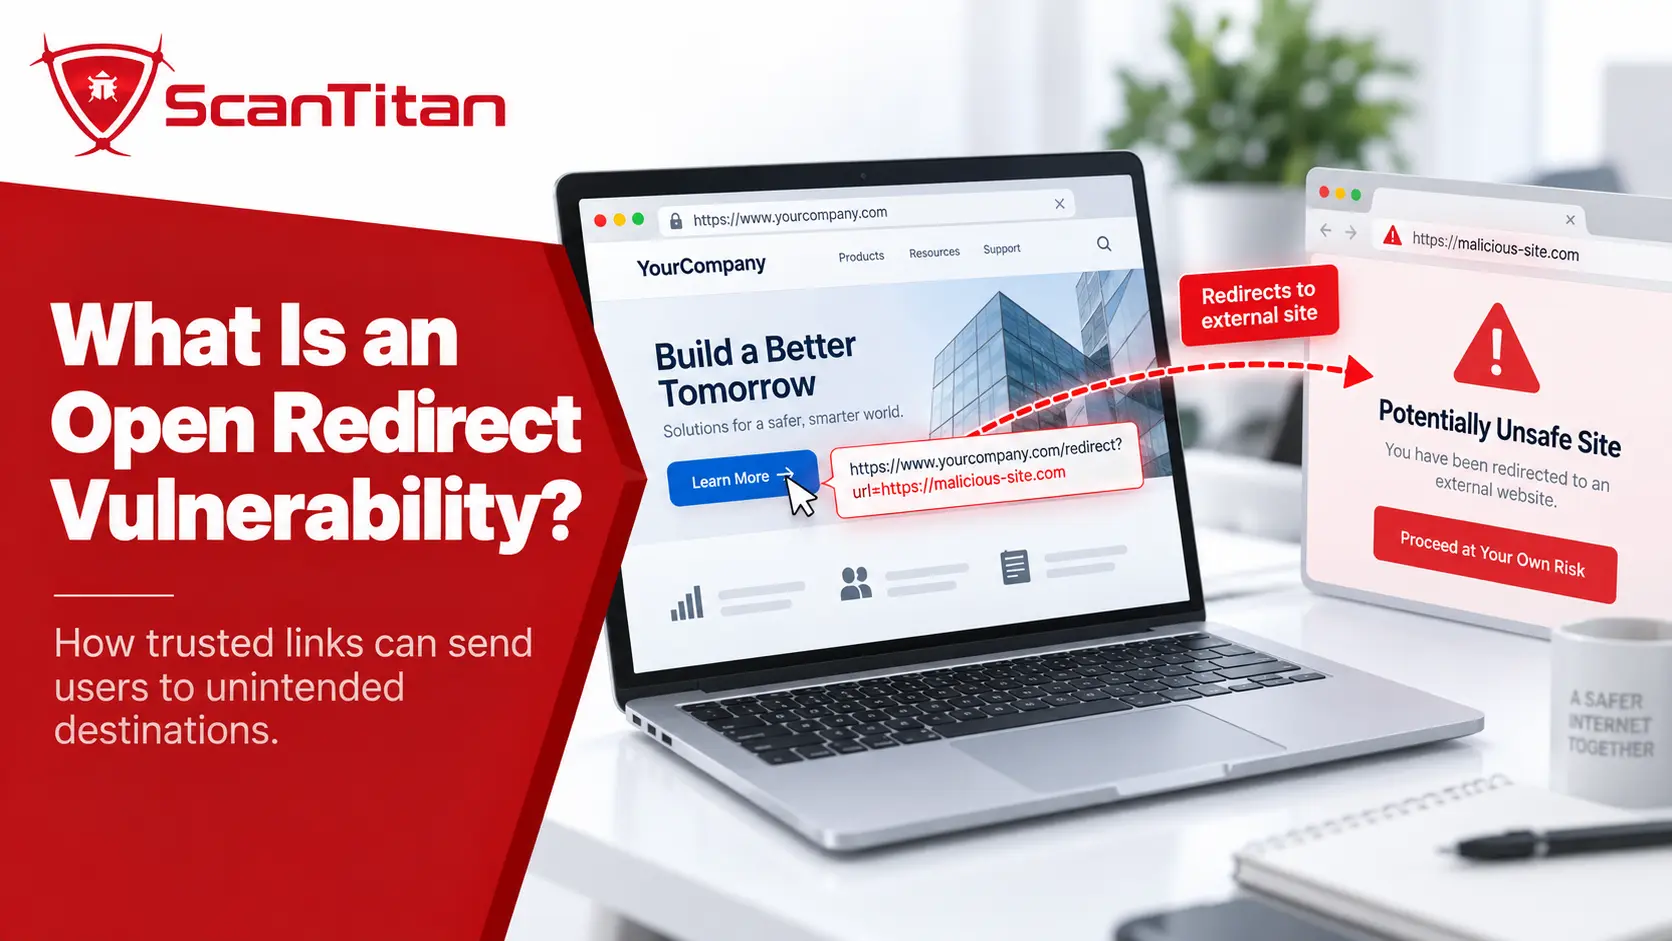
An open redirect vulnerability occurs when a web application lets attacker-controlled input determine where a user is redirected without sufficiently restricting the final destination. An attacker can then create a link that begins on a legitimate domain but sends the victim to an external site chosen by the attacker.The simplest impact is phishing: the trusted […]
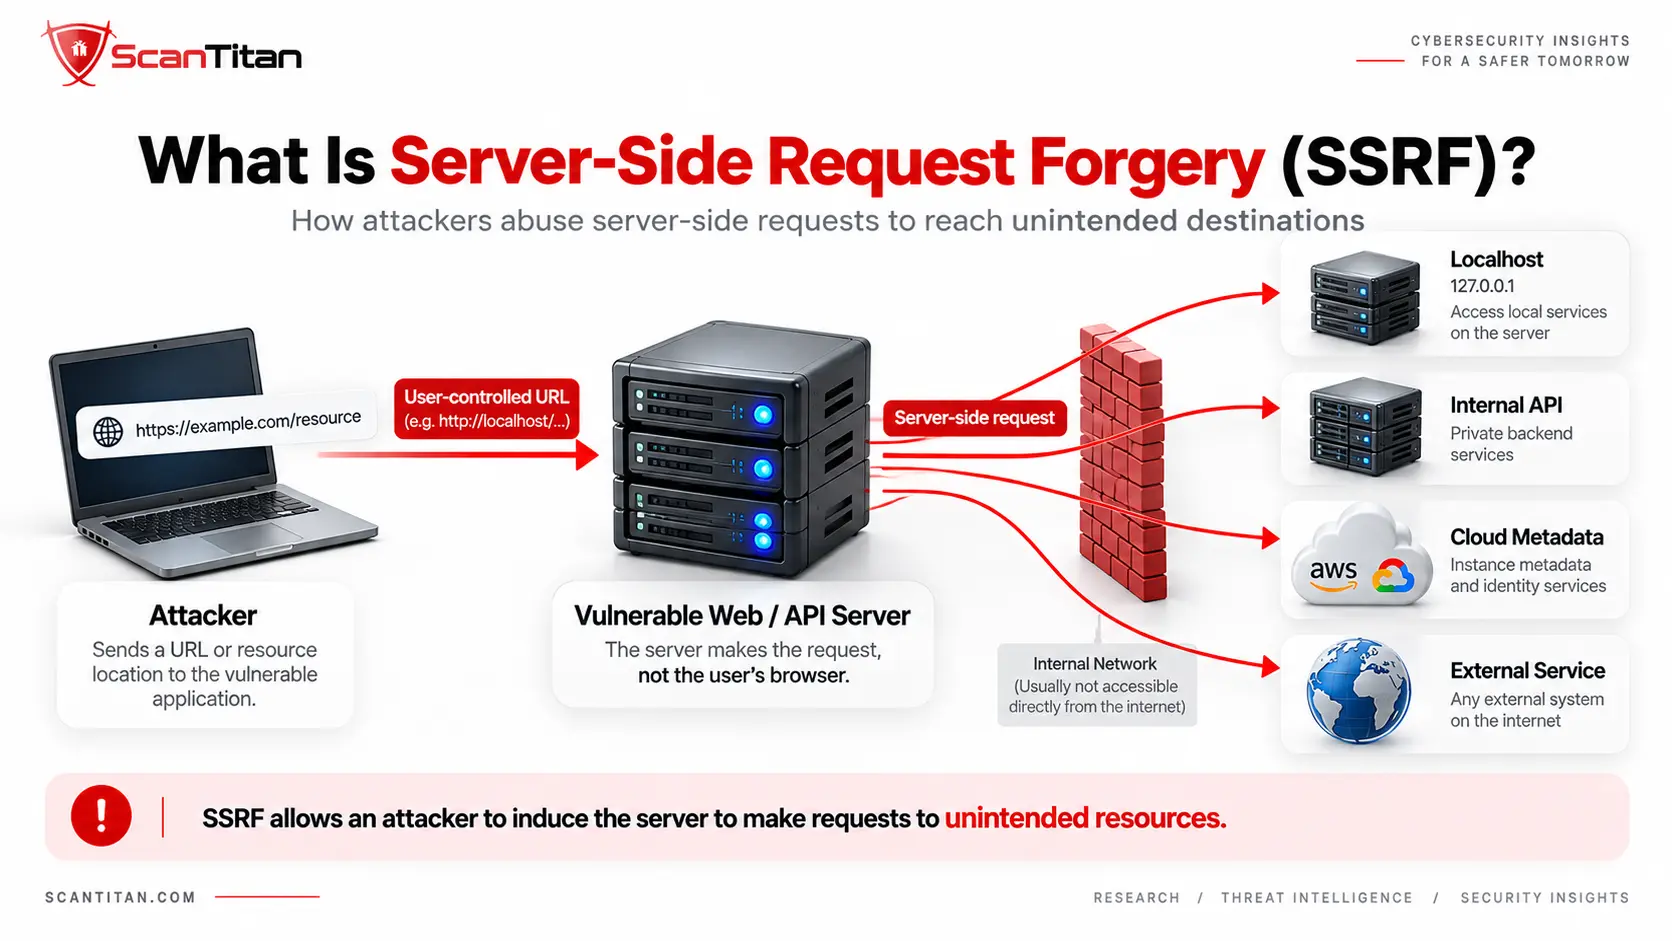
Server-Side Request Forgery (SSRF) is a web application security vulnerability in which attacker-controlled input causes a server-side component to send a network request to an unintended destination. The defining characteristic is that the sensitive request originates from the server, not from the attacker’s browser.That distinction matters because an application server may be able to reach […]
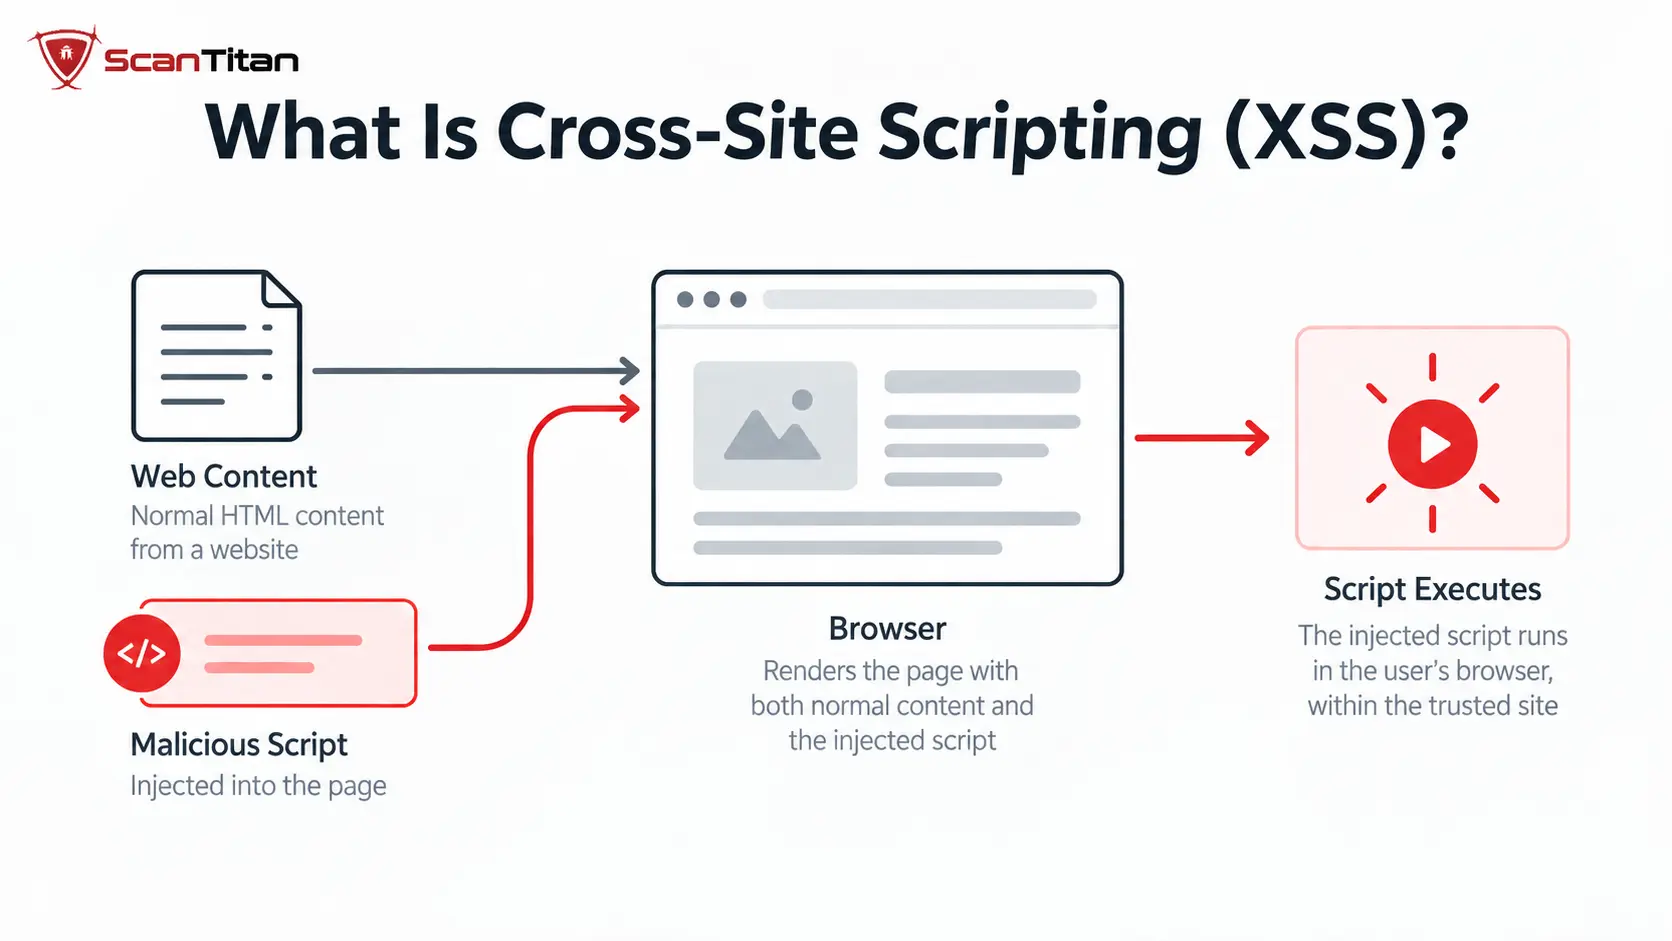
Cross-site scripting (XSS) is a web application vulnerability that allows untrusted data to reach a browser in a context where the browser interprets it as executable code instead of ordinary content. The attacker does not need to compromise the browser itself. The vulnerable website delivers or processes the attacker-controlled content in a way that makes […]
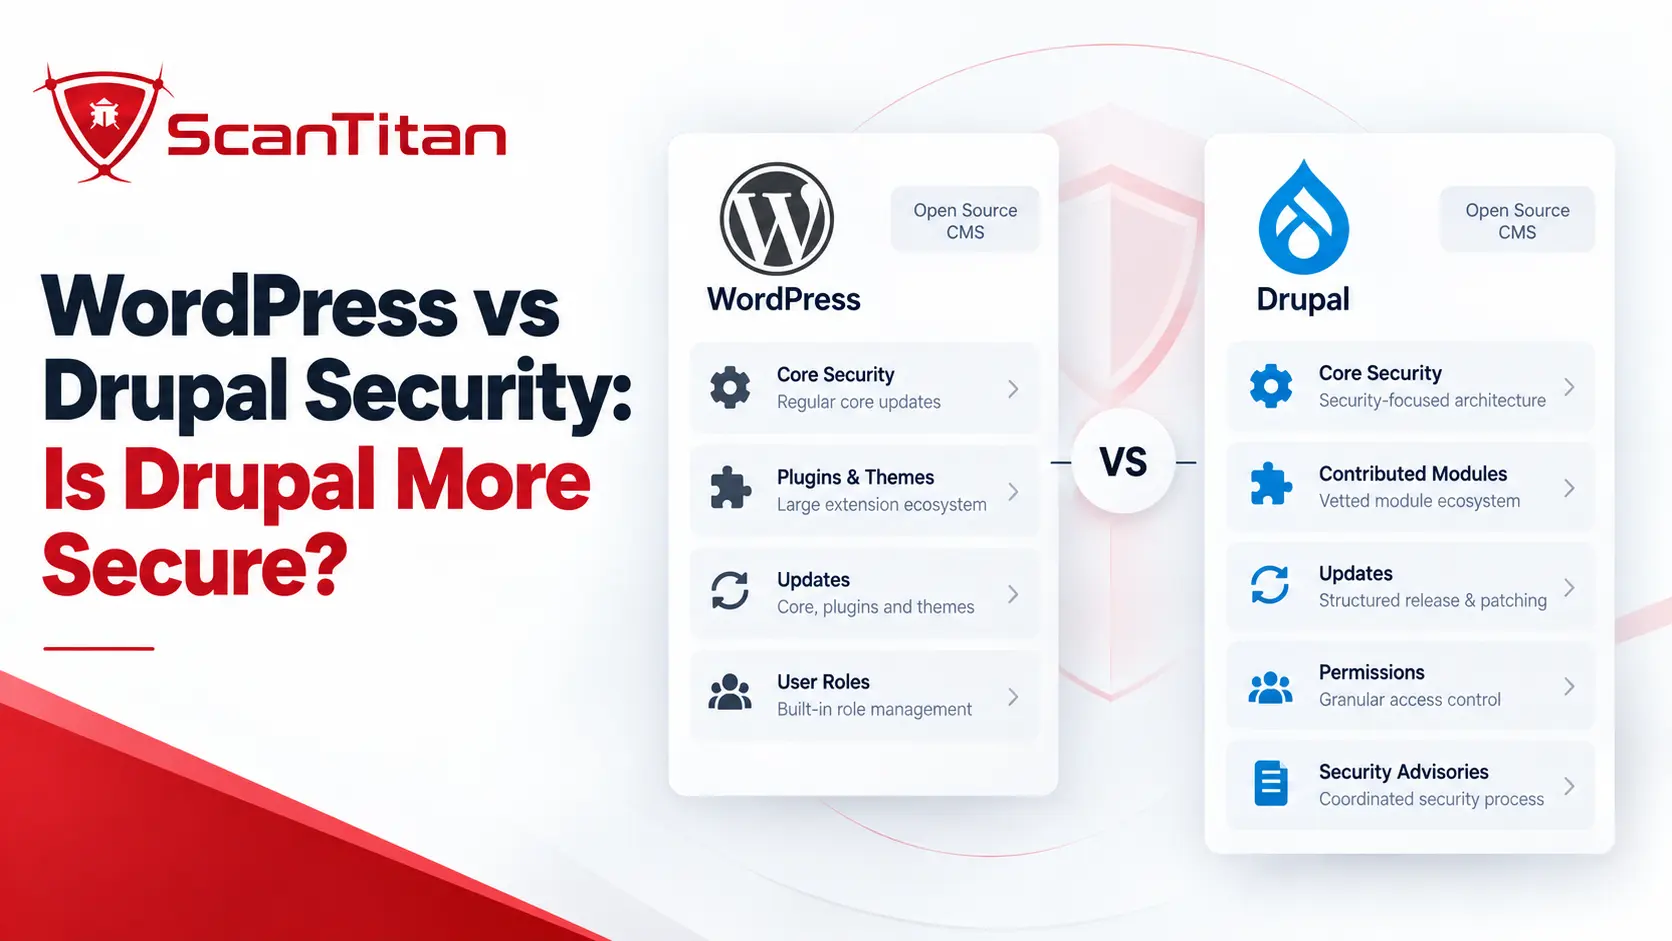
WordPress vs Drupal security is not as simple as comparing vulnerability counts. Drupal generally provides stronger security and governance defaults for complex, multi-user websites, especially around permissions, configuration management, and controlled deployments. WordPress core also has a mature security process and stronger native update automation, but its enormous plugin and theme ecosystem creates more third-party […]
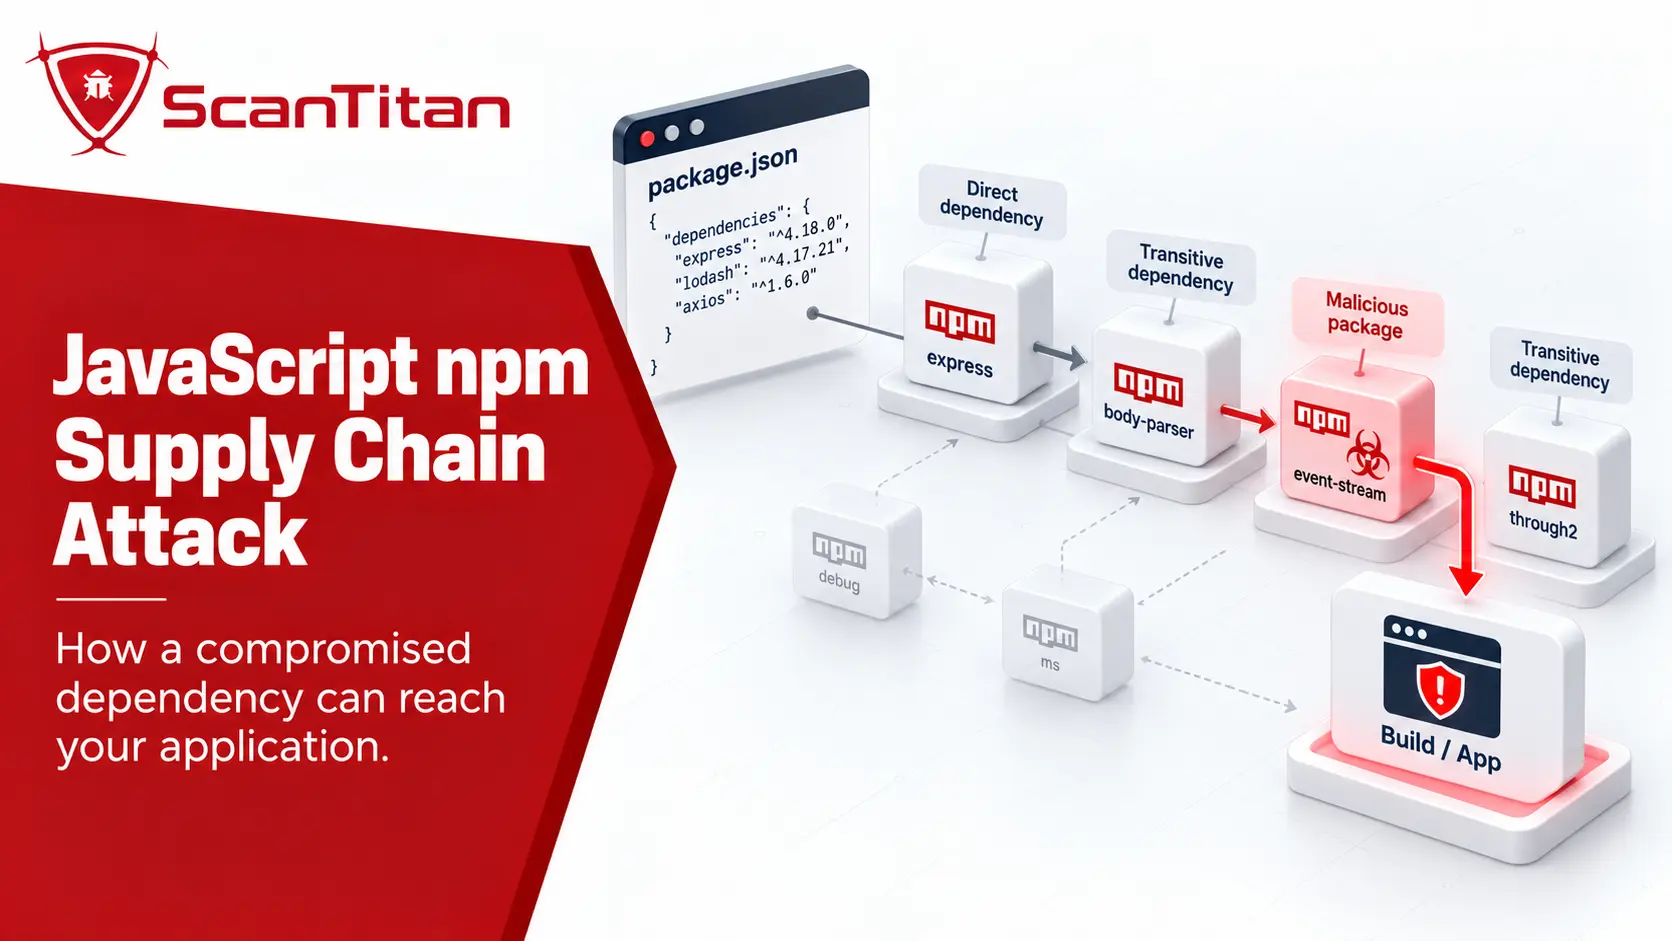
A JavaScript npm supply chain attack targets the software and infrastructure between an npm package maintainer and the application that eventually installs that package. Instead of exploiting a flaw in your own JavaScript first, an attacker may compromise a trusted package, publish a lookalike dependency, abuse package resolution, steal publishing credentials, or execute malicious code […]
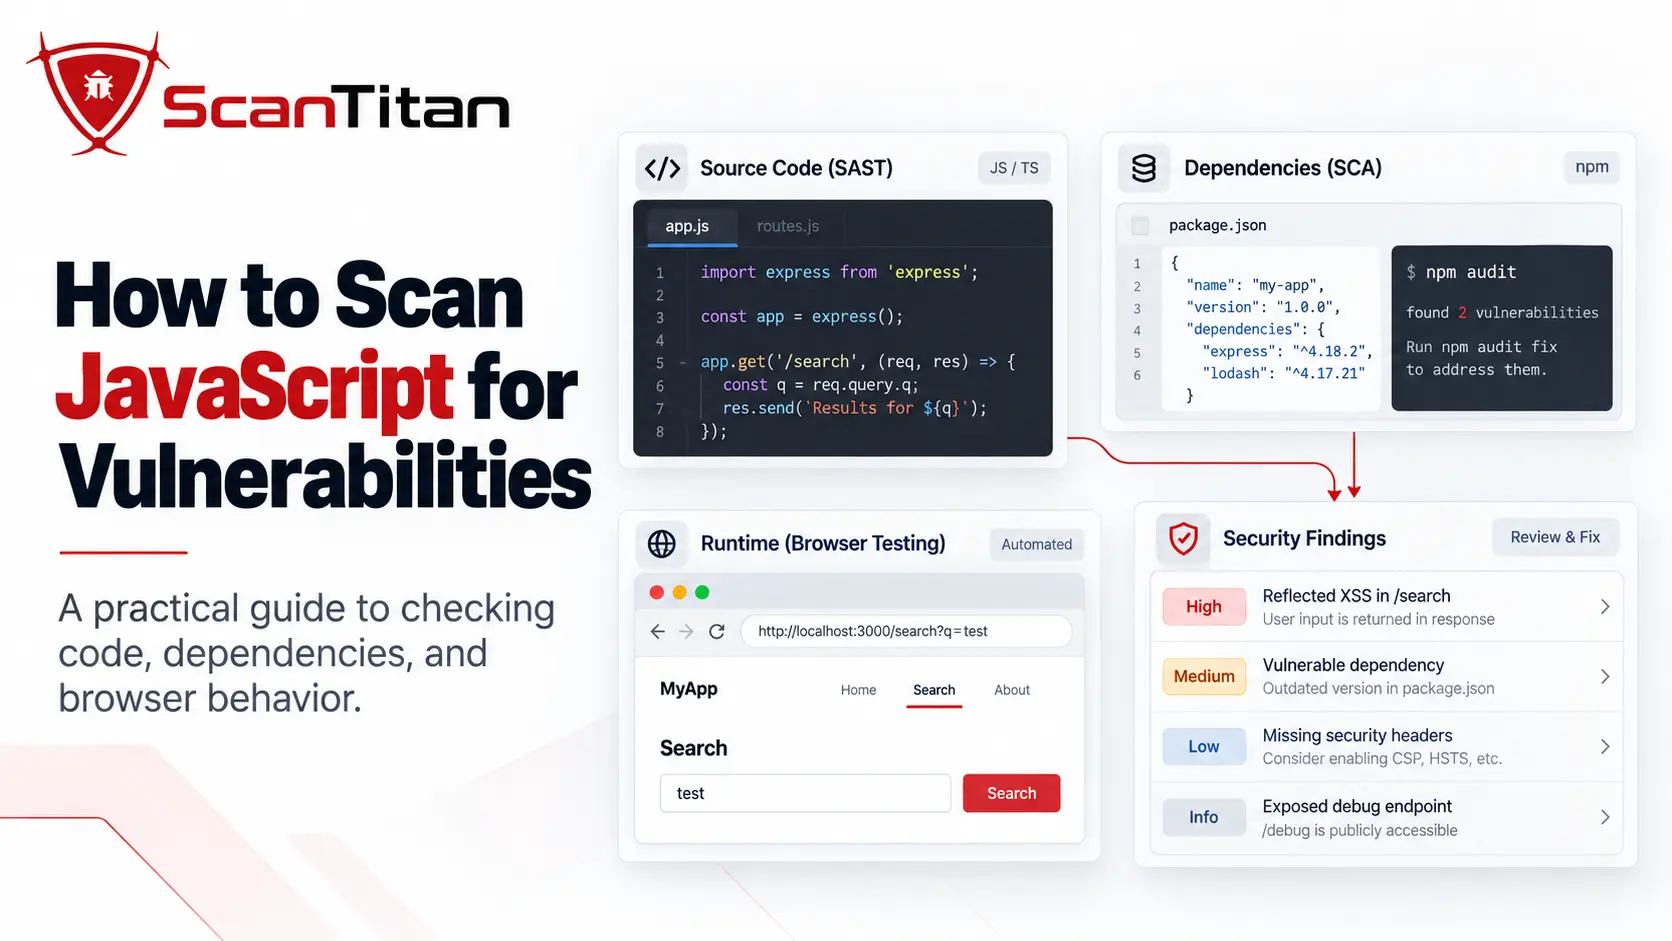
If you want to know how to scan JavaScript for vulnerabilities, do not rely on a single security check. A modern JavaScript application can contain weaknesses in the code your team writes, known vulnerabilities in npm dependencies, and security issues that appear only after the application runs in a browser. A useful JavaScript security assessment […]
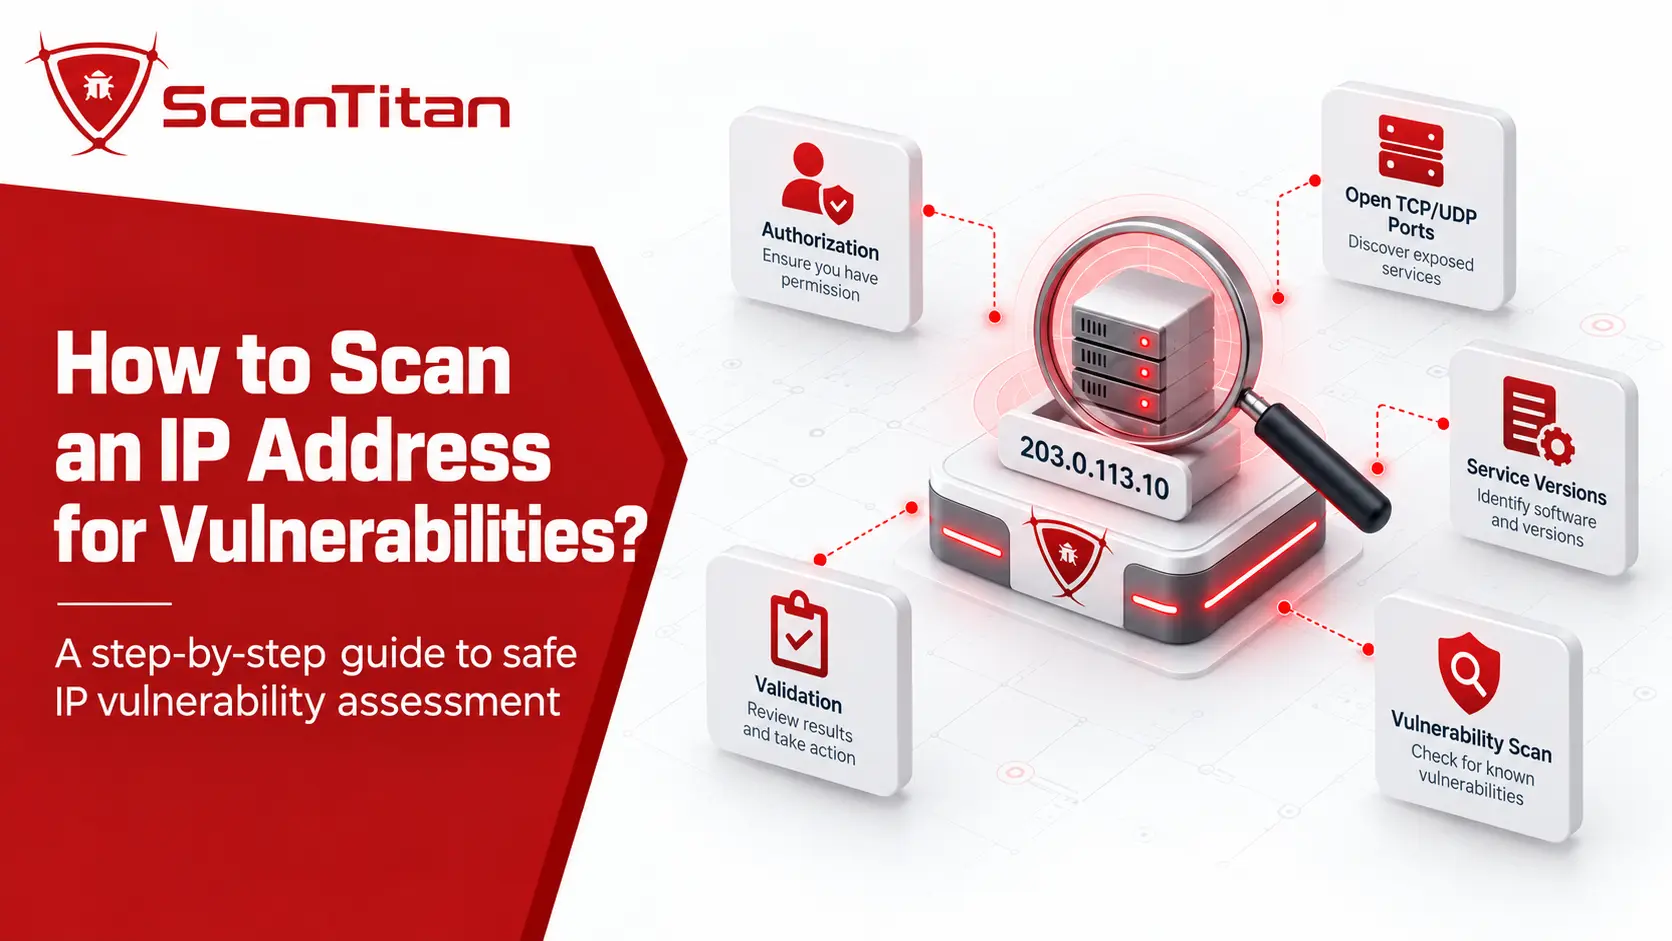
If you want to know how to scan an IP address for vulnerabilities, the process goes beyond checking whether a few ports are open. A proper assessment verifies the correct and authorized target, identifies reachable TCP and relevant UDP services, fingerprints the software behind them, runs vulnerability-specific checks, validates important findings, prioritizes confirmed weaknesses, applies […]
An IP vulnerability scan checks a specific IP address for security weaknesses that can be detected from the scanner’s location. It identifies reachable ports and services, gathers evidence about the software or configuration behind them, and checks that evidence for known vulnerabilities and security issues. This matters because internet-facing services remain an important route into […]
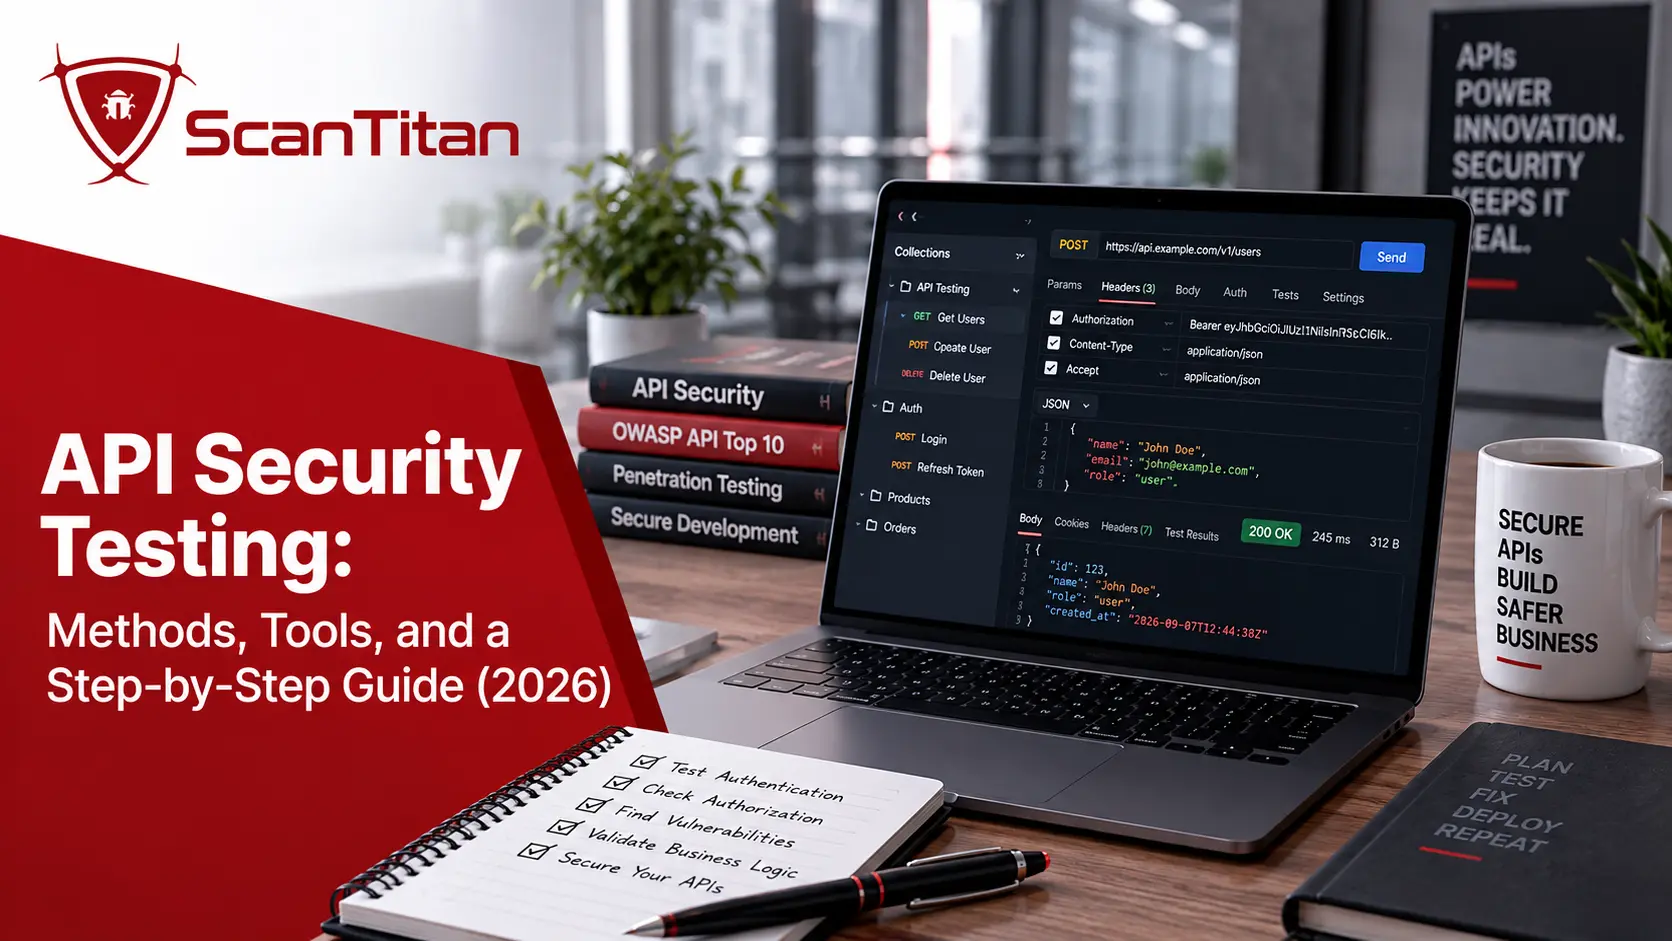
API security testing is the process of checking application programming interfaces for vulnerabilities, misconfigurations, authorization failures, unsafe input handling, and business-logic weaknesses before attackers can exploit them. Effective testing combines code analysis, dynamic scanning, fuzzing, specification-based testing, and human review across development and production. This guide explains what to test, which methods and tools to […]
By Obaida Al-Sulaiman, Information Security Manager (CISSP, GXPN, GWAPT). Reviewed September 2026. REST API security is the set of methods and controls that protect RESTful APIs from unauthorized access, data theft, and abuse. It spans authentication, authorization, encryption, rate limiting, inventory, and continuous testing. In Salt Security’s Q1 2025 survey, 99 percent of respondents said […]
API fuzzing is an automated security testing technique that floods your API endpoints with malformed, random, and unexpected inputs to find the bugs and vulnerabilities that normal testing never triggers. Instead of checking whether an endpoint returns the right answer for valid data, an API fuzzer asks what breaks when the data is wrong. This […]
An open ports security risk assessment is the process of finding every internet-facing port, identifying the service behind it, and scoring how likely an attacker is to exploit it. Not every open port is dangerous. Port 443 running patched HTTPS is fine. Port 3389 exposing Remote Desktop Protocol to the whole internet is not. This […]
The port 445 vulnerability is the security risk of exposing Server Message Block (SMB) traffic, which runs over TCP port 445, to an untrusted network. Attackers target port 445 for wormable remote code execution, ransomware, and lateral movement, and it drove the 2017 WannaCry outbreak through the EternalBlue exploit. This guide covers the key CVEs, […]
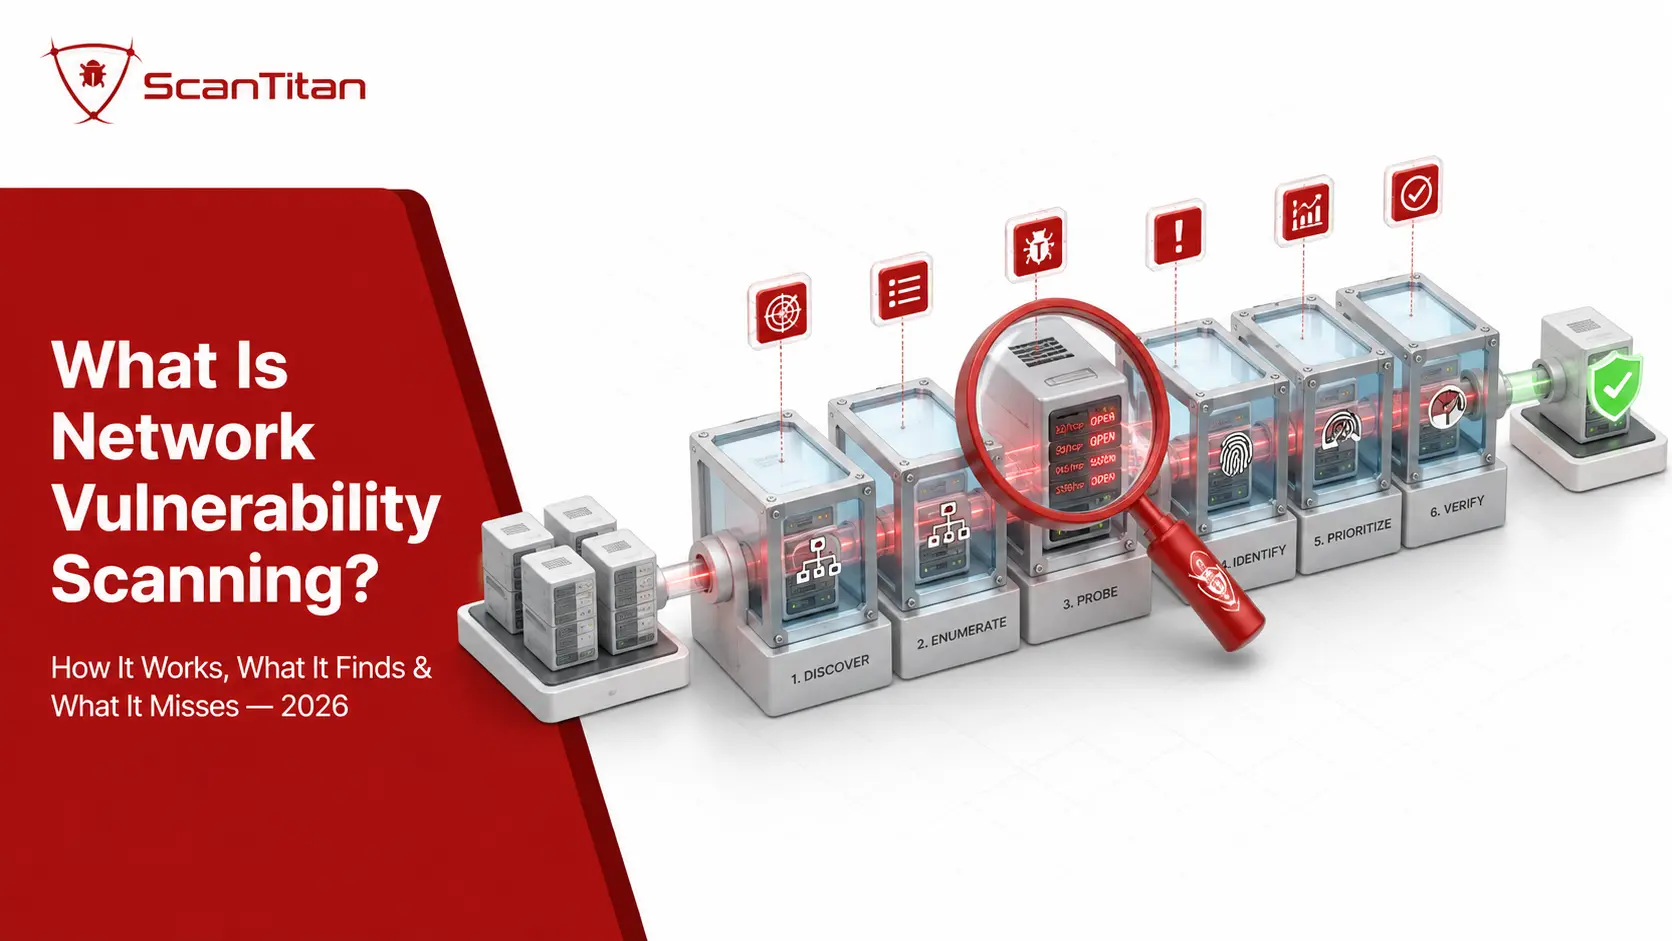
Network vulnerability scanning is the automated process of probing every host on a network, identifying the service behind each open port, and matching what it finds against a database of known vulnerabilities. It is the cheapest reliable way to see your infrastructure the way an attacker sees it. It is also widely oversold. A scan […]
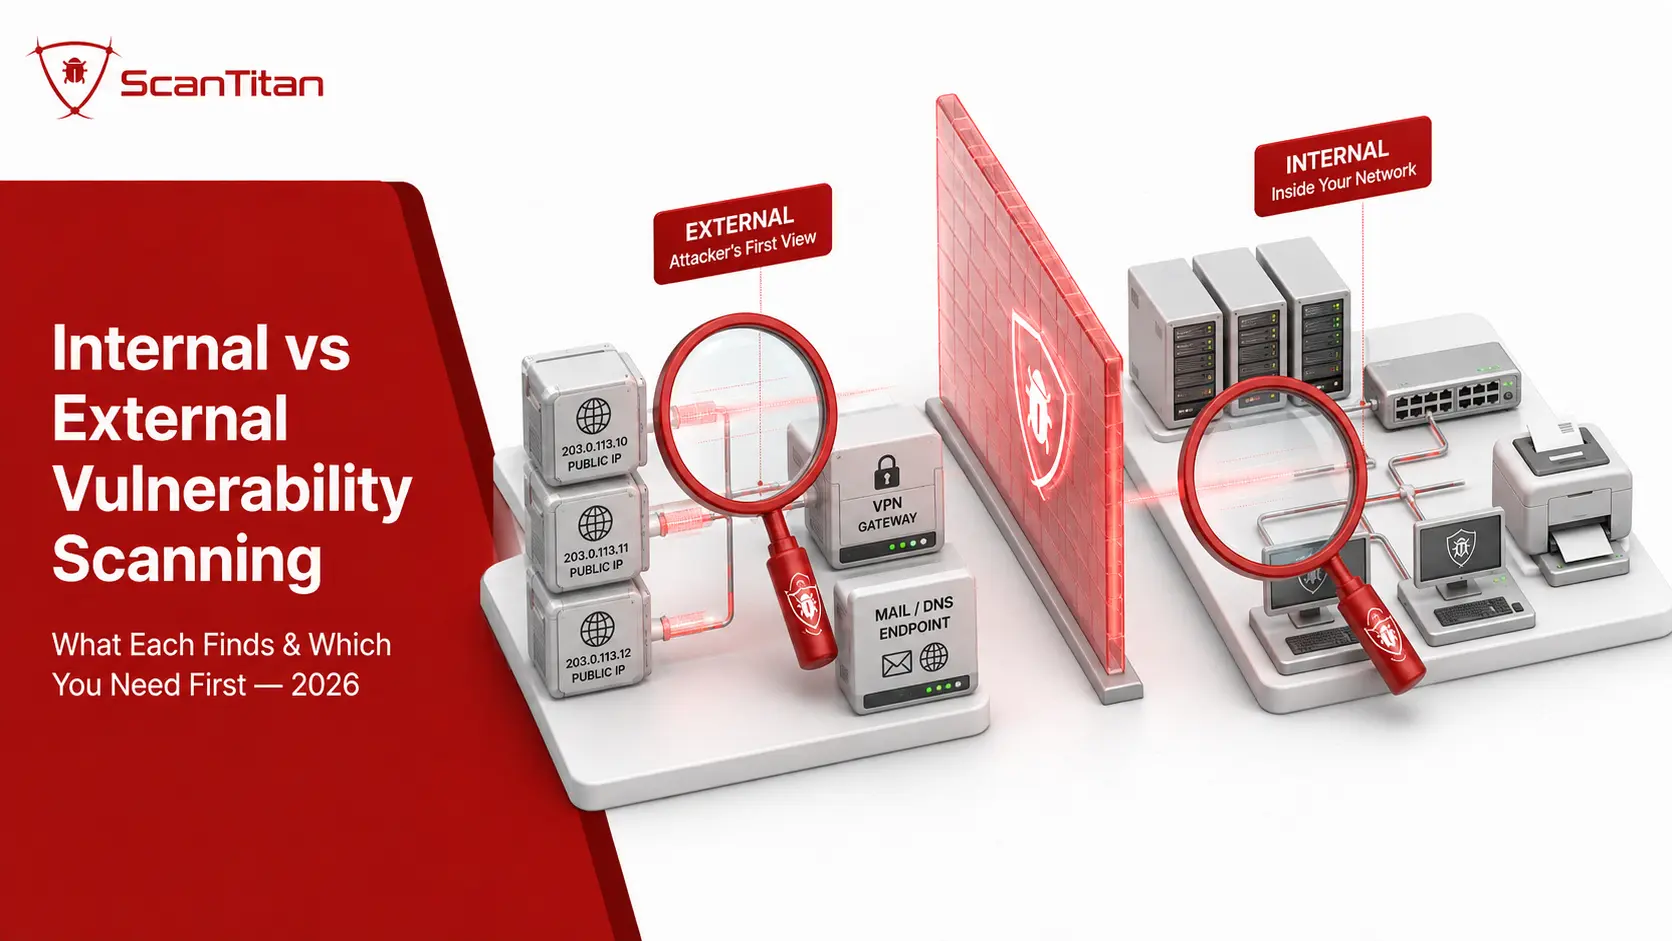
Internal vs external vulnerability scanning is primarily a difference in vantage point. An external scan tests internet-facing systems from outside your network, while an internal scan tests systems reachable from inside it. External scanning answers “what can an attacker reach before gaining access?” Internal scanning answers “what weaknesses become reachable after someone is inside?” Most […]
If your WordPress site has been hacked, the fastest way to fix it is to work in order rather than panic: contain the site, find and remove the malware, close the vulnerability that let the attacker in, then harden against a repeat. This guide walks through how to fix a hacked WordPress site step by […]
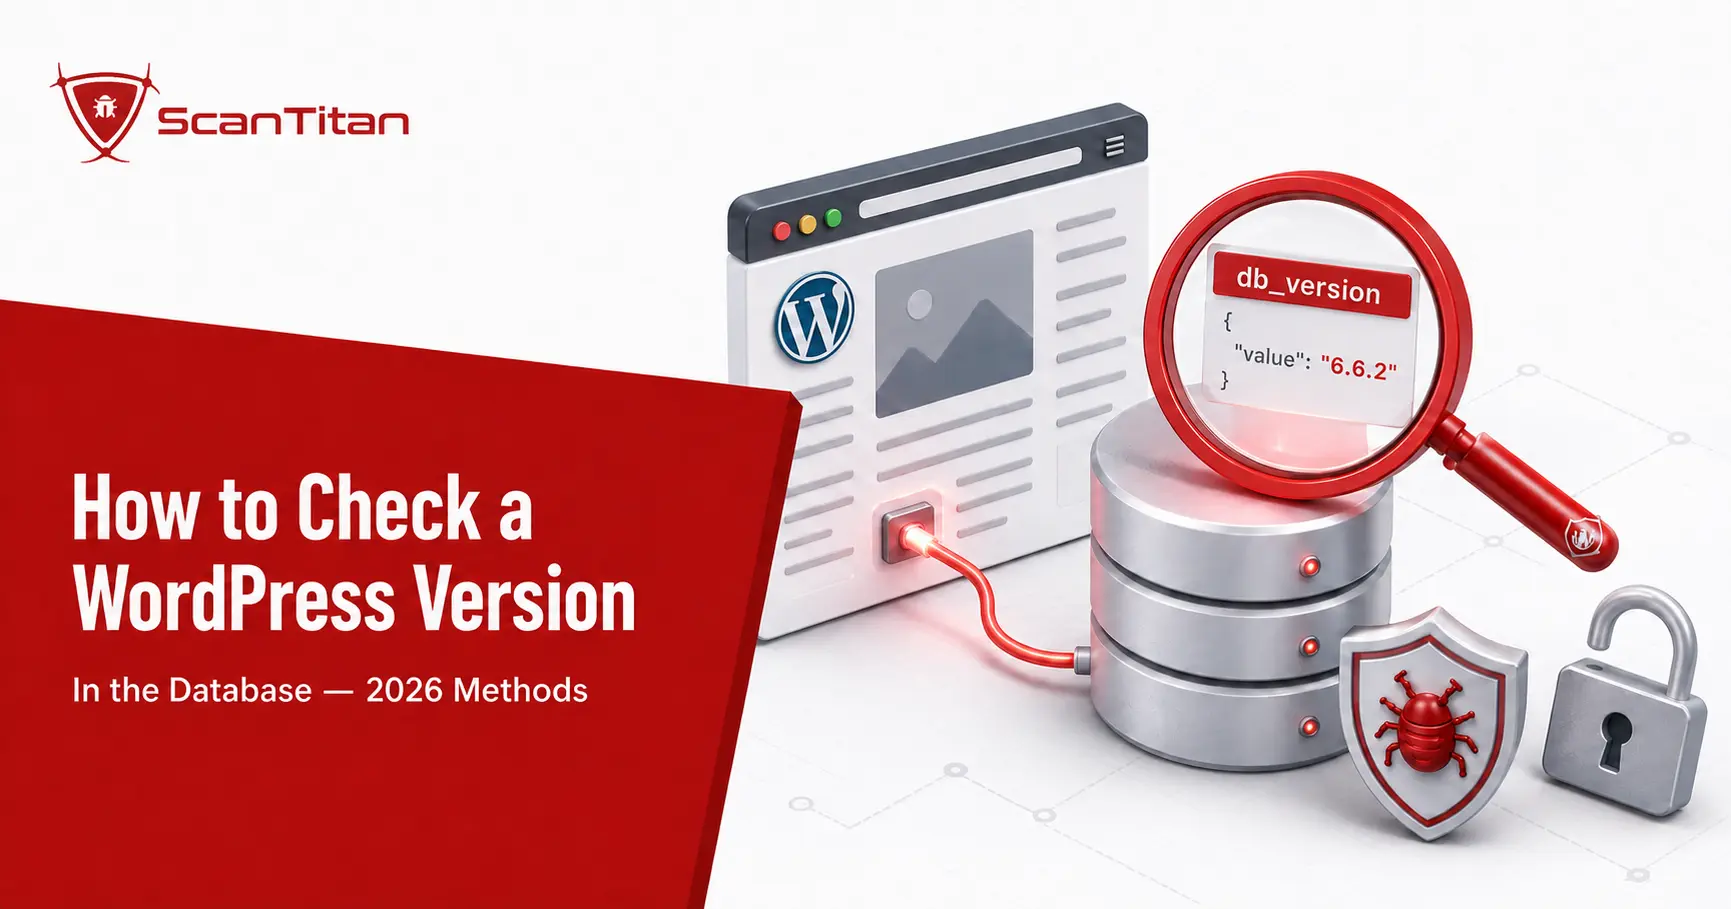
Learning how to check a wordpress version in database is useful when you are locked out of the dashboard, but it comes with a catch most guides get wrong: the version is not stored as a plain row. What the database holds is the db_version schema number and a cached core-update record whose version_checked field […]
Learning how to check WordPress version without login often takes only a couple of minutes because default or lightly hardened WordPress sites may expose version clues in the page source, RSS feeds, asset URLs, and public files. Knowing the version can help with security auditing because automated tools use the same public clues for reconnaissance. […]
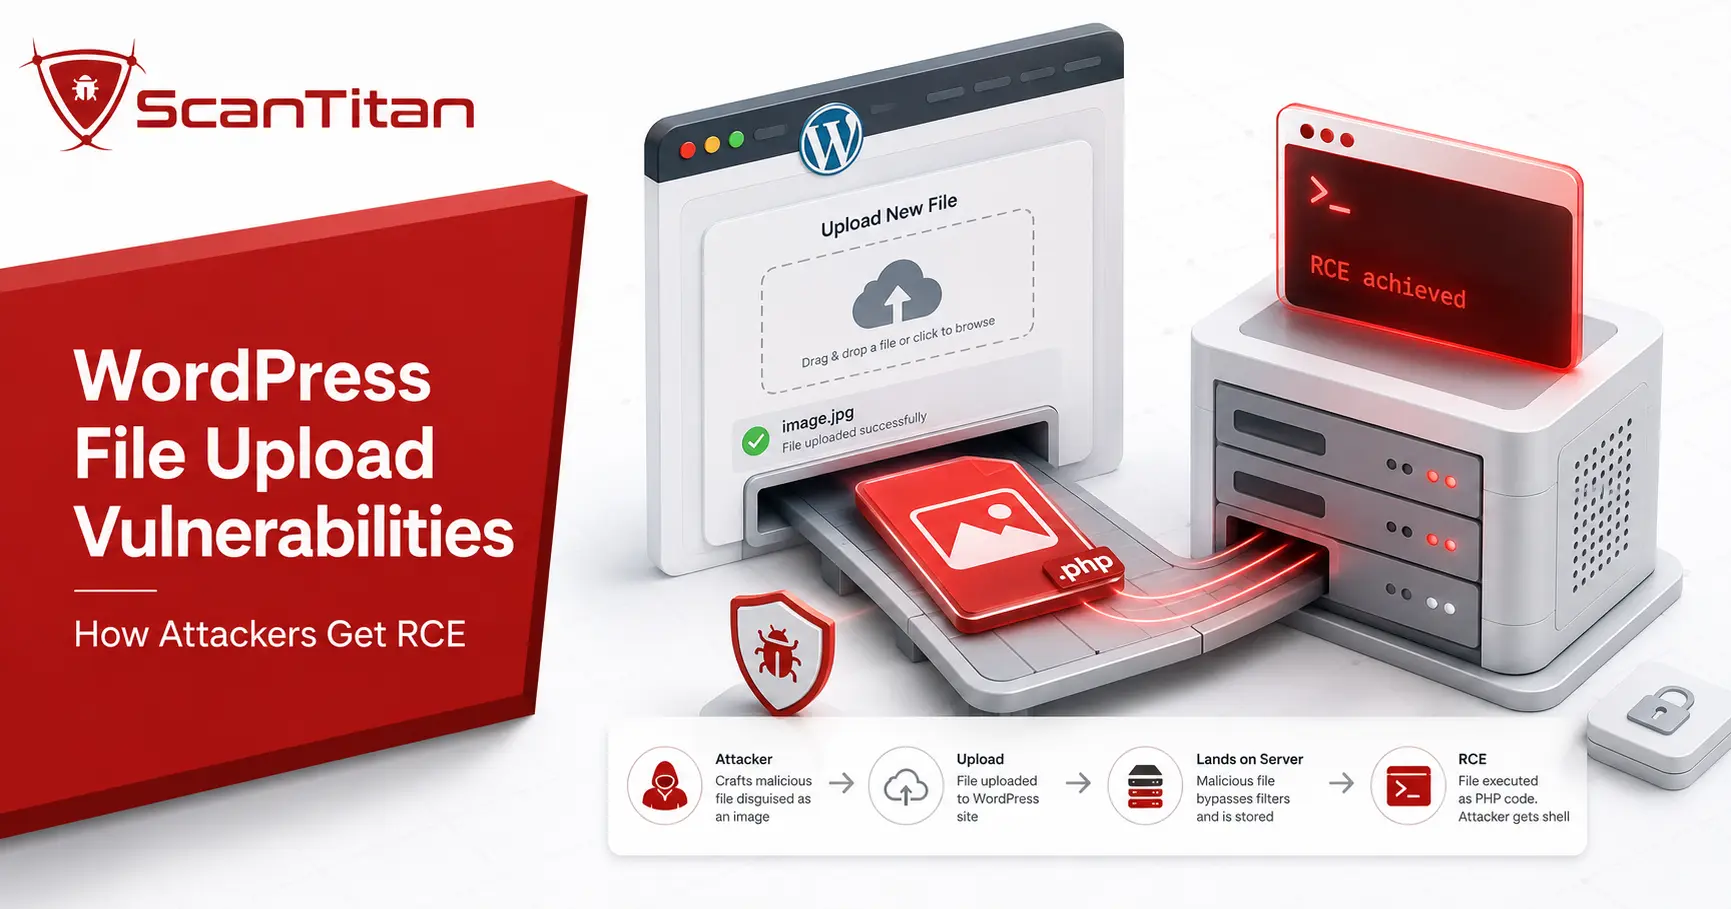
A WordPress file upload vulnerability is one of the most dangerous flaws a site can have, because it can lead straight to remote code execution when an attacker can place an executable file in a web-accessible location where the server will run it. These flaws live almost entirely in plugins and themes that accept uploads […]
WordPress SQL injection is one of the most damaging ways a WordPress site gets breached, because it reaches the database where everything lives: your users, passwords, settings, and content. The WordPress core is well protected against it, and most real cases trace back to insecure plugin or theme code rather than WordPress itself. This guide […]
WordPress plugin vulnerabilities are the single biggest reason WordPress sites get hacked, and the problem is growing, not shrinking. Plugins account for more than nine in ten WordPress security flaws, the core almost none, and some heavily exploited newly disclosed plugin bugs are now mass-exploited within hours. This guide covers what plugin vulnerabilities are, the […]
Learning how to secure Joomla website comes down to a short list of controls applied in the right order, not a hundred obscure tweaks. Patch first, lock down the login, apply least privilege, force HTTPS, harden the server, cut your extension count, and scan on a schedule. Most hacked Joomla sites fall to one skipped […]
The Joomla vs WordPress security debate usually gets answered with loyalty, not evidence. The honest version is duller and more useful: both platforms ship a secure core, and both get breached through third-party code far more than through a core bug. Joomla bundles more security controls by default, while WordPress patches its core faster and […]