A seo spam hack is an attack that injects spam pages, links or redirects into your site so the attacker can rank pharmacy, casino or counterfeit-goods pages on your domain. It often stays invisible to you and the visitors you check with, while Google shows it to searchers. This guide explains how to confirm it, where the spam hides, how to remove it and clean up Google’s index, and how to stop it coming back.
site:yourdomain.com in Google and look for pages you never wrote. If you find them, back up the site, find the code that creates the pages, remove it, patch the way in, then serve a 404 or 410 for the spam URLs and clean the sitemap so Google drops them.What an SEO Spam Hack Is
SEO spam is content an attacker plants on a site they do not own so that search engines credit the site’s authority to the attacker’s goals. The three goals are to rank the attacker’s own pages on your domain, to build links that pass your trust to their sites, and to sell products straight from your URLs. Common variants include the pharma hack, the Japanese keyword hack, cloaked spam shown only to Googlebot, and doorway pages generated by the thousand. The attack does not usually break your site. It quietly borrows it, which is why owners learn about it from a customer, a hosting warning or a drop in traffic.
| Variant | What you see | Where it shows |
|---|---|---|
| Pharma hack | Drug names and links added to pages and search snippets | Mostly in Google, often cloaked |
| Japanese keyword hack | Thousands of auto-generated Japanese product pages | Indexed pages and search results |
| Cloaked keywords and links | Hidden spam text and links inside real pages | Only to Googlebot or search visitors |
| Gibberish or doorway pages | Auto-generated pages of nonsense text that redirect to a seller | Search results, then a redirect on click |
Signs of an SEO Spam Hack
These signs show up in Google and Search Console before they show up on your own pages.
- Search for
site:yourdomain.comand look for pages, titles or foreign text you never created. - Notice search results that show your domain with pharmacy, casino or counterfeit product titles.
- Watch Search Console for a security issue warning, a manual action or a sudden jump in indexed pages.
- Spot a traffic drop, or queries in the performance report that have nothing to do with your business.
- Check for browser, hosting or blocklist warnings on the domain.
Where an SEO Spam Hack Shows: Google, Your Site, Search Console and the Sitemap
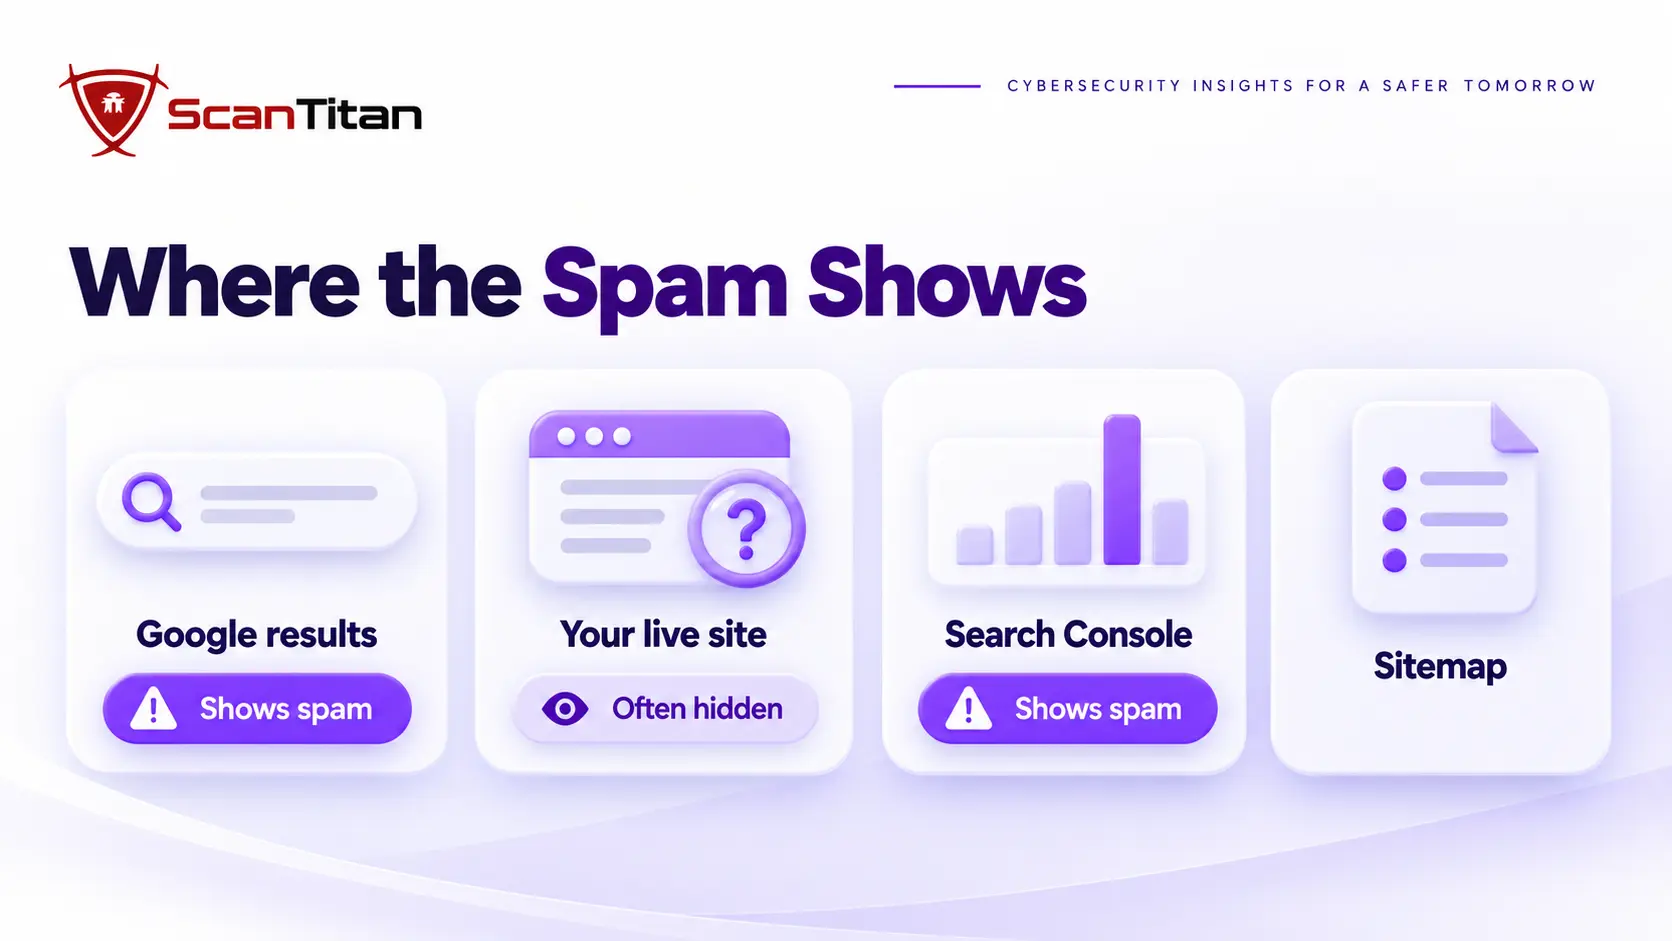
Looking at your own site is the least reliable test, because most of this spam is cloaked. Cloaking means the server shows one page to normal visitors and another to Googlebot or to people who arrive from a search result. Google’s spam policies note that it is not uncommon for a hacker to use cloaking to make the hack harder for the site owner to detect. The table shows what each place can and cannot tell you, so you know where to look first.
| Where you look | Does the spam show? | What it tells you |
|---|---|---|
| Google search results | Yes, usually first | Which spam URLs are indexed and what titles they carry |
| Your live site, as you | Often no | Little, because the code may hide from logged-in users and direct visits |
| Your live site, via a Google referrer | Sometimes | Whether a redirect or injected page appears only for search visitors |
| Search Console | Yes | Indexed pages, the queries you rank for and any security or manual action |
| Sitemap files | Sometimes | Fake sitemaps listing spam URLs that attackers submit for you |
How an SEO Spam Hack Gets In
The spam is the payload. The way in is one of four things, and finding which one you have decides whether the cleanup lasts.
Vulnerable Plugins and Themes
An outdated plugin or theme is the most common entry point, because attackers scan the internet for known flaws and exploit them automatically. A flaw that allows file upload or database writes is enough to plant spam pages without ever logging in. Deactivated plugins count too, since their files can often be requested directly. Check each plugin and theme against its current version, remove anything abandoned, and read the update notes for security fixes. The access log’s first malicious request usually names the exact component, and a plugin with a recent security fix is the first one to update.
Stolen or Weak Credentials
If an attacker has your WordPress admin, hosting panel, SFTP or database password, they can add spam files or rows directly and no vulnerability is needed. Passwords leak through reused logins, infected computers and phishing, so the compromise can predate the spam by weeks. After any hack, rotate every credential: hosting, SFTP, database, WordPress administrators and the salts in wp-config.php. Turn on two-factor authentication for administrators, and review the user list for accounts you do not recognize. A changed password closes the door they used, but only a patch closes the flaw behind it.
Nulled Themes and Plugins
Pirated copies of paid themes and plugins often ship with a backdoor or a hidden SEO spam module, installed by you with the attacker’s blessing. The code runs with full permissions and survives every cleanup that leaves the nulled copy in place. If you cannot trace a theme or plugin to its official vendor, treat it as hostile, replace it with a licensed or free official copy, and then search the files and database for what it left behind. Do not rely on the license checker the nulled copy ships with, because the same author wrote it.
Injected Database Rows
Some spam never touches a file. Attackers insert posts, links and options directly into the database, and the theme prints them. A file scan then comes back clean while Google keeps indexing the spam. Our guide on database malware in WordPress shows the SQL and WP-CLI checks for posts, options and users. Combine those with the file checks below, because cleaning one side leaves the other active. Spam rows are often inserted in bulk, so look for many similar posts created on the same date. Sort the posts table by date and by author, because one account or one minute usually accounts for the whole batch.
Where SEO Spam Hides in WordPress Files and Code
These are the places I check first. Each one can hold the code that creates or serves the spam pages.
- Inspect
.htaccessfor rewrite rules that send unknown URLs or search visitors to a script or another domain. - Search theme files, especially
functions.phpandheader.php, for obfuscated code and calls to external domains. - Look for PHP files in the uploads folder and for files with plausible core names in odd folders.
- Check the site root for extra sitemap files, spam HTML pages and verification files that you did not create.
- Review code that tests the user agent or referrer, which is how cloaking decides who sees the spam.
Obfuscated code is common in these files. Our article on obfuscated PHP malware shows how to read it without running it.
How to Remove an SEO Spam Hack Step by Step
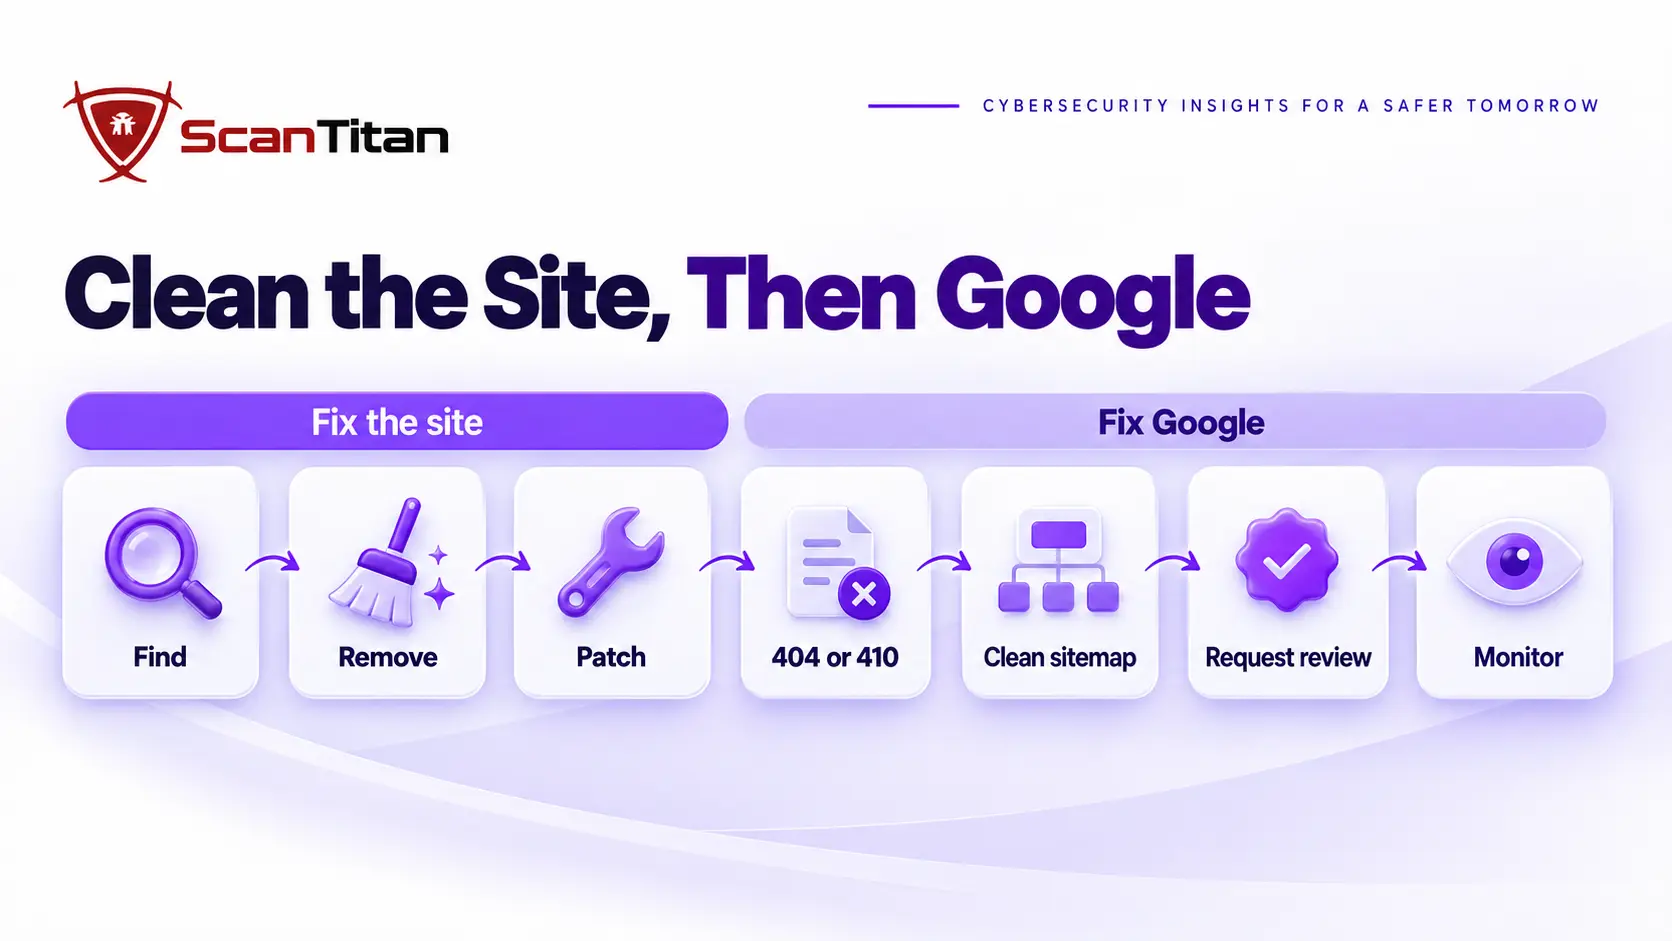
Do the steps in order. Removing spam before closing the entry point lets the attacker put it back.
- Back up the files and the database, and keep the copy as evidence before you change anything.
- Lock the site down with maintenance mode or restricted access while you work.
- List the spam URLs from
site:searches, Search Console and the access log, and note the pattern they follow. - Find the code that creates them by searching files and database rows for that pattern, the injected domains and obfuscated functions.
- Remove the infected files, rewrite rules and database rows, and delete fake sitemaps and spam pages.
- Patch the entry point, then rotate every password, key and salt.
- Rebuild WordPress core, plugins and themes from official copies, and re-scan the result.
For the full file-side process, follow our guide on how to remove malware from a website.
How to Clean Up Google After an SEO Spam Hack
Removing the code does not remove the spam URLs from Google. They stay indexed until Google recrawls them and sees they are gone. Make that signal clear: return a 404 or 410 status for every spam URL, because Google’s documentation on HTTP status codes explains how it treats them. Delete fake sitemaps and submit a clean one. For urgent cases, use the Removals tool in Search Console to hide URLs temporarily. If there is a manual action, fix the cause, then request a review from the manual actions report. Recovery takes weeks, and I would not promise a date.
How to Stop an SEO Spam Hack Coming Back
Spam that returns means a foothold survived. Treat a second appearance as a reinfection problem and work through the causes in our guide on why WordPress malware keeps coming back. Then keep the basics tight.
- Update WordPress, plugins and themes, and remove any you do not use.
- Limit administrator accounts and use two-factor authentication for every one.
- Monitor file changes so a new PHP file or edited
.htaccessraises an alert. - Repeat the
site:search and a Search Console check weekly for at least a month.
When an SEO Spam Hack Needs a Professional Cleanup
Get help when thousands of spam URLs are indexed, when the cloaking is something you cannot reproduce, when Google has applied a manual action, or when the spam returns after you clean it. These signs usually mean more than one foothold, and guessing costs you traffic every week the spam stays indexed. A professional cleanup finds the code, the entry point and the database rows together, and documents the evidence you need for a Google review. The cost of waiting is real, since spam that stays indexed keeps sending your authority to the attacker. ScanTitan’s website malware removal service covers all three.
SEO Spam Hack: Common Questions Answered
What is a seo spam hack?
It is an attack where someone injects spam pages, links or redirects into your site so their pharmacy, casino or counterfeit-goods pages rank on your domain. You often cannot see it on your own pages, because the spam is shown only to Google or to visitors who arrive from search.
How do I know if my site has an SEO spam hack?
Search site:yourdomain.com in Google and look for pages or titles you did not create. Then check Search Console for a security issue, a manual action, a jump in indexed pages or unrelated queries. A clean-looking live site does not rule it out, because cloaked spam hides from you.
Will an SEO spam hack hurt my rankings?
It can. Spam pages dilute your site, Google may apply a manual action, and visitors who land on spam leave quickly. Rankings usually recover after you remove the spam and Google recrawls, but the recovery takes weeks and depends on how long the hack ran.
How do I get spam pages out of Google?
Remove the code that creates them first, then return a 404 or 410 for each spam URL and submit a clean sitemap. Use the Removals tool in Search Console to hide urgent URLs temporarily. Google drops the rest as it recrawls, so the process is slow but reliable.
How long does recovery take after an SEO spam hack?
Expect weeks, and sometimes months for large sites with thousands of spam URLs. The cleanup itself can take a day. The wait is Google recrawling and dropping the old URLs, so submit a clean sitemap and monitor the indexed page count until it settles.
Why does the SEO spam come back after I clean it?
Because a foothold survived. A backdoor, a rogue administrator, an injected database row or the original vulnerable plugin lets the attacker reinstall it. Find the entry point, rotate every credential and check both files and database before you call the cleanup finished.
Is an SEO spam hack the same as the pharma hack or Japanese keyword hack?
Those are variants of the same attack. SEO spam is the umbrella term for injected pages, links and redirects that borrow your rankings. The pharma hack pushes drug keywords, the Japanese keyword hack pushes auto-generated Japanese product pages, and the removal and Google cleanup steps are largely the same.