Practical security insights for teams without a SOC
No vendor fluff. No recycled threat reports. Real guidance on vulnerability scanning, malware, and attack surface management — written by practitioners.
A cloaking hack in WordPress is malicious code that shows spam to Google and a normal site to you, so the dashboard and your own browser look clean while search results fill with pharmacy or casino pages. The code checks who is asking, by user agent, IP address, referrer or login state, and serves the […]
Nulled plugins malware is malicious code hidden in a pirated copy of a premium WordPress plugin, installed by an owner who wanted it for free. The code runs with the plugin’s full permissions, so it can open a backdoor, create administrators, inject spam or switch off your security plugin. This guide shows what hides inside, […]
A site still blocklisted after cleanup is rarely a mystery. The flag stays because you are still waiting for a review, part of the infection is still there, or a different list holds the flag. Blocklists do not judge how clean you feel, only what their crawler or reviewer sees. This guide shows how long […]
Malicious JavaScript on website pages is script code that an attacker planted so it runs in your visitors’ browsers. It loads from a theme file, a database row, a third-party tag or the server itself, and it redirects traffic, steals form data or shows fake prompts. This guide shows where it hides, how to find […]
WordPress mu-plugin malware is malicious PHP placed in the wp-content/mu-plugins folder, where WordPress loads it on every request without activation, so it never shows as an active plugin. Attackers use it to load remote payloads, hide accounts, steal logins and restore deleted files. This guide shows how it hides and survives, the indicators that give […]
Hidden admin user WordPress infections are administrator accounts that exist in the database but are filtered out of the Users screen by code, so the dashboard shows nothing unusual. Attackers create one to return after cleanup. This guide shows how attackers hide the account, how to find it with direct SQL when even WP-CLI is […]
The 12 signs of website malware fall into five groups: what visitors see, what Google shows, what you see in the dashboard, what the server’s files and logs show, and what your host or email provider reports. Redirects, browser warnings and spam in search results are the most common. This guide lists the 12 signs, […]
PHP2Shell is the name researchers gave to two critical PHP core flaws, CVE-2026-109618 and CVE-2026-109619, that let an unauthenticated attacker run code on a server through ordinary web requests. The PHP team shipped fixes on 21 October 2026 in versions 8.5.12, 8.4.27, 8.3.36, and 8.2.35. If your site runs PHP, which covers every WordPress, Joomla, […]
To find a backdoor in a website, run three passes: compare every file against a clean copy, search for code that behaves like a backdoor, and trace unusual requests in your access logs. Backdoors hide in eight places, from fake core files to the database, and a scanner alone misses many of them. This guide […]
How did my website get hacked? Almost always through one of nine entry points: a vulnerable plugin or theme, stolen credentials, a nulled theme, a compromised hosting account, vulnerable custom code, exposed files, an infected admin computer, a third-party script, or weak server settings. Each one leaves different evidence in your logs and files. This […]
A seo spam hack is an attack that injects spam pages, links or redirects into your site so the attacker can rank pharmacy, casino or counterfeit-goods pages on your domain. It often stays invisible to you and the visitors you check with, while Google shows it to searchers. This guide explains how to confirm it, […]
Database malware WordPress owners miss is malicious code, links or settings stored in database rows instead of files, which is why file scanners and file restores never catch it. It shows up as injected scripts, spam links, redirects, a changed site URL or an administrator you never created. This guide explains where the infection hides, […]
This guide will tell you how to monitor your website availability and uptime by using ScanTitan free online website monitor. As the world evolves today, websites become an increasingly vital tool for businesses and end-users relying on the internet for work or pleasure. With an increase in websites, there is a need for website availability […]
This guide will tell you how to scan your website against malware which includes viruses, webshells, malicious javascript and others by using ScanTitan free website malware scanner. What is website malware? Can a website be infected with malware too? Malware, is the short form for malicious software, is designed basically to cause harm to a […]
This guide will tell you how to find your website security vulnerabilities and weakness by using ScanTitan free online vulnerability scanner. What is website vulnerability? According to research, it has shown on average that websites experience a cyber attack of over 25 times per day which implies over 9,000 attacks per year. Website vulnerability simply […]
This guide will tell you how to reduce your website and online services attack surface by finding your security exposures using ScanTitan free online vulnerability scanner. What is website security exposure? With an increasing rate of cyber-attacks daily, there are various factors in which website security exposure is one that allows a website to become […]
This guide will tell you how to know your network exposure and running services on your edge device like a firewall or router and how to monitor network exposure using ScanTitan. What is network exposure monitoring? With the rate at which hackers are exploiting services behind open ports, it is very important to conduct network […]
This article will guide you on how to monitor your cyber brand security using ScanTitan cyber brand monitoring to prevent digital image issues, traffic drops, and your customer trust loss. What is cyber brand monitoring? Cyber brand monitoring is very essential in your business if you want to consistently stand out, retain customers on your […]
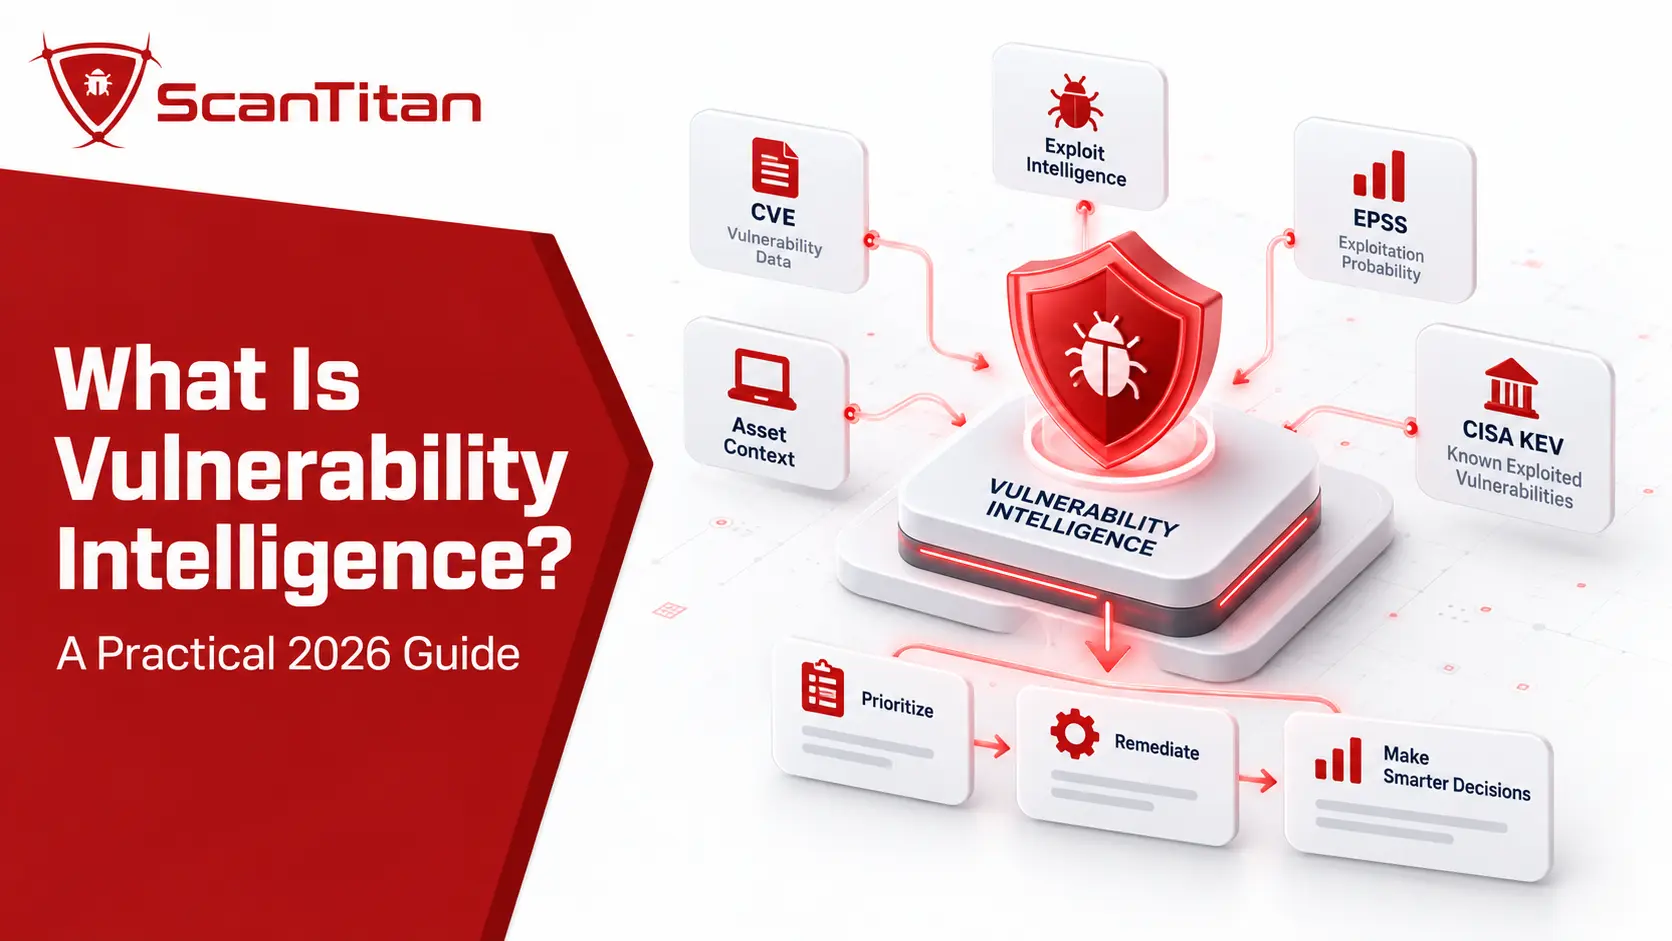
Vulnerability intelligence is the process of turning raw vulnerability data into decisions about what to fix first. It combines CVE records with exploit activity, technical severity, affected products, patch status, threat context, and your own asset exposure. That matters more in 2026 because Verizon reports vulnerability exploitation as the initial access path in 31% of […]
This guide will tell you what is cyber threat intelligence and how it is important to identify relevant threats of your business using ScanTitan Threat Intelligence platform. What is Threat Intelligence? Cyber threats keep increasing daily and it has become an essential issue for organizations and companies to deal with. Threat intelligence is simply the […]
PHP2Shell is the name researchers gave to two critical PHP core flaws, CVE-2026-109618 and CVE-2026-109619, that let an unauthenticated attacker run code on a server through ordinary web requests. The PHP team shipped fixes on 21 October 2026 in versions 8.5.12, 8.4.27, 8.3.36, and 8.2.35. If your site runs PHP, which covers every WordPress, Joomla, […]
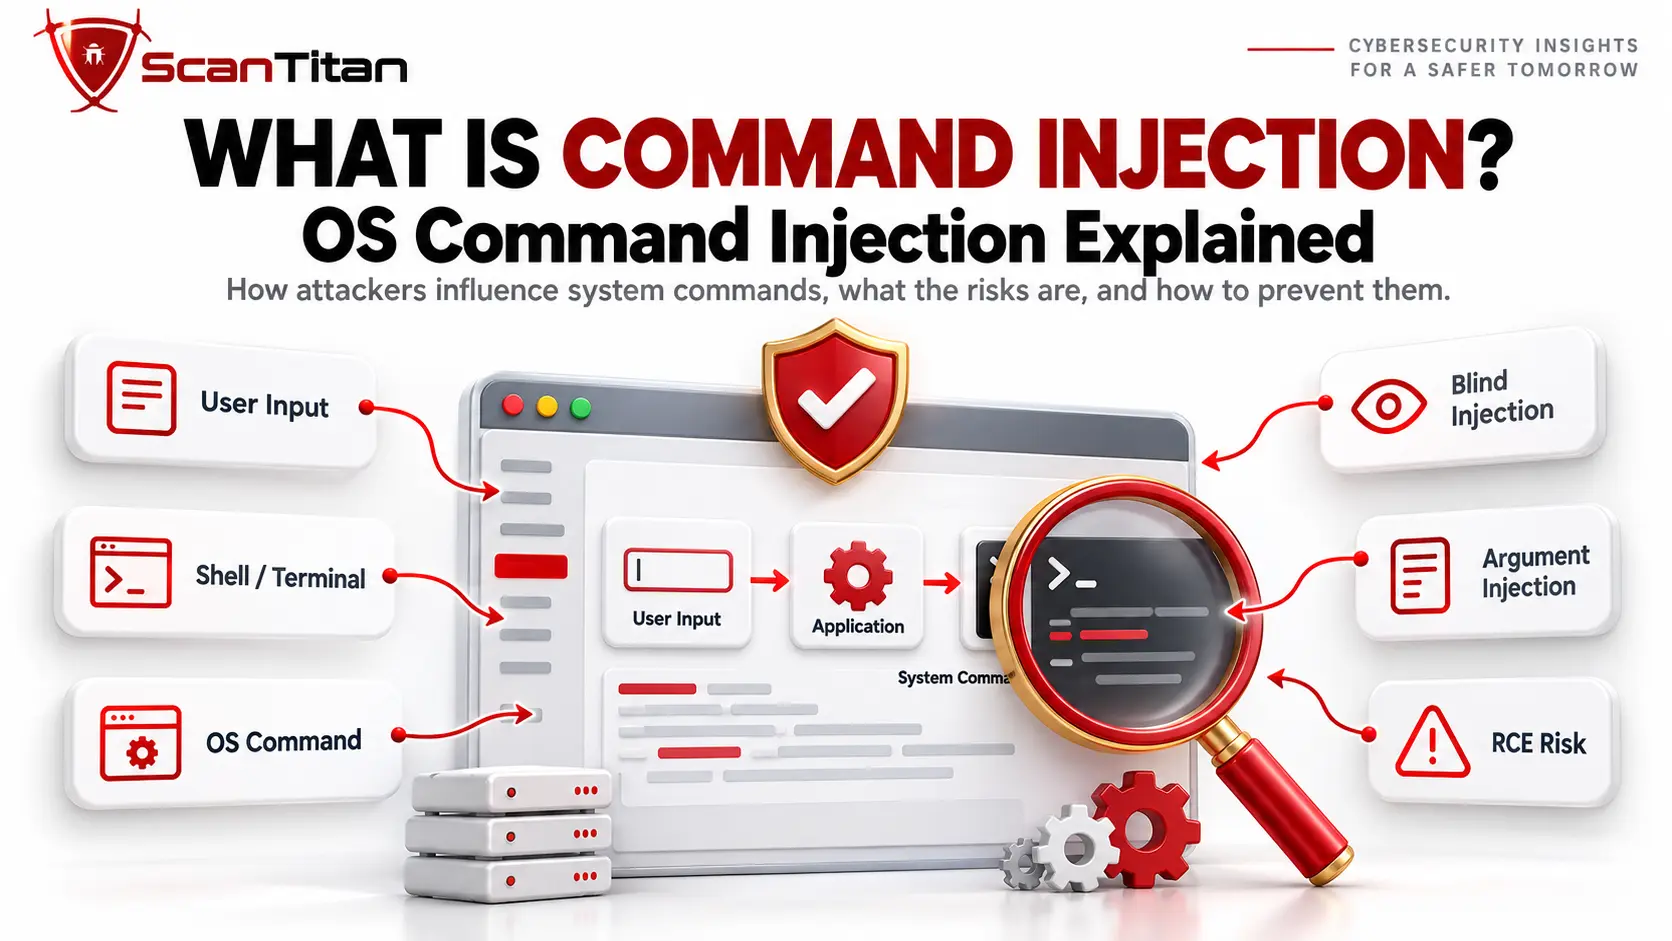
Command injection, usually referring to OS command injection, is a security vulnerability in which attacker-controlled input changes an operating-system command executed by an application, allowing unintended command behavior or additional commands to run with the application’s privileges, The core trust boundary is straightforward: the attacker influences data, the application turns that data into part of […]
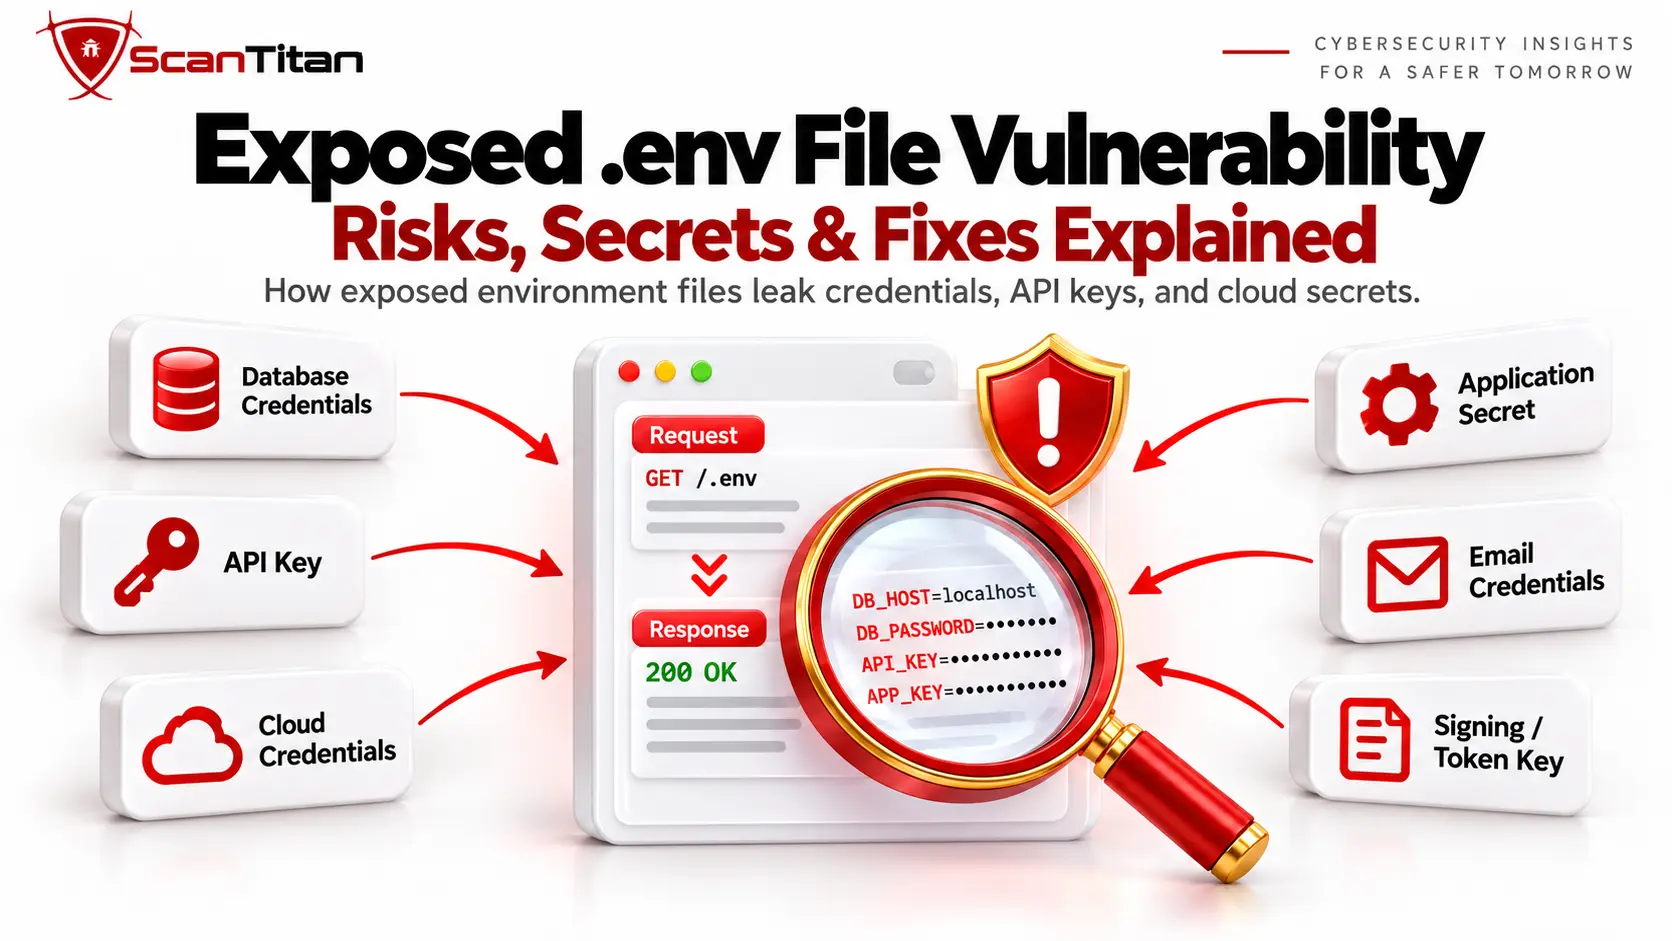
An exposed .env file vulnerability occurs when a web server allows unauthorized users to retrieve an environment configuration file. A publicly accessible .env file can reveal database credentials, API keys, application secrets, cloud credentials, mail passwords, signing keys, and other configuration values that were intended to remain server-side.The severity depends on what the file contains […]
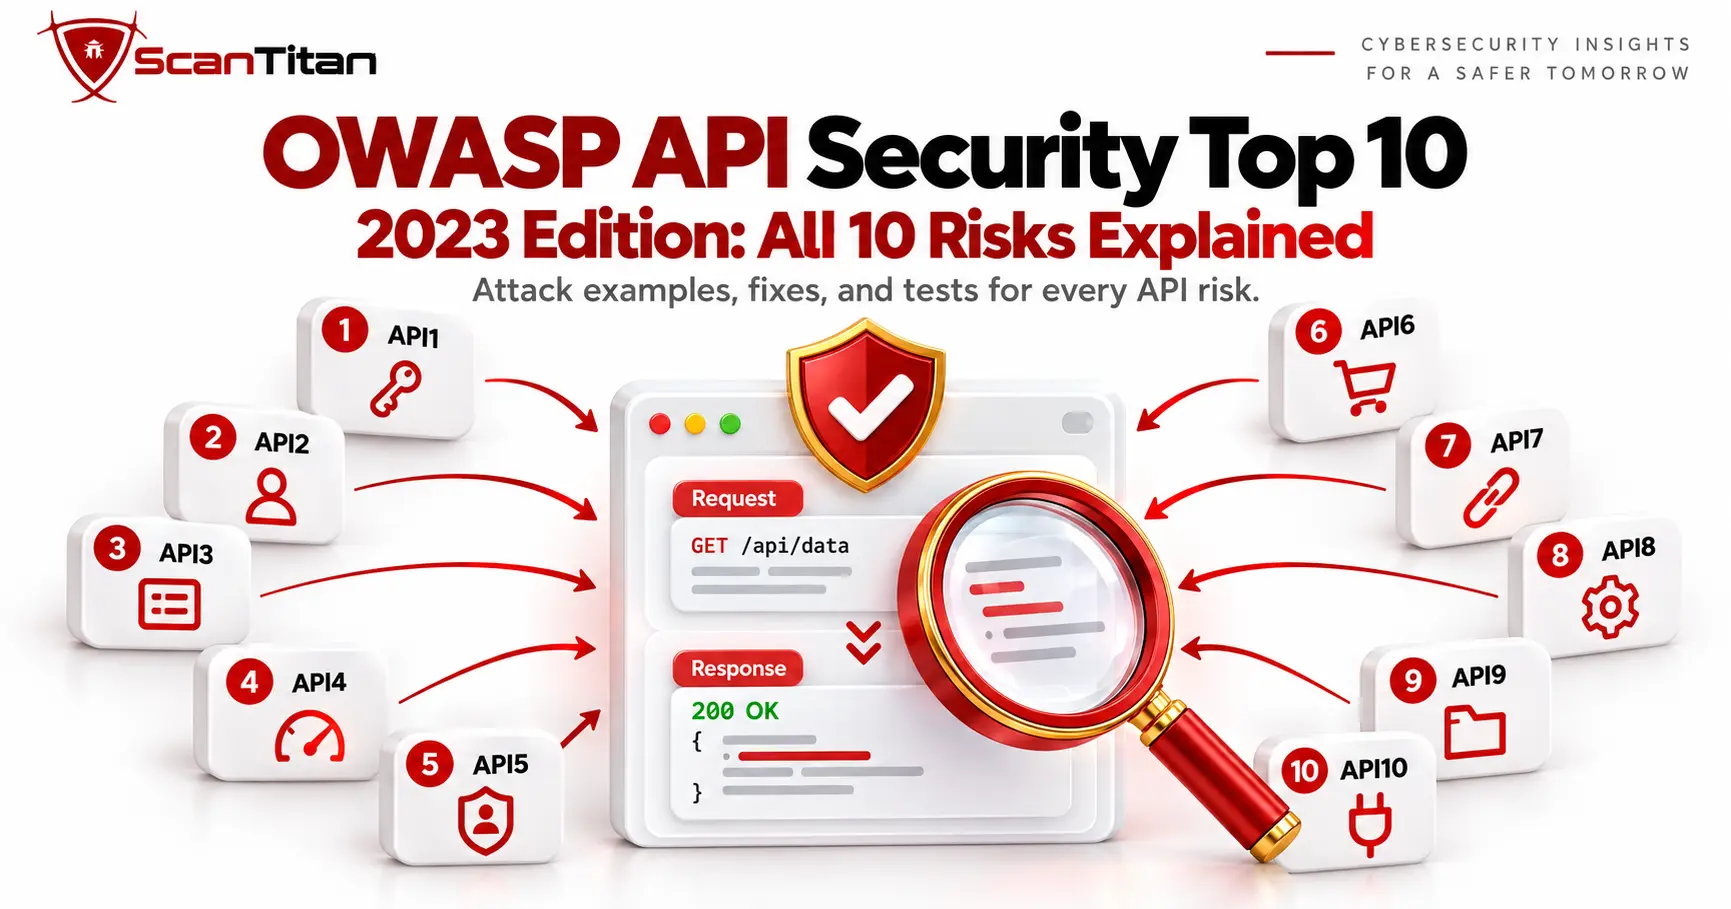
The OWASP API Top 10 is a ranked list of the ten most critical API security risks, and the 2023 edition is still the current version. It covers broken authorization, broken authentication, resource abuse, server-side request forgery, misconfiguration, and unsafe use of third-party APIs. This guide explains all ten risks with an attack example, a […]
The best vulnerability scanning tools in 2026 depend on what you need to scan. ScanTitan, Intruder, and HostedScan serve small teams that want cloud scanning without a security department, Tenable Nessus, Qualys VMDR, and Rapid7 InsightVM cover servers and networks, and Invicti, Burp Suite DAST, and Detectify test running web applications. This guide compares ten […]
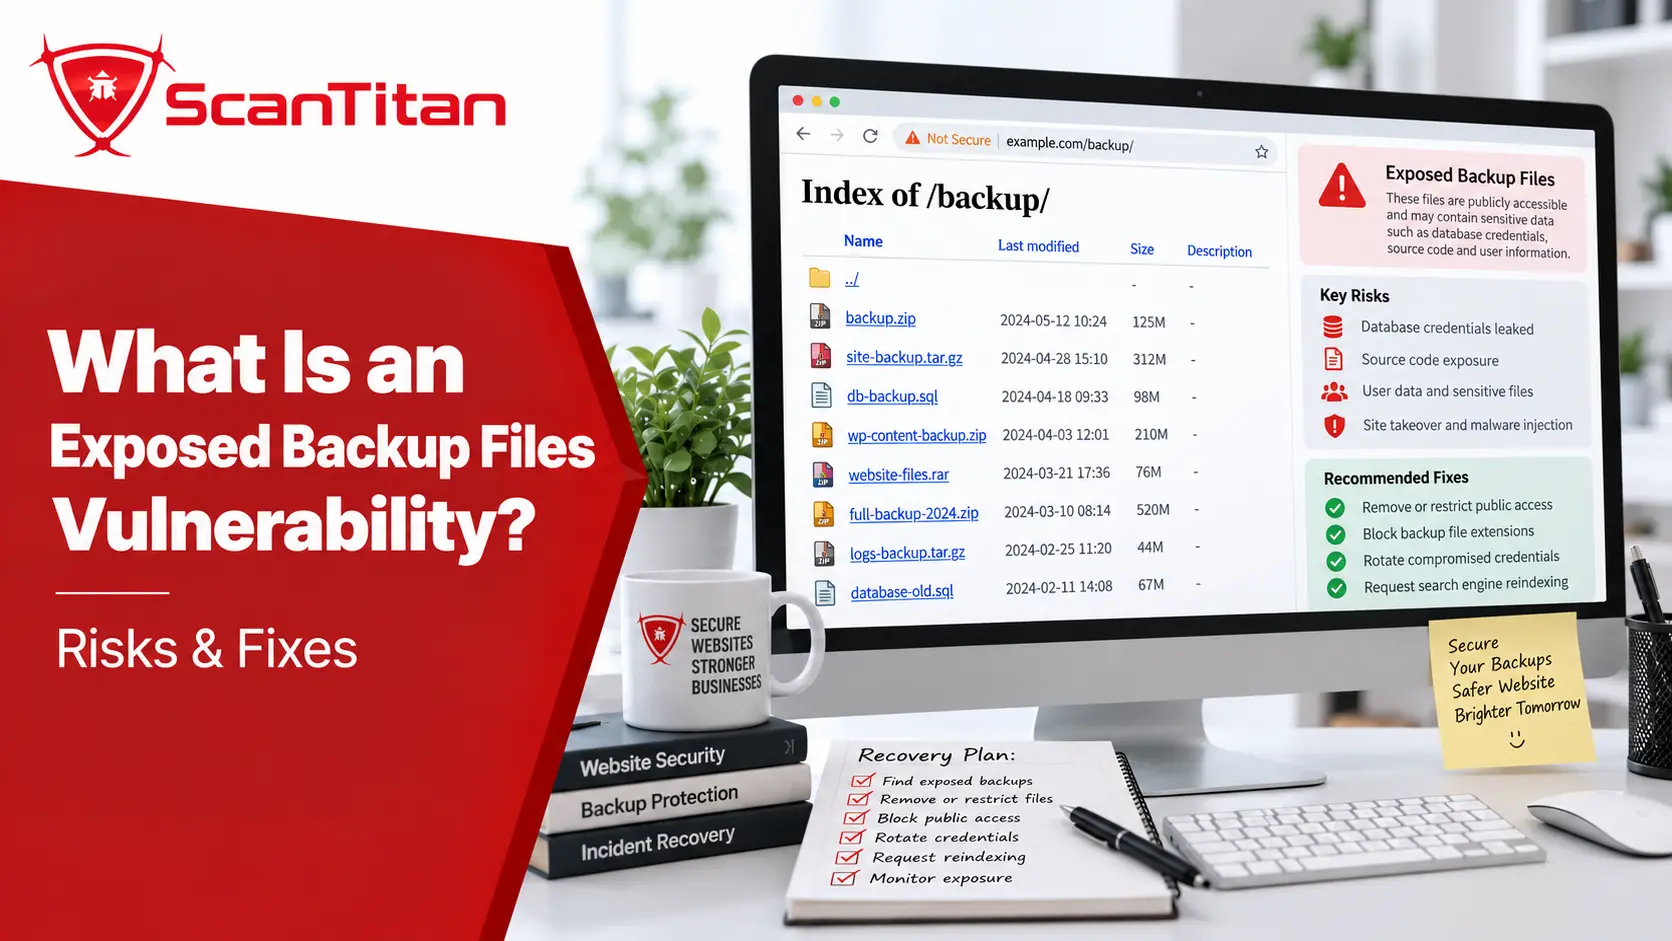
An exposed backup files vulnerability occurs when a backup, database dump, old source-code copy, deployment archive, or editor-generated file is publicly accessible from a web server. Files such as config.php.bak, database.sql, site-backup.zip, or index.php~ can reveal source code, credentials, private data, and internal application details.The impact depends on what the backup contains. An obsolete static […]
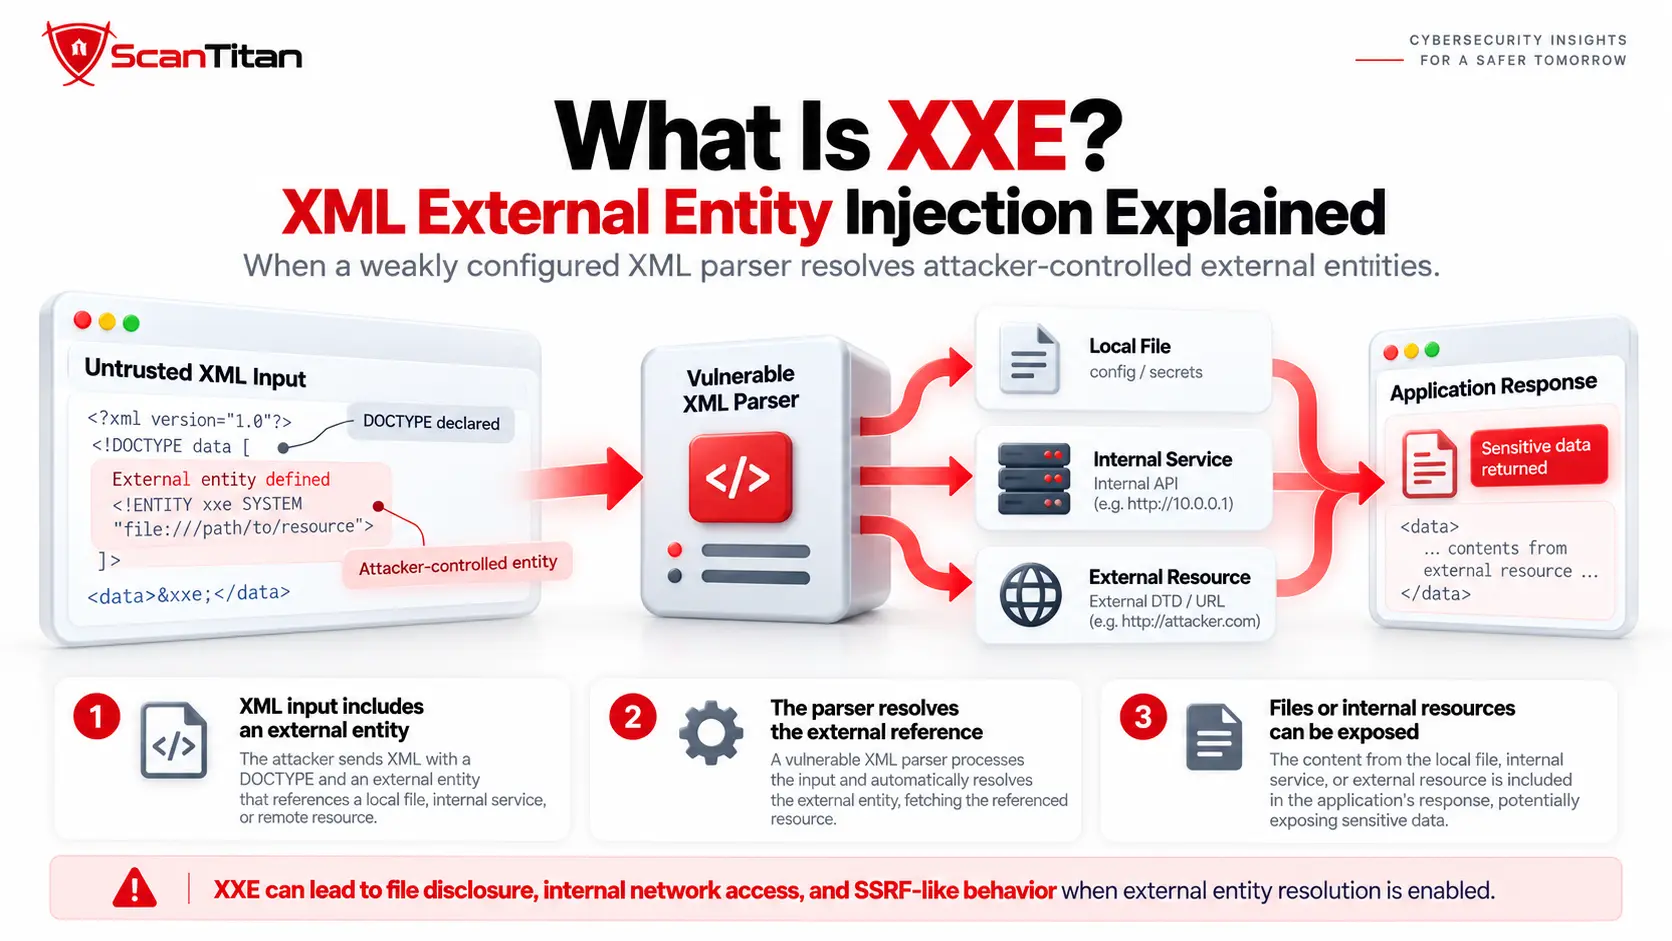
XML External Entity (XXE) Injection is a web security vulnerability in which an application processes attacker-controlled XML with a parser that is allowed to resolve external entities or other external XML resources. That unsafe parser behavior can expose local files, trigger server-side requests to internal or external systems, or create other unintended resource access. The […]
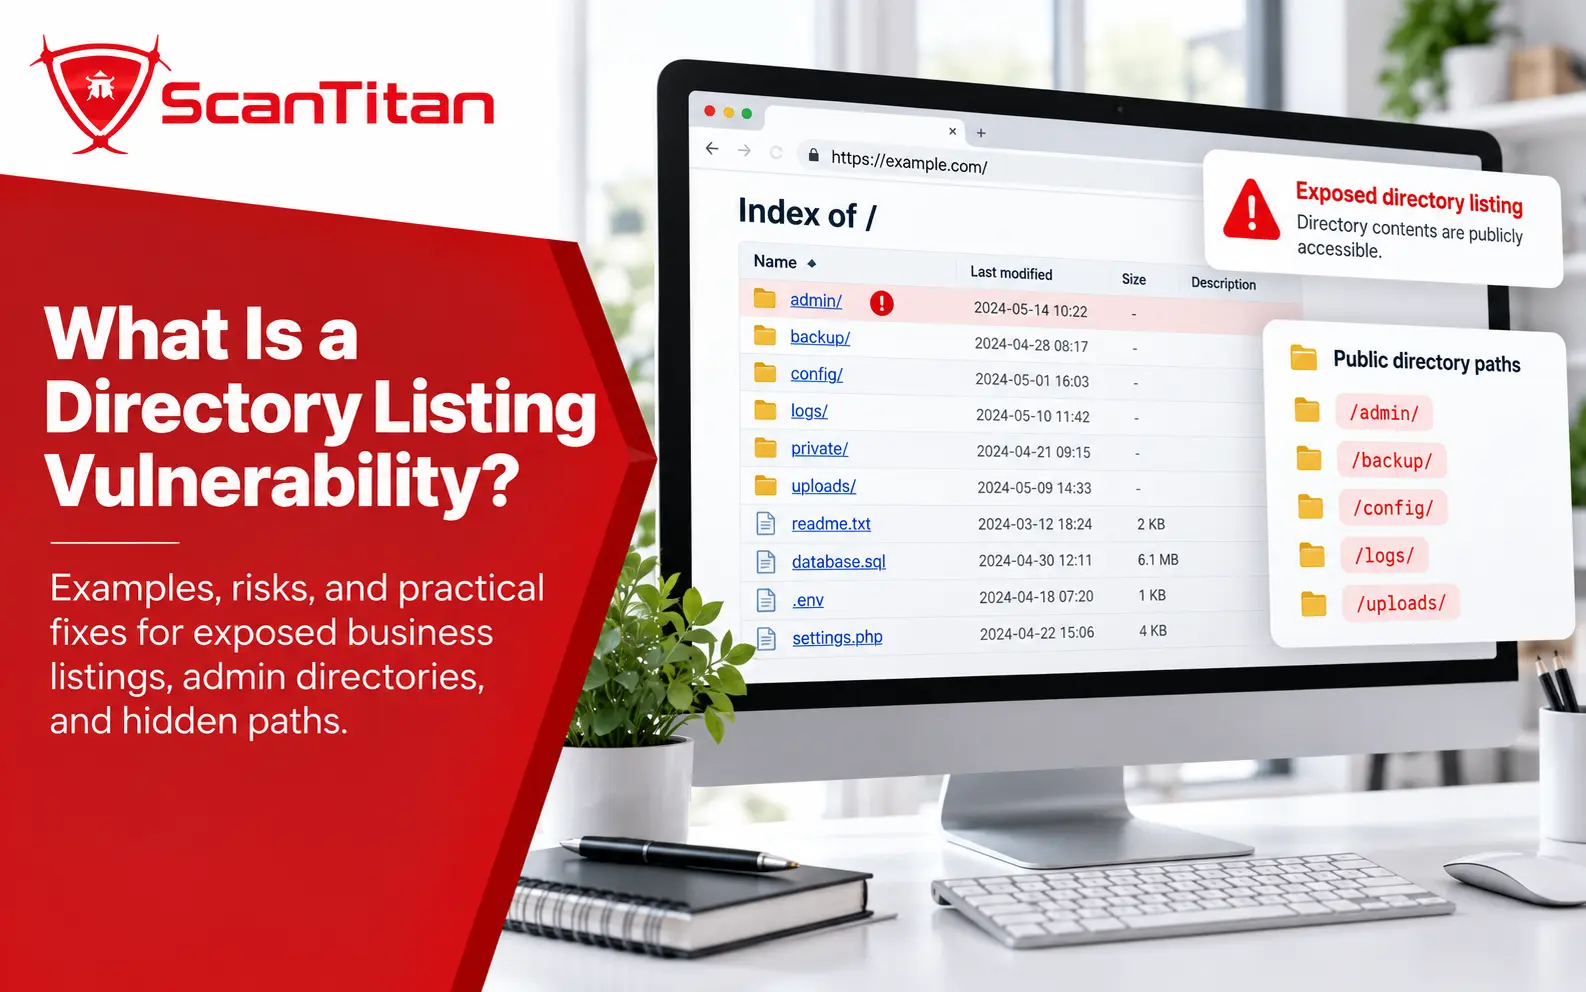
A directory listing vulnerability occurs when a web server exposes a browsable index of files and subdirectories that were not intended to be discovered this way. Instead of returning an index page or denying access, the server generates a list that can reveal filenames, backup archives, configuration files, logs, source code, database exports, or internal […]
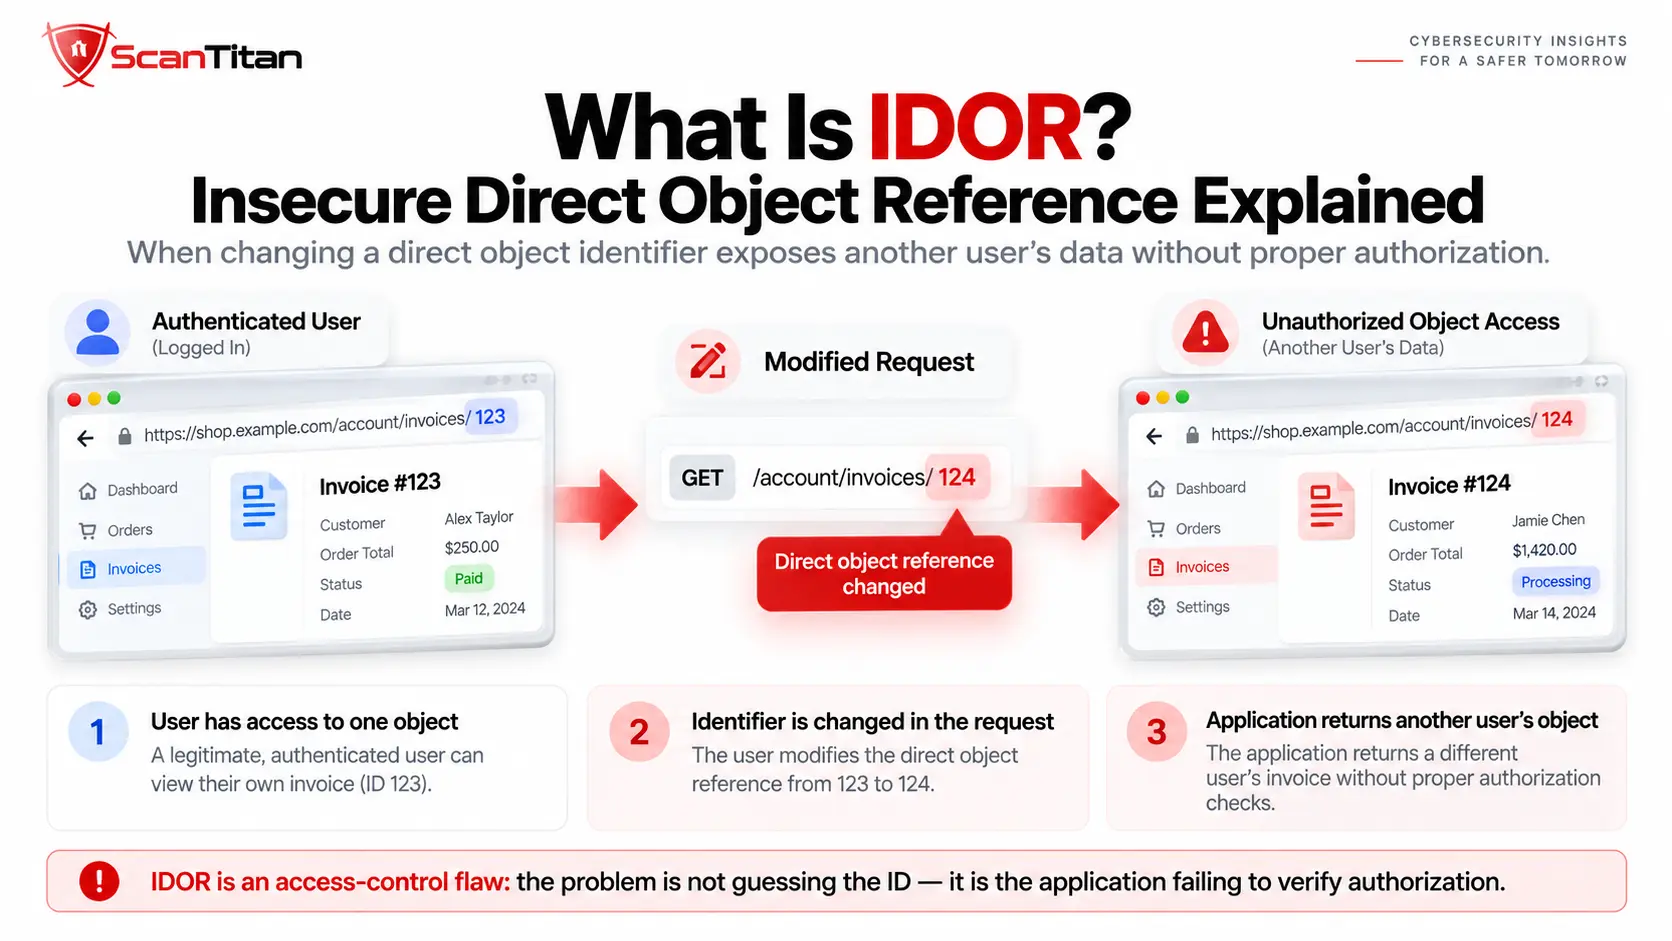
Insecure Direct Object Reference (IDOR) is an access control vulnerability in which an application uses a user-controllable reference to retrieve, change, delete, or otherwise act on an object without verifying that the requester is authorized to perform that action on that specific object.The central mistake is confusing authentication with authorization. Authentication answers “Who are you?” […]
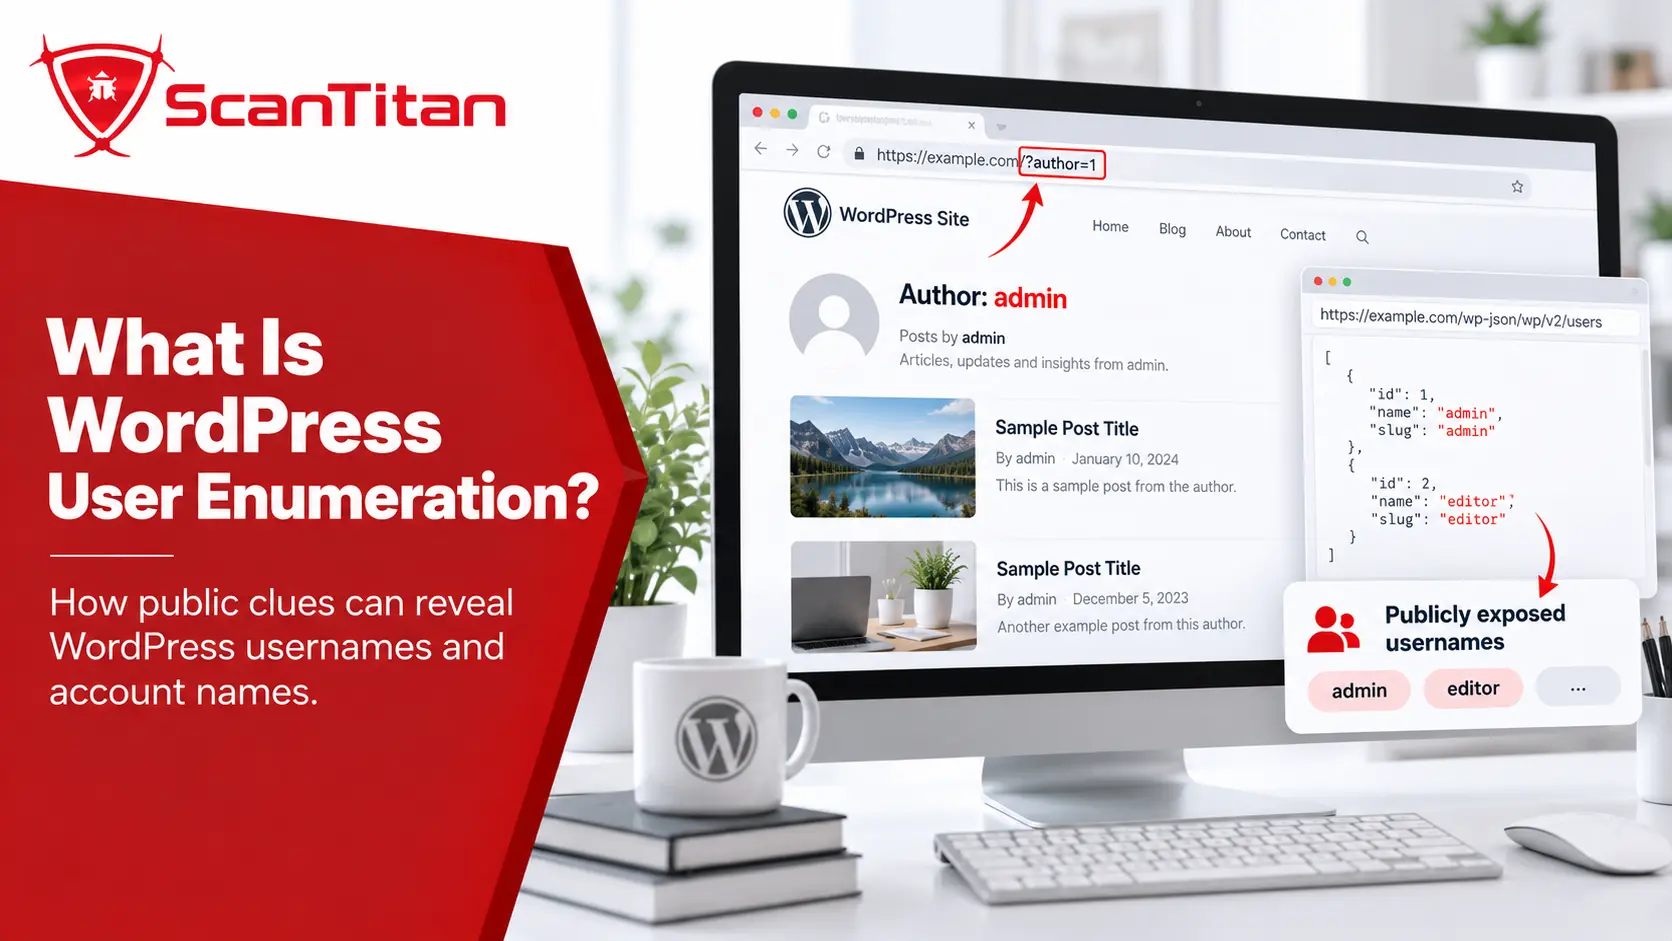
WordPress user enumeration is the process of discovering information that identifies valid WordPress accounts, such as user IDs, display names, author slugs, author URLs, or whether an account exists. WordPress can expose some of this information intentionally through author pages, REST API responses, sitemaps, and login behavior. Enumeration does not bypass authentication and does not […]
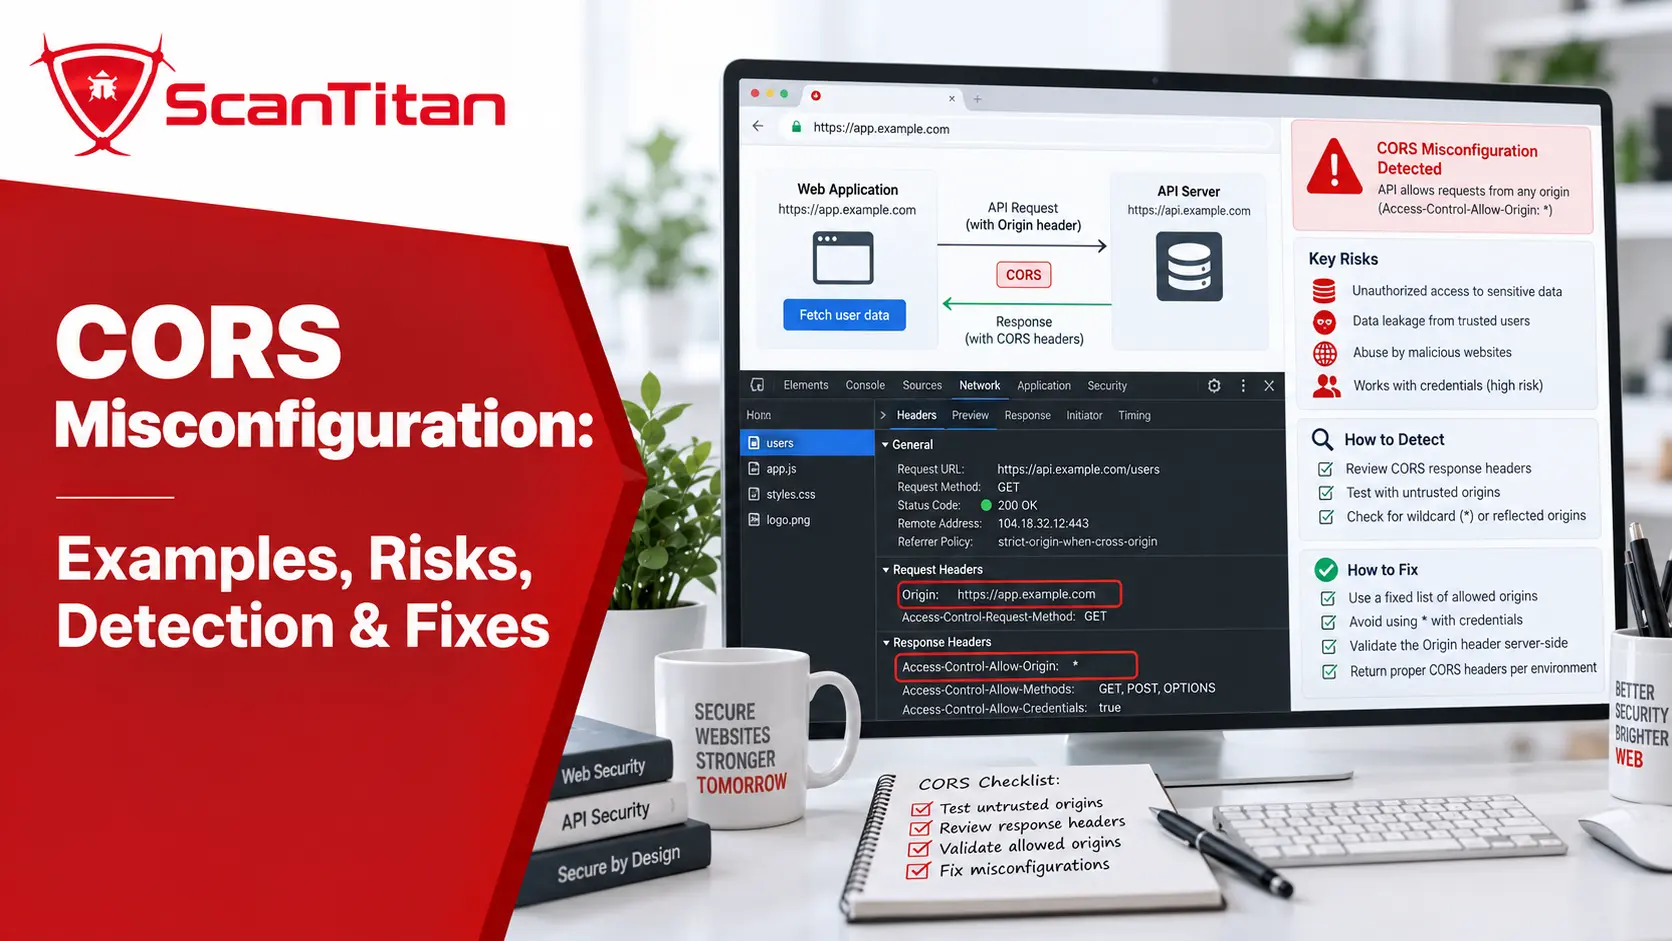
A CORS misconfiguration occurs when a web application allows an untrusted origin to read cross-origin responses that should only be available to trusted websites. Common causes include reflecting arbitrary Origin values, weak origin validation, trusting null, or allowing origins that attackers can control.Not every permissive CORS response is an exploitable vulnerability. The real risk depends […]
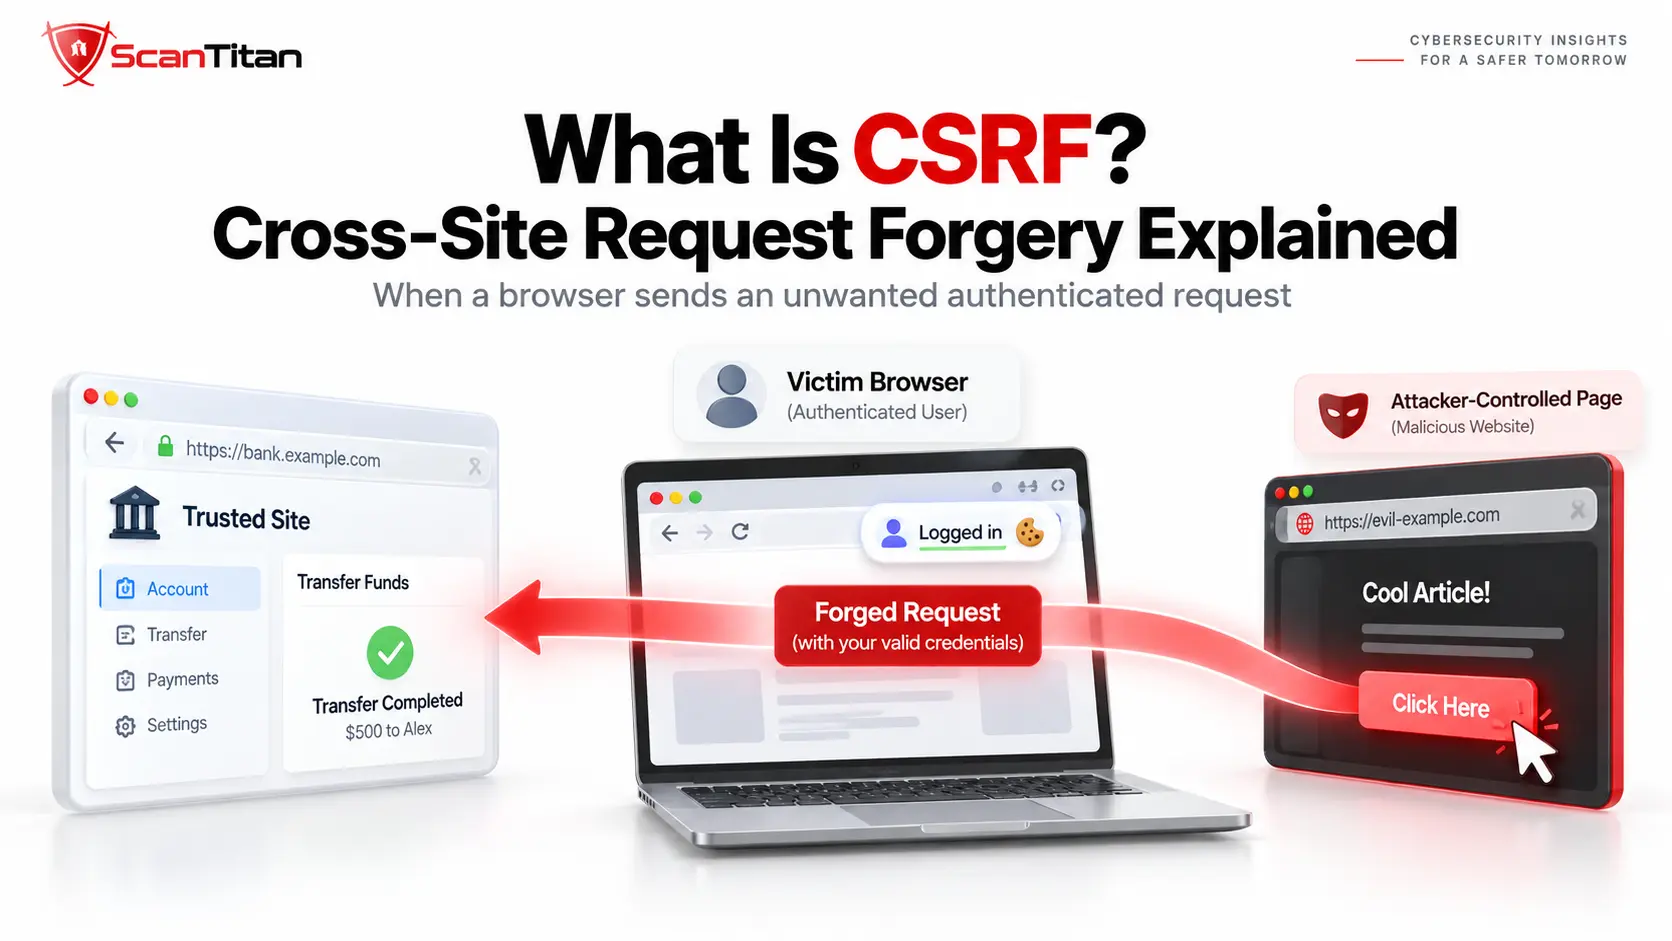
Cross-Site Request Forgery (CSRF) is a web security vulnerability in which an attacker causes a user’s browser to send an unintended request to an application that accepts the user’s automatically supplied credentials or authority. The browser may be authenticated, but the application fails to verify that the user actually intended the action.That distinction is the […]
A cloaking hack in WordPress is malicious code that shows spam to Google and a normal site to you, so the dashboard and your own browser look clean while search results fill with pharmacy or casino pages. The code checks who is asking, by user agent, IP address, referrer or login state, and serves the […]
Nulled plugins malware is malicious code hidden in a pirated copy of a premium WordPress plugin, installed by an owner who wanted it for free. The code runs with the plugin’s full permissions, so it can open a backdoor, create administrators, inject spam or switch off your security plugin. This guide shows what hides inside, […]
A site still blocklisted after cleanup is rarely a mystery. The flag stays because you are still waiting for a review, part of the infection is still there, or a different list holds the flag. Blocklists do not judge how clean you feel, only what their crawler or reviewer sees. This guide shows how long […]
Malicious JavaScript on website pages is script code that an attacker planted so it runs in your visitors’ browsers. It loads from a theme file, a database row, a third-party tag or the server itself, and it redirects traffic, steals form data or shows fake prompts. This guide shows where it hides, how to find […]
WordPress mu-plugin malware is malicious PHP placed in the wp-content/mu-plugins folder, where WordPress loads it on every request without activation, so it never shows as an active plugin. Attackers use it to load remote payloads, hide accounts, steal logins and restore deleted files. This guide shows how it hides and survives, the indicators that give […]
Hidden admin user WordPress infections are administrator accounts that exist in the database but are filtered out of the Users screen by code, so the dashboard shows nothing unusual. Attackers create one to return after cleanup. This guide shows how attackers hide the account, how to find it with direct SQL when even WP-CLI is […]
The 12 signs of website malware fall into five groups: what visitors see, what Google shows, what you see in the dashboard, what the server’s files and logs show, and what your host or email provider reports. Redirects, browser warnings and spam in search results are the most common. This guide lists the 12 signs, […]
To find a backdoor in a website, run three passes: compare every file against a clean copy, search for code that behaves like a backdoor, and trace unusual requests in your access logs. Backdoors hide in eight places, from fake core files to the database, and a scanner alone misses many of them. This guide […]
How did my website get hacked? Almost always through one of nine entry points: a vulnerable plugin or theme, stolen credentials, a nulled theme, a compromised hosting account, vulnerable custom code, exposed files, an infected admin computer, a third-party script, or weak server settings. Each one leaves different evidence in your logs and files. This […]
A seo spam hack is an attack that injects spam pages, links or redirects into your site so the attacker can rank pharmacy, casino or counterfeit-goods pages on your domain. It often stays invisible to you and the visitors you check with, while Google shows it to searchers. This guide explains how to confirm it, […]
Database malware WordPress owners miss is malicious code, links or settings stored in database rows instead of files, which is why file scanners and file restores never catch it. It shows up as injected scripts, spam links, redirects, a changed site URL or an administrator you never created. This guide explains where the infection hides, […]
WordPress malware keeps coming back when cleanup removed what you could see and left the way back in. The usual causes are a surviving backdoor, a hidden admin user, a malicious mu-plugin or cron job, a payload in the database, or the original unpatched hole. This guide shows how to tell reinfection from a new […]
12+ years in information security. Specialises in web application security, vulnerability management, and external attack surface reduction for SMB and mid-market organisations.
New CVEs, practical guides, and scan methodology updates. One email per week. No sales pitch.
No spam. Unsubscribe any time. GDPR compliant.
Editorial standards: All ScanTitan blog content is reviewed by certified InfoSec professionals before publication. Technical claims are tested against live scan results or cited from primary sources (CVE database, OWASP, NIST NVD). We do not accept sponsored posts or paid placements.
Try a free scan
Run a free vulnerability scan on your domain. No account required.