Practical security insights for teams without a SOC
No vendor fluff. No recycled threat reports. Real guidance on vulnerability scanning, malware, and attack surface management — written by practitioners.
The 12 signs of website malware fall into five groups: what visitors see, what Google shows, what you see in the dashboard, what the server’s files and logs show, and what your host or email provider reports. Redirects, browser warnings and spam in search results are the most common. This guide lists the 12 signs, […]
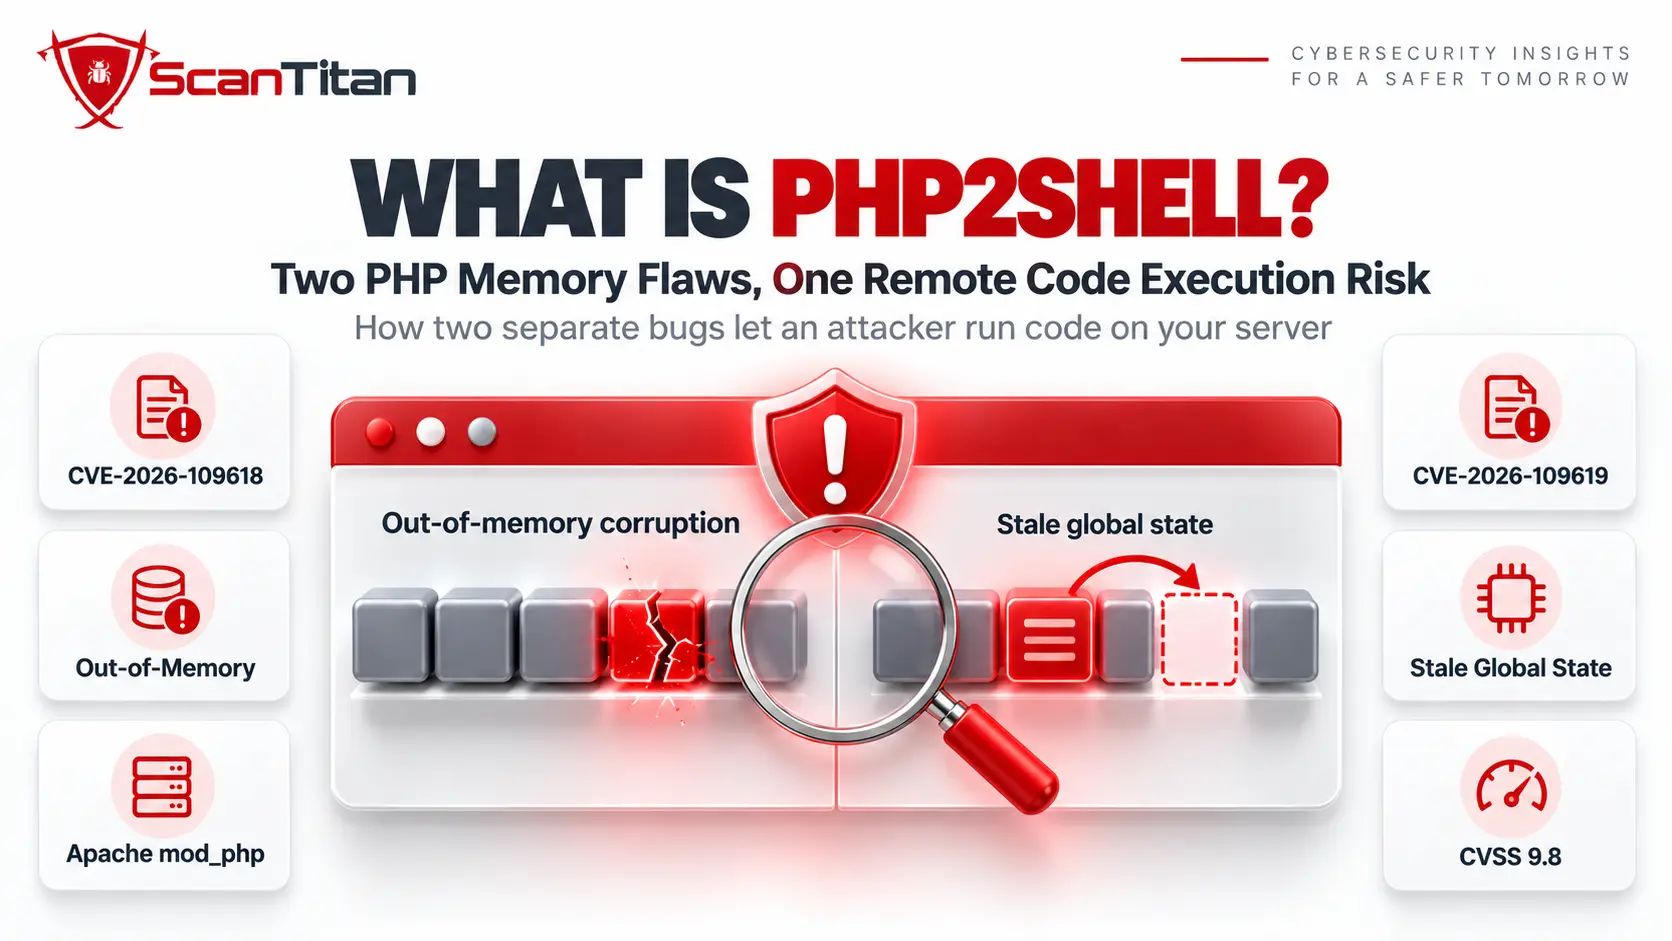
PHP2Shell is the name researchers gave to two critical PHP core flaws, CVE-2026-109618 and CVE-2026-109619, that let an unauthenticated attacker run code on a server through ordinary web requests. The PHP team shipped fixes on 21 October 2026 in versions 8.5.12, 8.4.27, 8.3.36, and 8.2.35. If your site runs PHP, which covers every WordPress, Joomla, […]
To find a backdoor in a website, run three passes: compare every file against a clean copy, search for code that behaves like a backdoor, and trace unusual requests in your access logs. Backdoors hide in eight places, from fake core files to the database, and a scanner alone misses many of them. This guide […]
How did my website get hacked? Almost always through one of nine entry points: a vulnerable plugin or theme, stolen credentials, a nulled theme, a compromised hosting account, vulnerable custom code, exposed files, an infected admin computer, a third-party script, or weak server settings. Each one leaves different evidence in your logs and files. This […]
A seo spam hack is an attack that injects spam pages, links or redirects into your site so the attacker can rank pharmacy, casino or counterfeit-goods pages on your domain. It often stays invisible to you and the visitors you check with, while Google shows it to searchers. This guide explains how to confirm it, […]
Database malware WordPress owners miss is malicious code, links or settings stored in database rows instead of files, which is why file scanners and file restores never catch it. It shows up as injected scripts, spam links, redirects, a changed site URL or an administrator you never created. This guide explains where the infection hides, […]
WordPress malware keeps coming back when cleanup removed what you could see and left the way back in. The usual causes are a surviving backdoor, a hidden admin user, a malicious mu-plugin or cron job, a payload in the database, or the original unpatched hole. This guide shows how to tell reinfection from a new […]
Obfuscated PHP malware is malicious PHP code that an attacker has scrambled so scanners and site owners cannot read it at a glance. The scrambling uses encoding, string tricks and indirect function calls, and it is the reason an infected file can look like random letters instead of a script. This guide shows how to […]
The 15 different types of malware below are the families every security guide names, and each one is explained from a site owner’s point of view: what it does to a website, where it hides and how you would notice it. A virus, a rootkit and a cryptojacker behave very differently on a web server […]
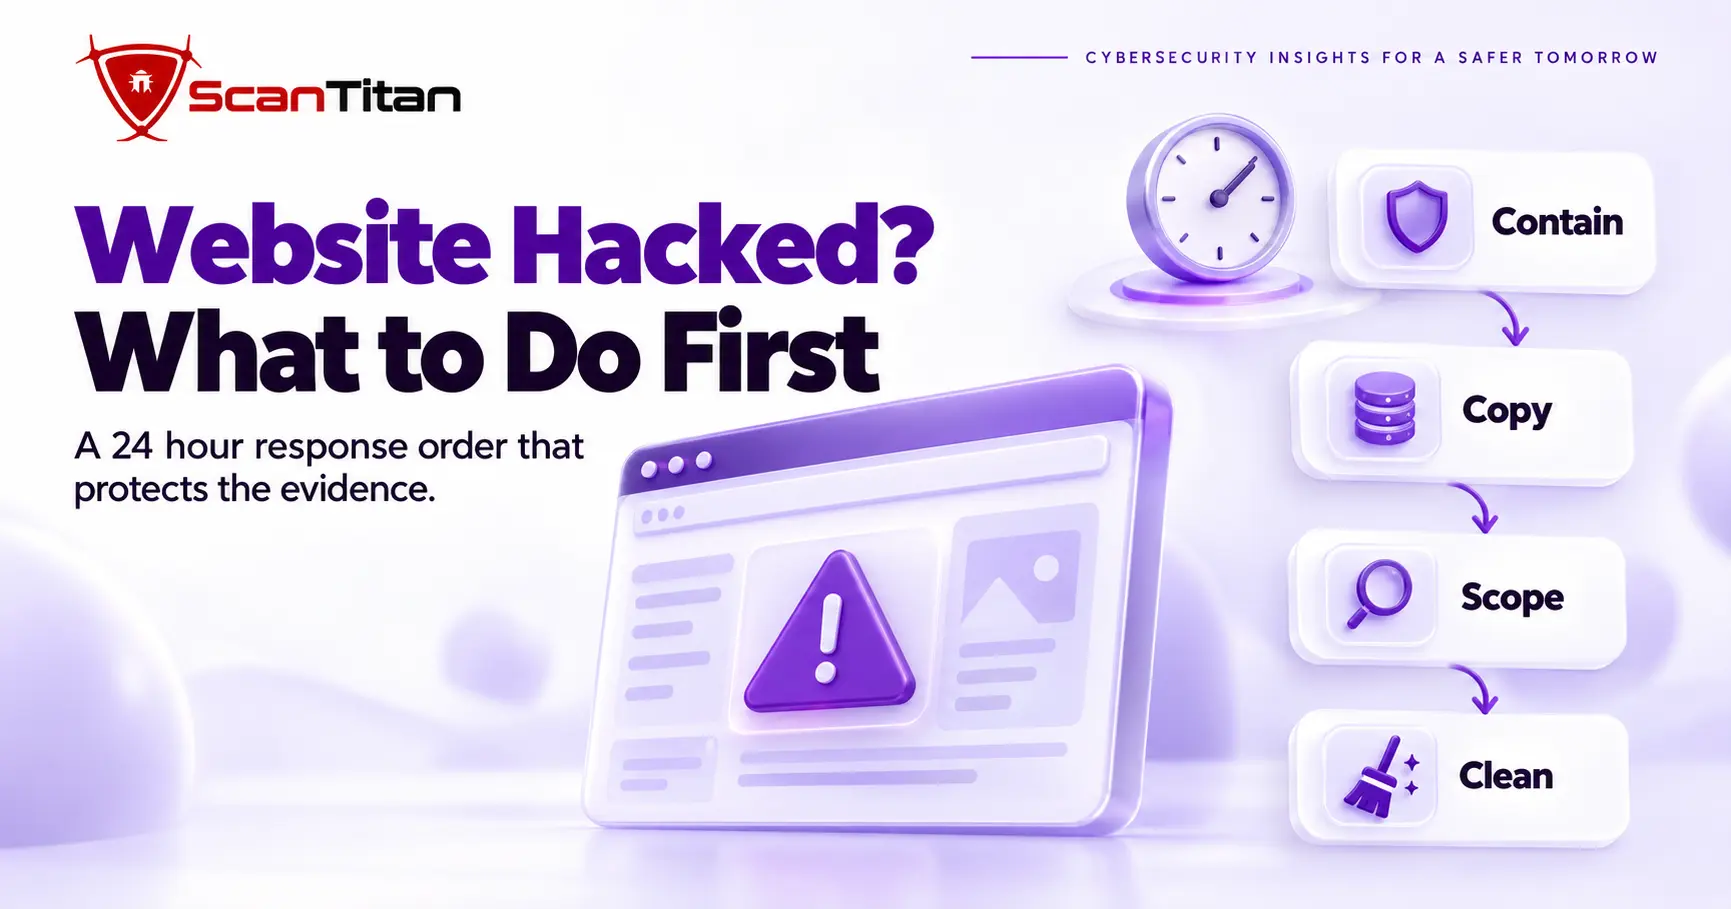
When your website is hacked, what to do first is contain it, copy it and only then clean it. This website hacked what to do guide gives the order for the first 24 hours: confirm the hack, take the site offline, rotate credentials, preserve evidence, scope the damage, choose between cleaning and restoring, and close […]
A clean malware scan is a report that says the scanner found nothing it recognizes, and it is not proof that a site is clean. When a malware scanner says clean but site hacked signs keep appearing, trust the signs, because attackers write code to pass the scanners owners run. This guide shows how to […]
A malicious redirect is code that sends visitors from your page to a spam, scam or malware site without their consent. It often fires only for some visitors, which is why owners miss it, and it usually sits in the .htaccess file, a theme file, a JavaScript file or the database. Attackers plant it after […]
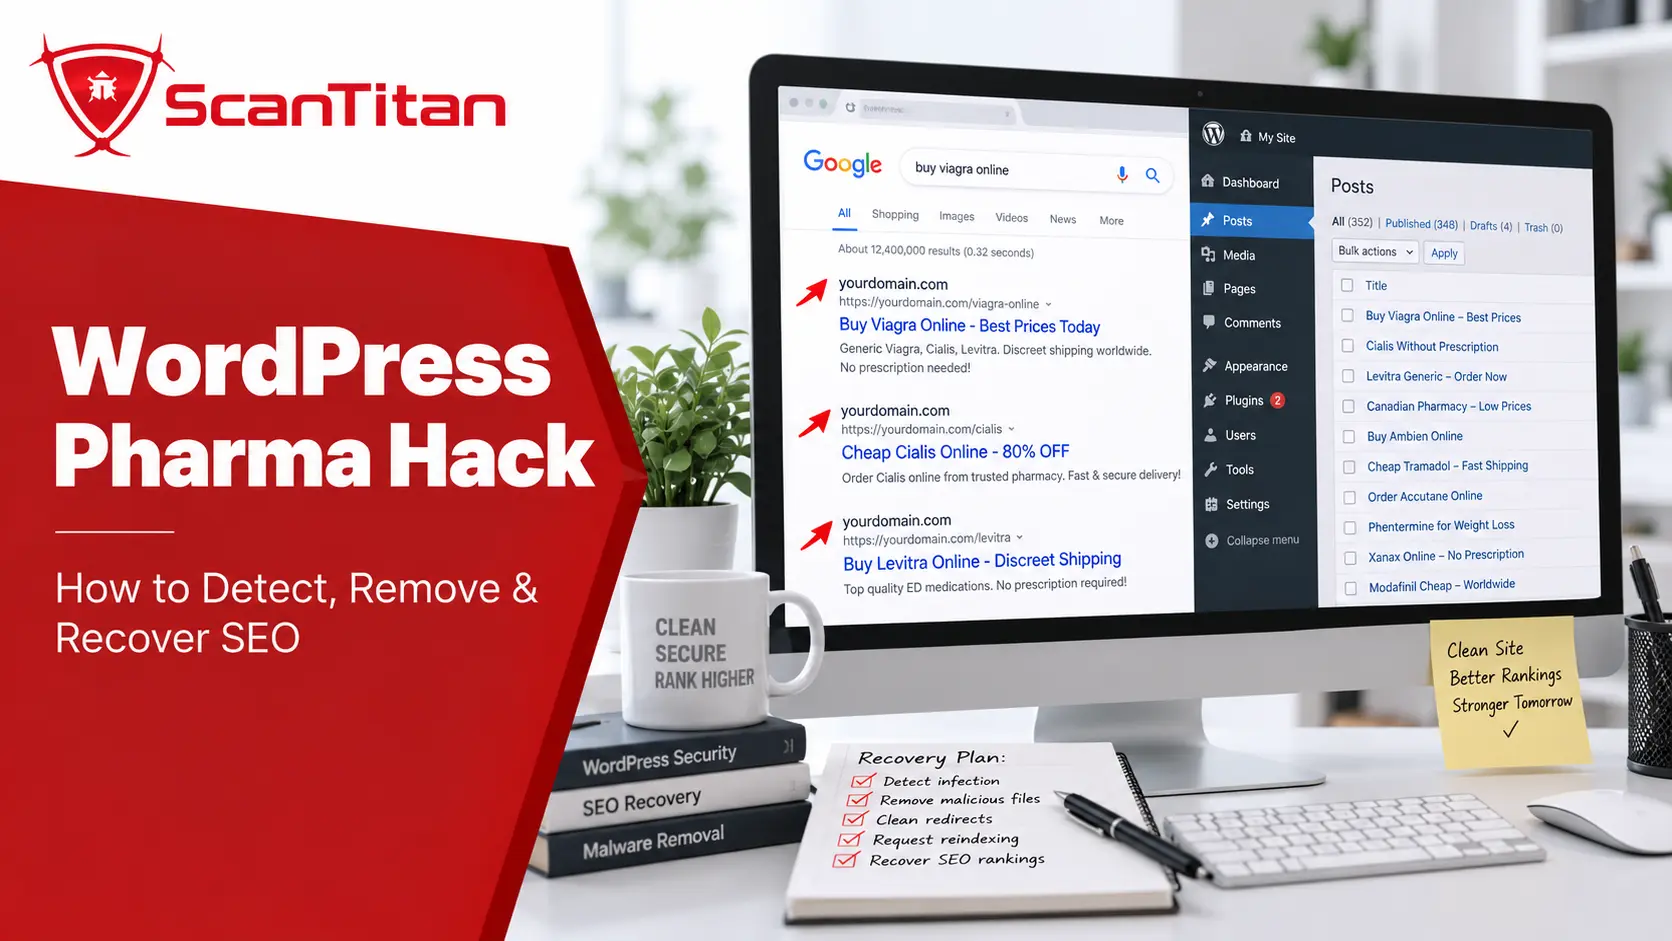
A WordPress pharma hack is a post-compromise SEO spam infection that adds pharmaceutical keywords, links, pages, redirects, or hidden content to a WordPress website without the owner’s permission. It is also commonly called a Viagra hack, pharmaceutical spam hack, or pharma SEO spam.The infection can be confusing because the website may look normal when you […]
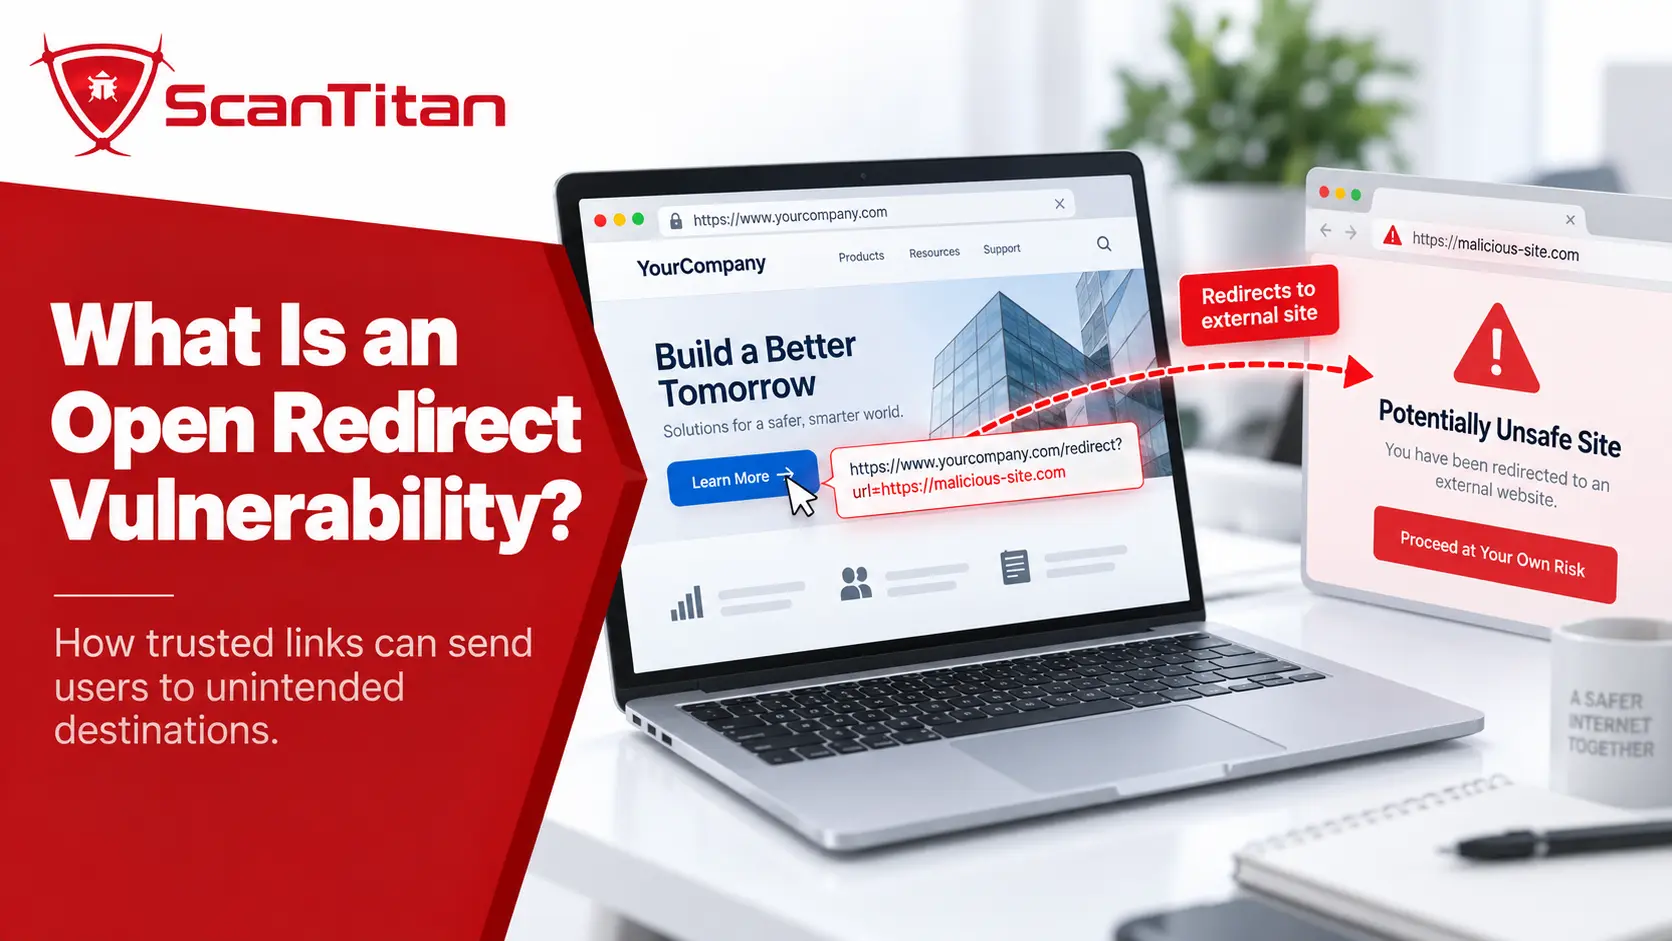
An open redirect vulnerability occurs when a web application lets attacker-controlled input determine where a user is redirected without sufficiently restricting the final destination. An attacker can then create a link that begins on a legitimate domain but sends the victim to an external site chosen by the attacker.The simplest impact is phishing: the trusted […]
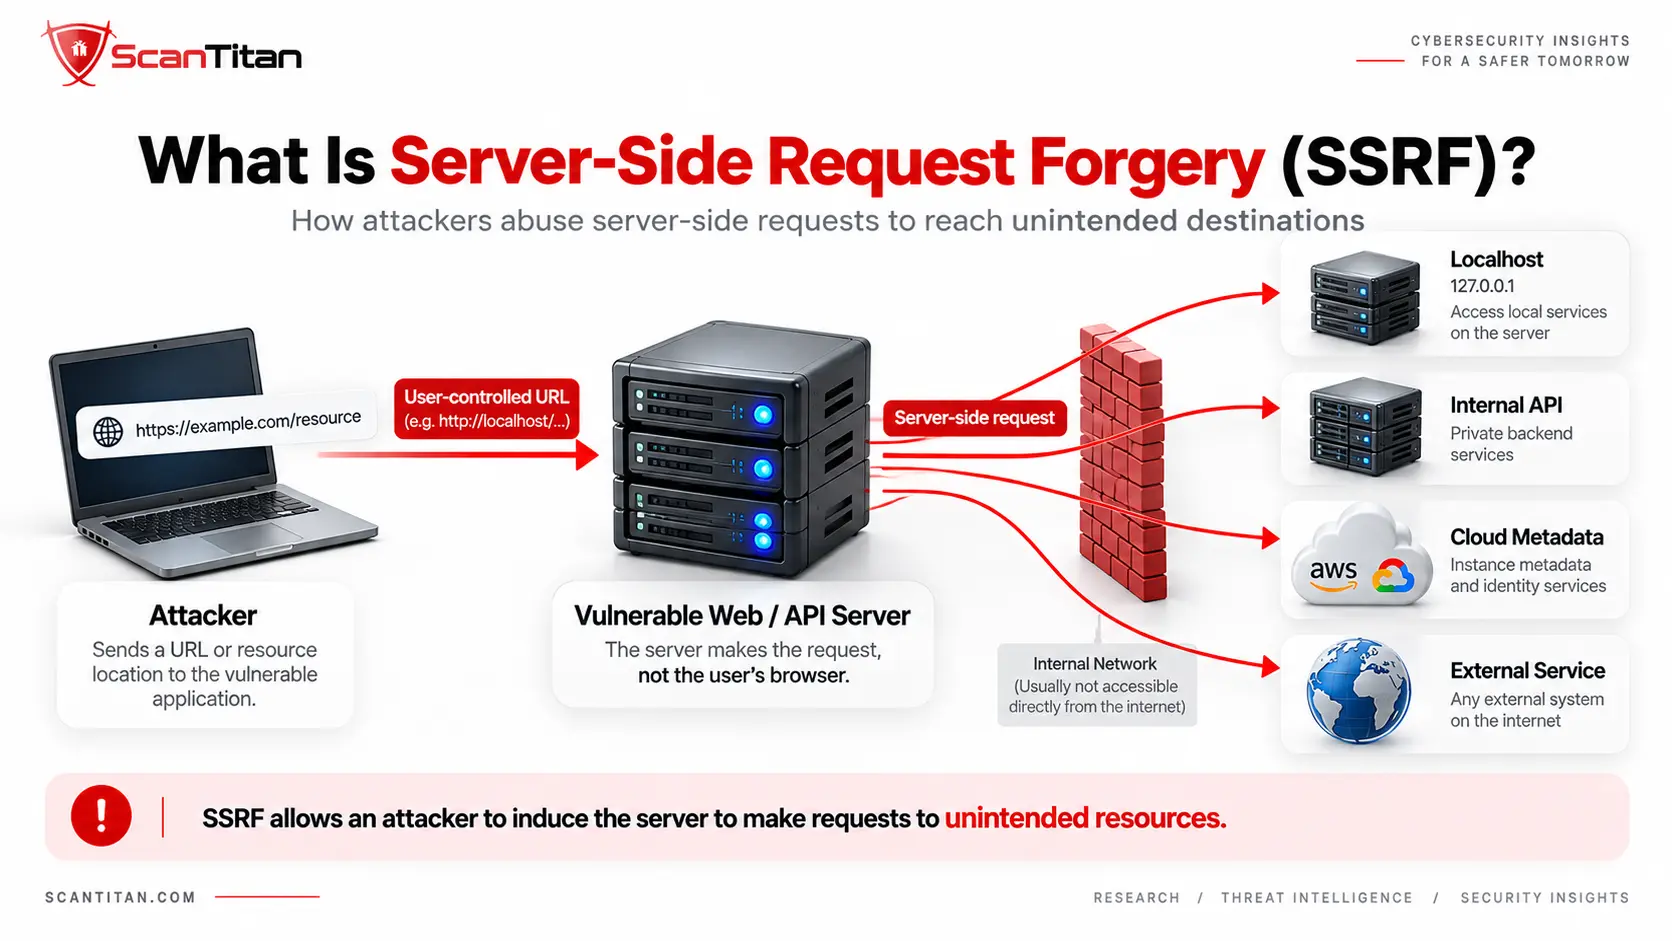
Server-Side Request Forgery (SSRF) is a web application security vulnerability in which attacker-controlled input causes a server-side component to send a network request to an unintended destination. The defining characteristic is that the sensitive request originates from the server, not from the attacker’s browser.That distinction matters because an application server may be able to reach […]
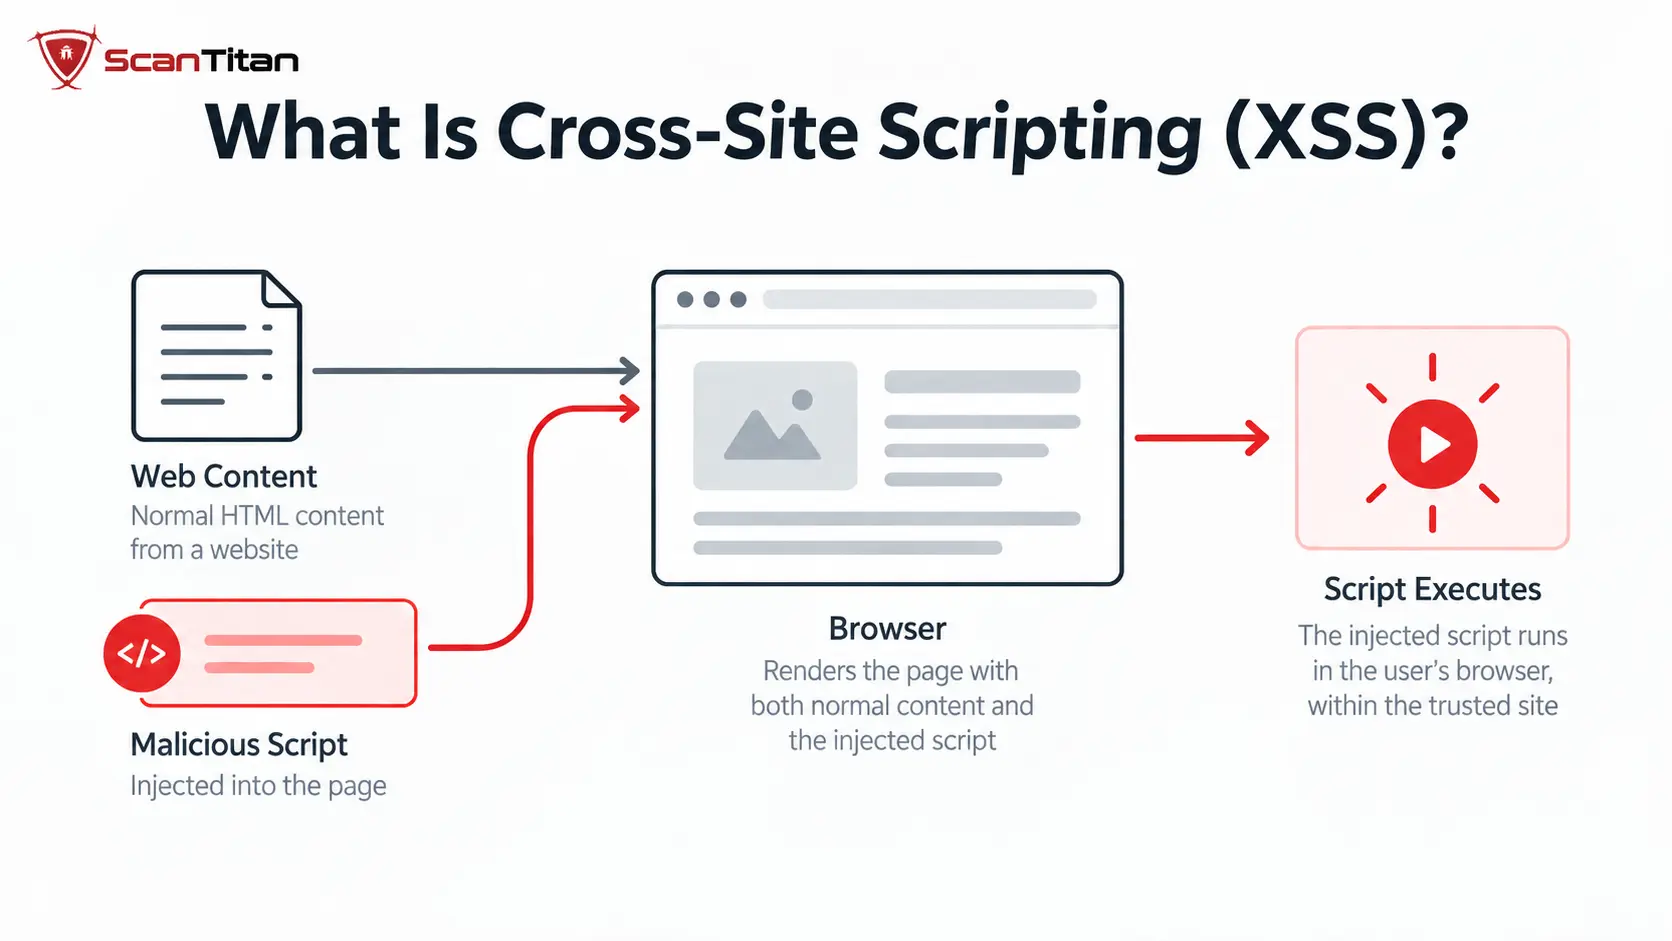
Cross-site scripting (XSS) is a web application vulnerability that allows untrusted data to reach a browser in a context where the browser interprets it as executable code instead of ordinary content. The attacker does not need to compromise the browser itself. The vulnerable website delivers or processes the attacker-controlled content in a way that makes […]
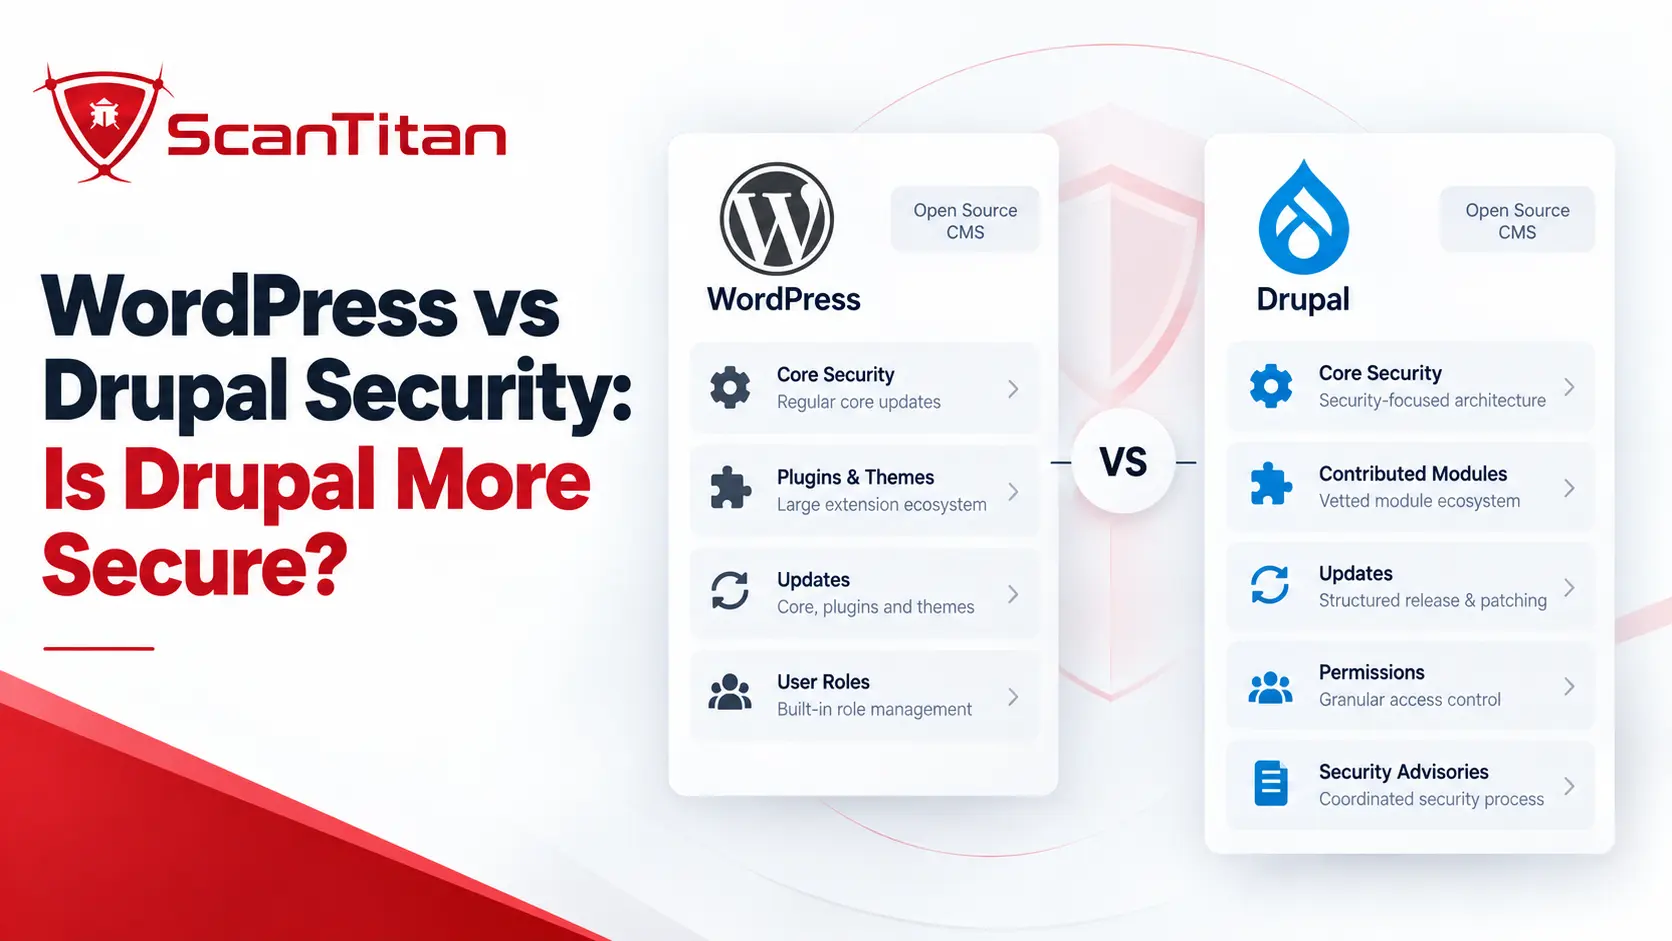
WordPress vs Drupal security is not as simple as comparing vulnerability counts. Drupal generally provides stronger security and governance defaults for complex, multi-user websites, especially around permissions, configuration management, and controlled deployments. WordPress core also has a mature security process and stronger native update automation, but its enormous plugin and theme ecosystem creates more third-party […]
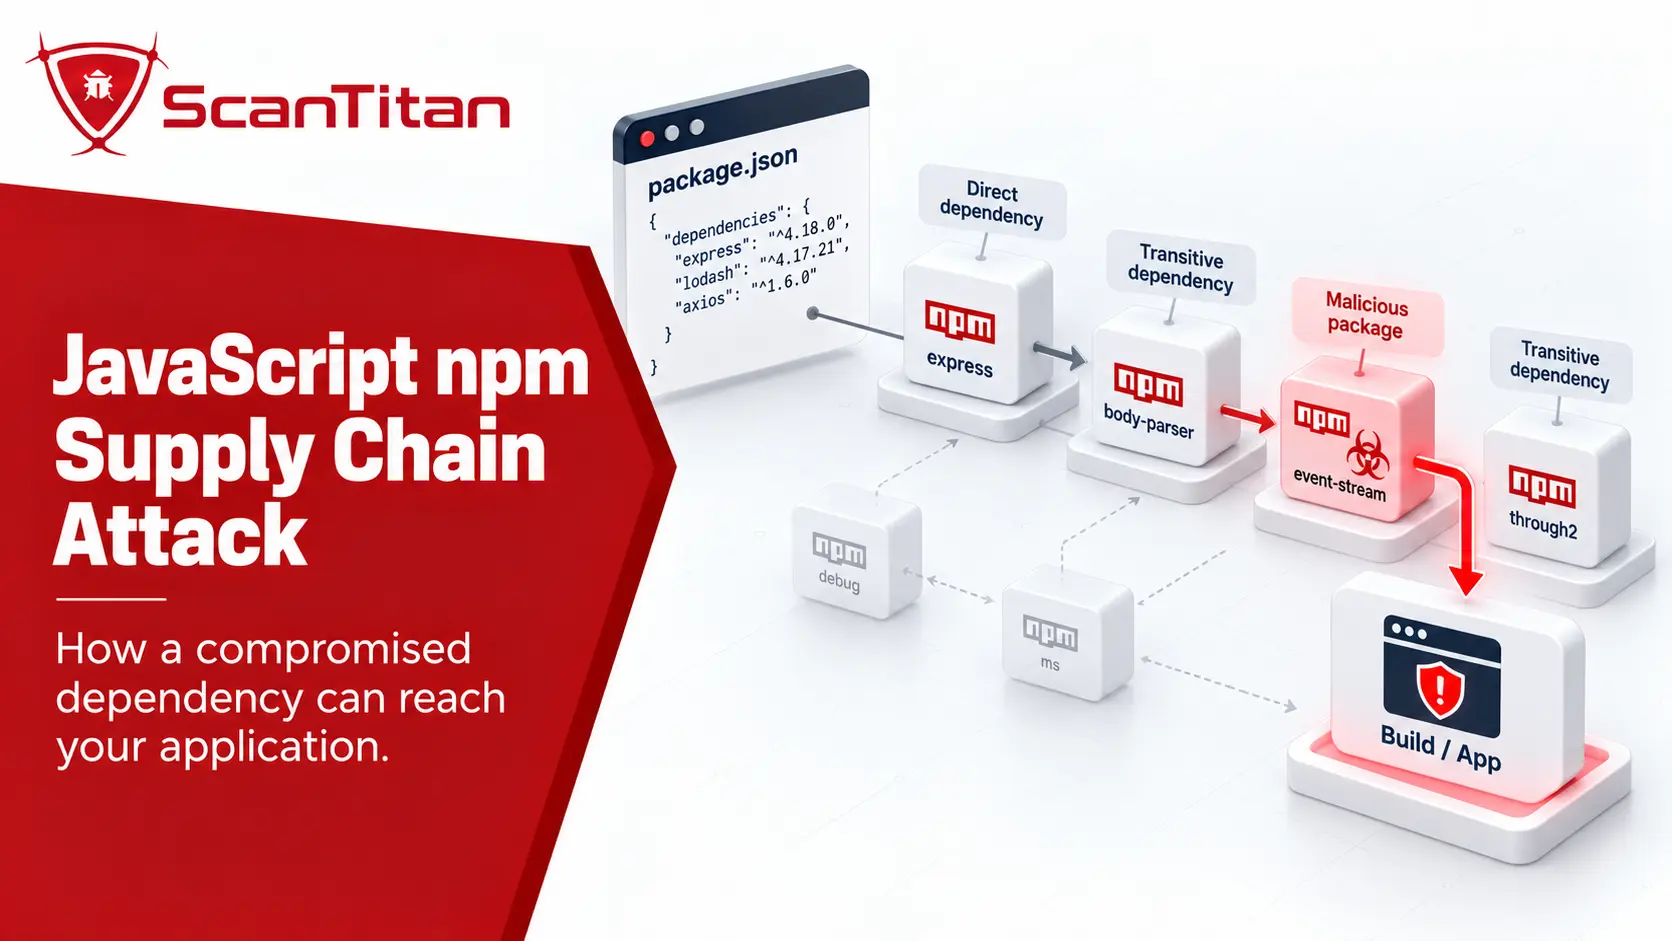
A JavaScript npm supply chain attack targets the software and infrastructure between an npm package maintainer and the application that eventually installs that package. Instead of exploiting a flaw in your own JavaScript first, an attacker may compromise a trusted package, publish a lookalike dependency, abuse package resolution, steal publishing credentials, or execute malicious code […]
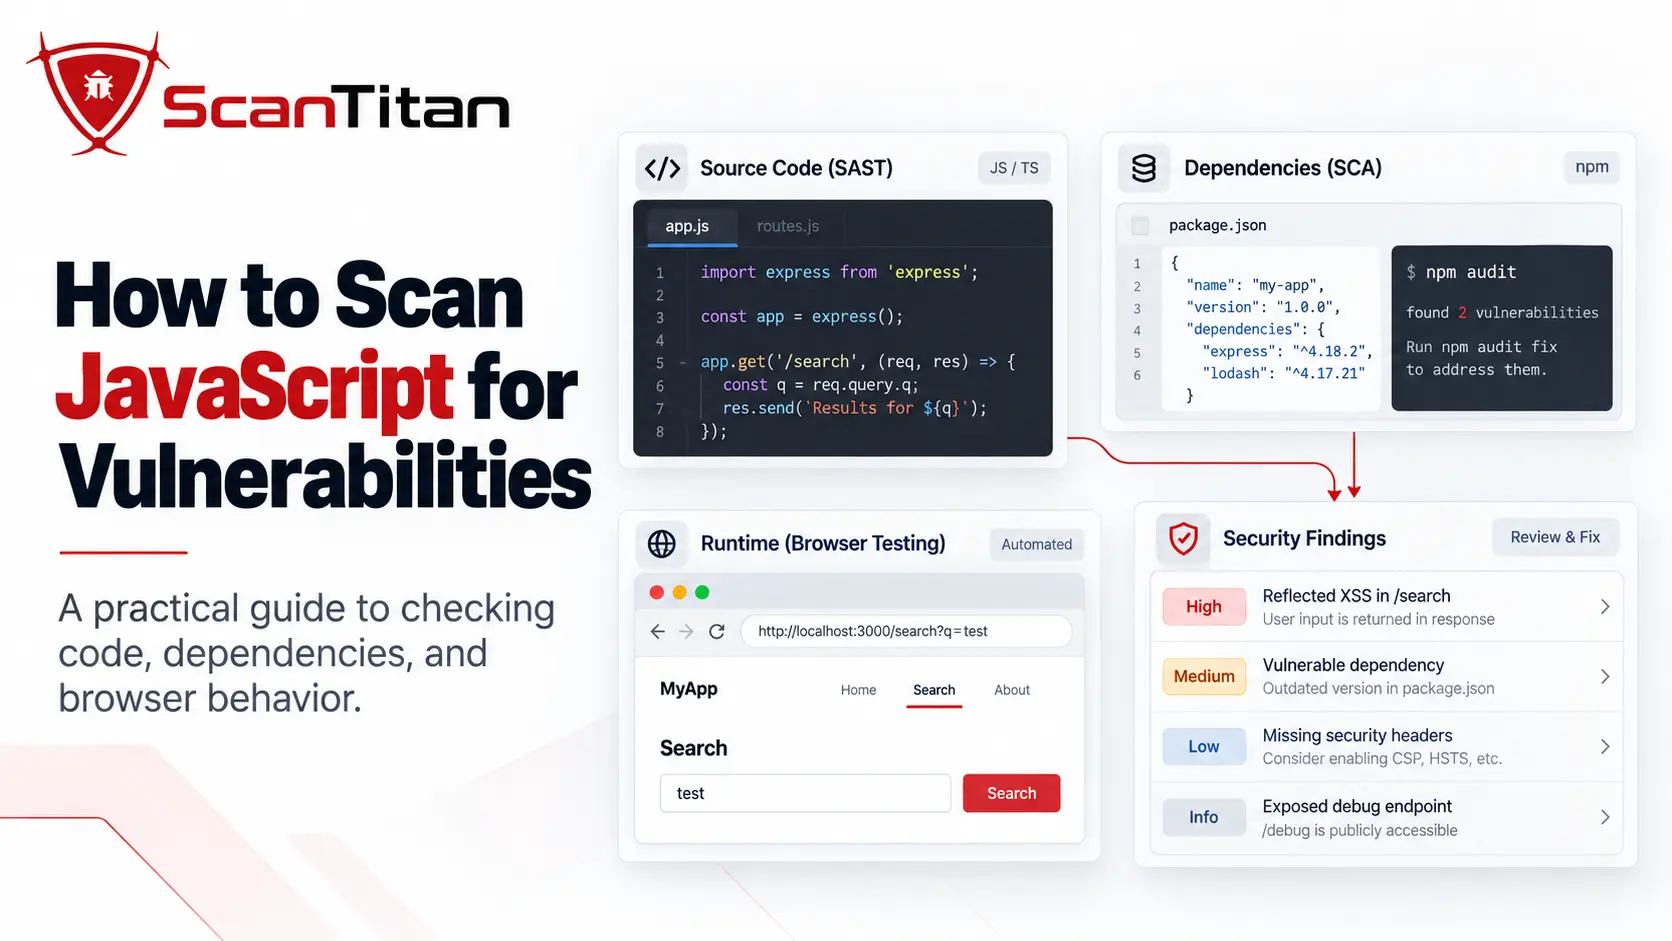
If you want to know how to scan JavaScript for vulnerabilities, do not rely on a single security check. A modern JavaScript application can contain weaknesses in the code your team writes, known vulnerabilities in npm dependencies, and security issues that appear only after the application runs in a browser. A useful JavaScript security assessment […]
If you want to know how to scan an IP address for vulnerabilities, the process goes beyond checking whether a few ports are open. A proper assessment verifies the correct and authorized target, identifies reachable TCP and relevant UDP services, fingerprints the software behind them, runs vulnerability-specific checks, validates important findings, prioritizes confirmed weaknesses, applies […]
An IP vulnerability scan checks a specific IP address for security weaknesses that can be detected from the scanner’s location. It identifies reachable ports and services, gathers evidence about the software or configuration behind them, and checks that evidence for known vulnerabilities and security issues. This matters because internet-facing services remain an important route into […]
API security testing is the process of checking application programming interfaces for vulnerabilities, misconfigurations, authorization failures, unsafe input handling, and business-logic weaknesses before attackers can exploit them. Effective testing combines code analysis, dynamic scanning, fuzzing, specification-based testing, and human review across development and production. This guide explains what to test, which methods and tools to […]
By Obaida Al-Sulaiman, Information Security Manager (CISSP, GXPN, GWAPT). Reviewed September 2026. REST API security is the set of methods and controls that protect RESTful APIs from unauthorized access, data theft, and abuse. It spans authentication, authorization, encryption, rate limiting, inventory, and continuous testing. In Salt Security’s Q1 2025 survey, 99 percent of respondents said […]
API fuzzing is an automated security testing technique that floods your API endpoints with malformed, random, and unexpected inputs to find the bugs and vulnerabilities that normal testing never triggers. Instead of checking whether an endpoint returns the right answer for valid data, an API fuzzer asks what breaks when the data is wrong. This […]
The 12 signs of website malware fall into five groups: what visitors see, what Google shows, what you see in the dashboard, what the server’s files and logs show, and what your host or email provider reports. Redirects, browser warnings and spam in search results are the most common. This guide lists the 12 signs, […]
To find a backdoor in a website, run three passes: compare every file against a clean copy, search for code that behaves like a backdoor, and trace unusual requests in your access logs. Backdoors hide in eight places, from fake core files to the database, and a scanner alone misses many of them. This guide […]
How did my website get hacked? Almost always through one of nine entry points: a vulnerable plugin or theme, stolen credentials, a nulled theme, a compromised hosting account, vulnerable custom code, exposed files, an infected admin computer, a third-party script, or weak server settings. Each one leaves different evidence in your logs and files. This […]
A seo spam hack is an attack that injects spam pages, links or redirects into your site so the attacker can rank pharmacy, casino or counterfeit-goods pages on your domain. It often stays invisible to you and the visitors you check with, while Google shows it to searchers. This guide explains how to confirm it, […]
Database malware WordPress owners miss is malicious code, links or settings stored in database rows instead of files, which is why file scanners and file restores never catch it. It shows up as injected scripts, spam links, redirects, a changed site URL or an administrator you never created. This guide explains where the infection hides, […]
WordPress malware keeps coming back when cleanup removed what you could see and left the way back in. The usual causes are a surviving backdoor, a hidden admin user, a malicious mu-plugin or cron job, a payload in the database, or the original unpatched hole. This guide shows how to tell reinfection from a new […]
Obfuscated PHP malware is malicious PHP code that an attacker has scrambled so scanners and site owners cannot read it at a glance. The scrambling uses encoding, string tricks and indirect function calls, and it is the reason an infected file can look like random letters instead of a script. This guide shows how to […]
The 15 different types of malware below are the families every security guide names, and each one is explained from a site owner’s point of view: what it does to a website, where it hides and how you would notice it. A virus, a rootkit and a cryptojacker behave very differently on a web server […]
When your website is hacked, what to do first is contain it, copy it and only then clean it. This website hacked what to do guide gives the order for the first 24 hours: confirm the hack, take the site offline, rotate credentials, preserve evidence, scope the damage, choose between cleaning and restoring, and close […]
A clean malware scan is a report that says the scanner found nothing it recognizes, and it is not proof that a site is clean. When a malware scanner says clean but site hacked signs keep appearing, trust the signs, because attackers write code to pass the scanners owners run. This guide shows how to […]
A malicious redirect is code that sends visitors from your page to a spam, scam or malware site without their consent. It often fires only for some visitors, which is why owners miss it, and it usually sits in the .htaccess file, a theme file, a JavaScript file or the database. Attackers plant it after […]
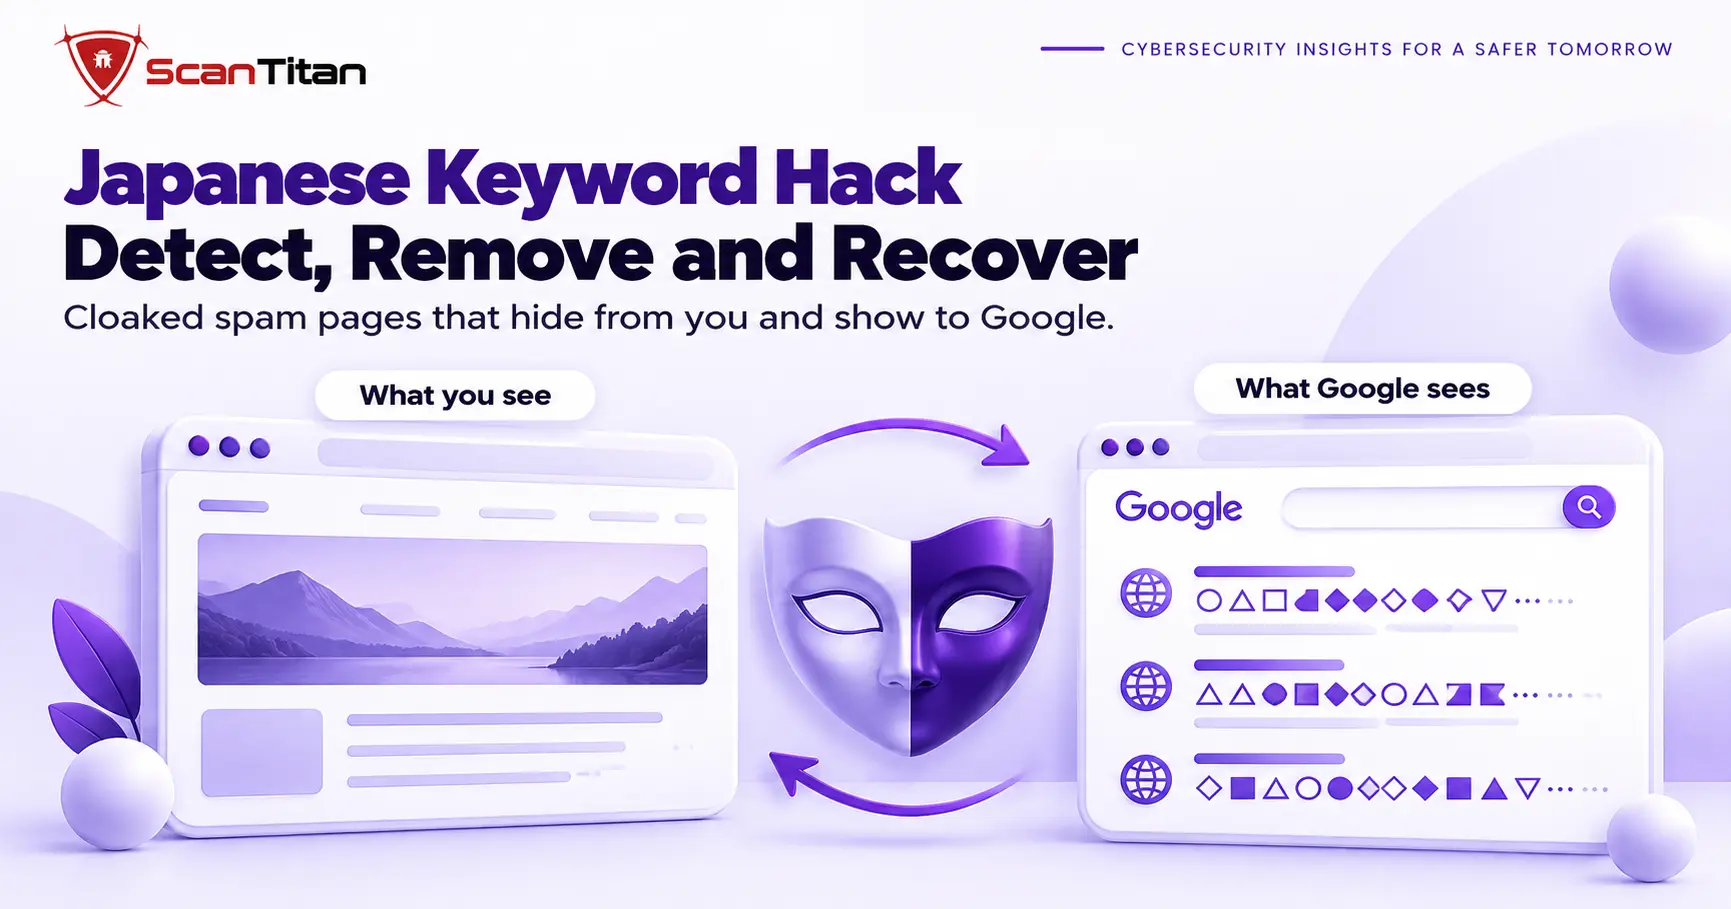
The Japanese keyword hack is a form of SEO spam hack in which attackers inject thousands of auto-generated Japanese pages into a compromised website. It works by cloaking: Google and search visitors see the spam, while you see your normal site. Owners usually find out from Japanese results in search or a sudden jump in […]
12+ years in information security. Specialises in web application security, vulnerability management, and external attack surface reduction for SMB and mid-market organisations.
New CVEs, practical guides, and scan methodology updates. One email per week. No sales pitch.
No spam. Unsubscribe any time. GDPR compliant.
Editorial standards: All ScanTitan blog content is reviewed by certified InfoSec professionals before publication. Technical claims are tested against live scan results or cited from primary sources (CVE database, OWASP, NIST NVD). We do not accept sponsored posts or paid placements.
Try a free scan
Run a free vulnerability scan on your domain. No account required.